
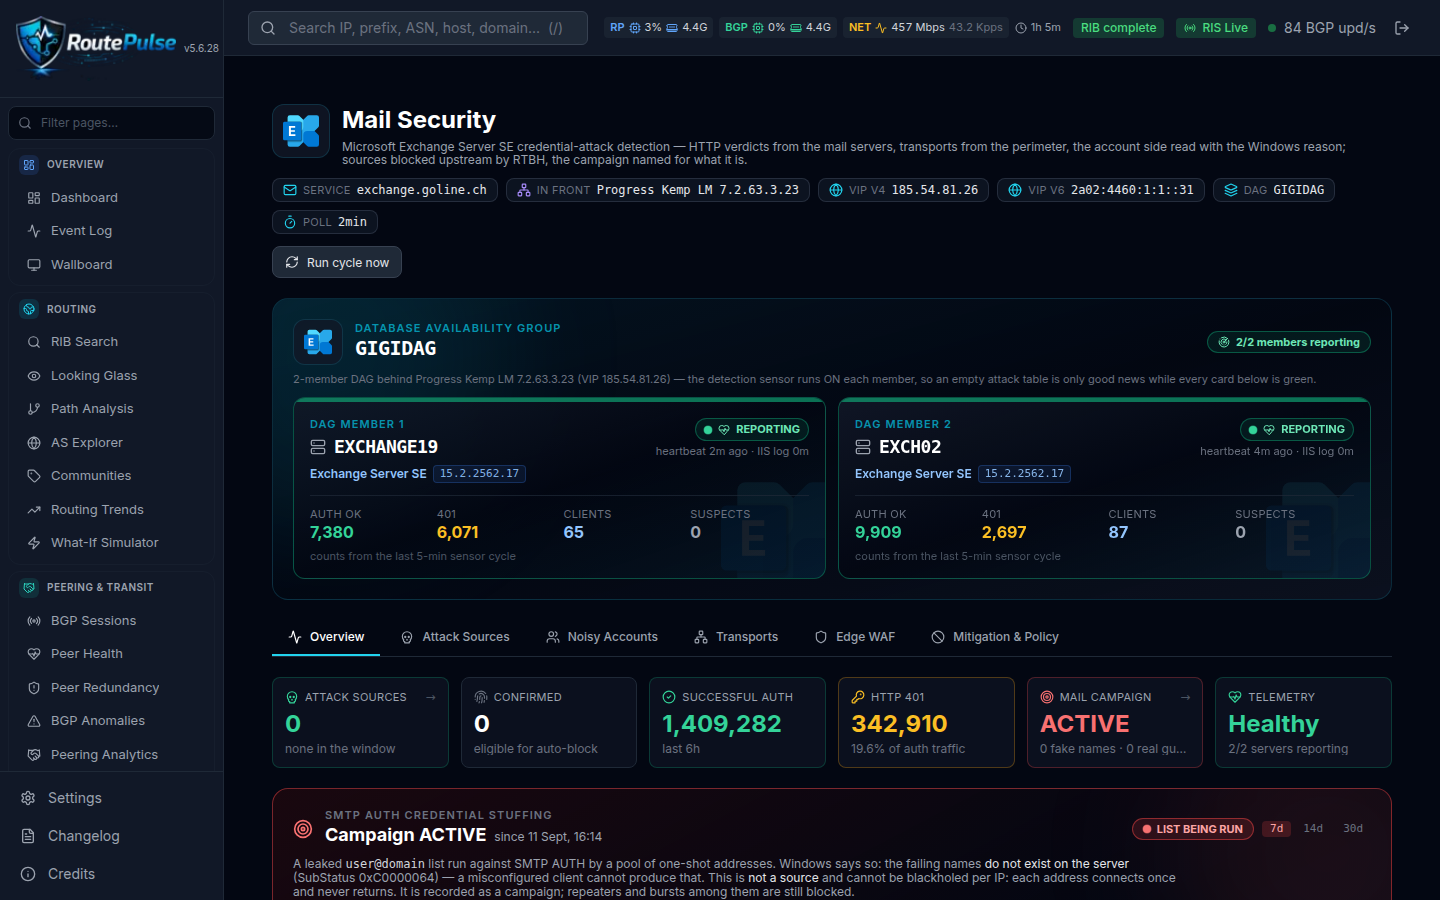
Mail Security — Exchange Credential Attacks Seen Across Every Transport, Not One Log
Credential attacks on Exchange arrive through OWA, EWS, ActiveSync, IMAP, POP and SMTP AUTH at once, and each transport logs differently — or not at all. RoutePulse correlates the Exchange server’s own authentication telemetry with the edge load balancer and the firewall into one picture per source: failed logins, usernames tried, the zero-success criterion that separates an attacker from a misconfigured client, and distributed sprays that hide below every per-IP threshold.
A confirmed source is blocked at the edge and, when it keeps hammering, blackholed on the core routers with a strike-escalated TTL; the response is audited, notified and reported to AbuseIPDB. Every decision is explained in plain language on the page, including the sources the collateral guard deliberately did not block.