
RoutePulse — Complete BGP Analytics & Security Intelligence Platform

RoutePulse sees both — and acts with mathematical proof.
18-model ML ensemble feeding an 8-gate Conviction Engine: SPRT + Thompson Sampling + Conformal Prediction. First BGP+security platform with provable false-positive bounds. 47 MITRE ATT&CK playbooks. CAD compositional detector (90% noise reduction). QR-scannable LoA. NIS2/DORA/AI-Act dossier.
BGP hijack confirmed by traffic shift? Blackholed in <3 s. Encrypted C2 over QUIC? Flagged. DGA botnet fan-out? Contained. Multi-modal FortiGate anomaly? CAD 90% noise-cut.
18 ML models. 8-gate Conviction Engine. 5-pillar threat scoring. Conformal Prediction with provable FDR bounds. 84% false-positive reduction on production AS202032.
Watch the trailer (3:48, 19 screens)
13 production screens, US English narration: the NOC first — traffic, data coherence, BGP anomalies, RPKI — then the SOC: War Room, RA-VPN siege ladder, Cloudflare Magic Transit, mitigations, identity, ML brain, and the compliance evidence.
Watch the full tour (6:54, 37 screens)
Every page of the platform, in the same order: the NOC, the SOC, then the evidence. US English narration.
From the first suspicious flow to BGP blackhole
in under 3 seconds — fully autonomous.
NOC + SOC Unified Console
Your NOC sees a route flap. Your SOC sees a threat actor. RoutePulse sees both — and correlates them. BGP hijack + traffic shift = confirmed attack, not two separate tickets in two different tools.
AI-Powered SOC Analyst
Works 24/7 alongside your team — investigating every critical alert, correlating 39 threat feeds, and orchestrating a 18-model ML pipeline across 56+ anomaly types.
8-Gate Pipeline: Detection to Blackhole in <3s
IP validation → Infrastructure check → ASN whitelist (22 CDN) → Volume gate → ThreatClassifier (10 classes) → TOCTOU lock → Router SSH → Claude AI Arbiter. Every gate must pass. Zero collateral damage on production routers.
Built for the scale of a full Internet routing table — 1.28M+ prefixes, 870K+ hosts, 40K+ flows/min — with 180 days of instant-query retention. No sampling. No blind spots. No compromises.
Why NOC & SOC Teams Choose RoutePulse
18-Model ML Ensemble
3-tier architecture: Core (Baseline, IsoForest, Markov, K-Means, Holt-Winters, Latency, ThreatIntel, Temporal, Beaconing, GraphChange), Specialized (CarpetBomb, DnsTunnel, Reflector), Tier 1 Expansion (QUIC Anomaly, Protocol Mismatch, BGP-Traffic Correlation, DGA/FastFlux, Encrypted C2 Profiler). Self-tuning via TP/FP feedback loops with precision-based adaptive learning. 56+ anomaly detection types across 8 MITRE ATT&CK categories.
Autonomous AI SOC Analyst (ANIE)
6-layer AI engine: L1 MITRE ATT&CK enrichment, L2 autonomous investigation, L3 continuous threat hunting, L4 ML orchestration, L5 self-tuning, L6 persistent network memory. Budget-aware at $1–3/day after 4-layer digest optimization.
5-Pillar Unified Threat Score
183-point composite across Cyber Events (48pt), Behavioral (40pt), ML Ensemble (30pt), External Intelligence (40pt), and FeedIntel (25pt). 15 correlation rules auto-classify severity and trigger mitigation.
52K+ Indicators, Sub-Microsecond Lookup
39 threat feeds loaded into Bloom filter for <1μs correlation against every flow. MISP integration (4,894 events, 9.9M attributes), AbuseIPDB, Shodan, and commercial blocklists in real time.
1,300x Query Acceleration
Columnar analytics engine with 17 materialized views and 9.5x compression. TopTalkers from 17s to <1s, IP lookups from 8s to 98ms. 180 days of full retention at 3.5TB, instantly queryable.
Automated Blackhole Mitigation
RTBH (Remote Triggered Black Hole) for IPv4 (/32, /24) and IPv6 (/128) via persistent SSH to Juniper MX and Huawei NetEngine routers. BGP community 65535:666 upstream signaling to 6 transit providers (RFC 7999). AI-driven NEUTRALIZE / OBSERVE / SAFE verdicts, 8-gate safety pipeline with Claude AI Arbiter, progressive ban escalation (7d to 365d), 22-ASN cloud protection, PIN auth. Cloudflare Magic Transit on-demand DDoS protection for prefix-level defense. Alert to blackhole in <3 seconds.
📡 Keep the Lights On
Six daily NOC questions — and the page that answers each one in under 5 seconds.
Traffic Analytics + Flow Analyzer
Live sFlow/IPFIX/NetFlow parsing into ClickHouse (35 tables, 9.5× compression). 1,575 SolarWinds-sourced app signatures via DPI. Top ASNs, IXP community attribution (SwissIX, MIX-IT, MINAP), per-protocol breakdown, Wireshark-style ad-hoc filter.
BMP Loc-RIB (RFC 9069)
Ingest the router's post-policy FIB as a first-class BMP feed. ~218K prefixes live on MX204 — the routes the router actually installs, with the AS-PATH, communities and RPKI status it actually uses.
Capacity Planning & Forecast
P95 billing tracker per-provider, cost-per-Mbps comparison, CDR utilization, 6-month historical trends, what-if simulator. New: least-squares saturation forecast (days-to-80%/95% with confidence badges) and commit-burn projection with month-end overage in CHF, plus a dashboard Capacity Runway KPI.
BGP-LS Topology (RFC 7752)
Link-state NLRI ingestion with 2000-entry ring buffer. Interactive d3-force graph: nodes, links and prefixes straight from the IGP. Junos / Huawei VRP / Cisco IOS-XR terminology cross-reference documented.
Peer Health + Loc-RIB Monitors
BMP session uptime badges, flap detection with history, down-since timestamps, per-peer prefix counts. Auto-emailed outreach on 3-day-down via Peering Manager — GOLINE-branded templates.
External BGP Visibility
RIPE RIS Live WebSocket across 23 global vantage points. Mismatch + hijack detection, propagation trace, Last-Seen timestamp, monitored prefix watchlist with alerts on visibility changes or withdrawals.


🛡️ Hunt, Correlate, Mitigate
Six daily SOC questions — and the answer in ML, correlation and one-click mitigation.
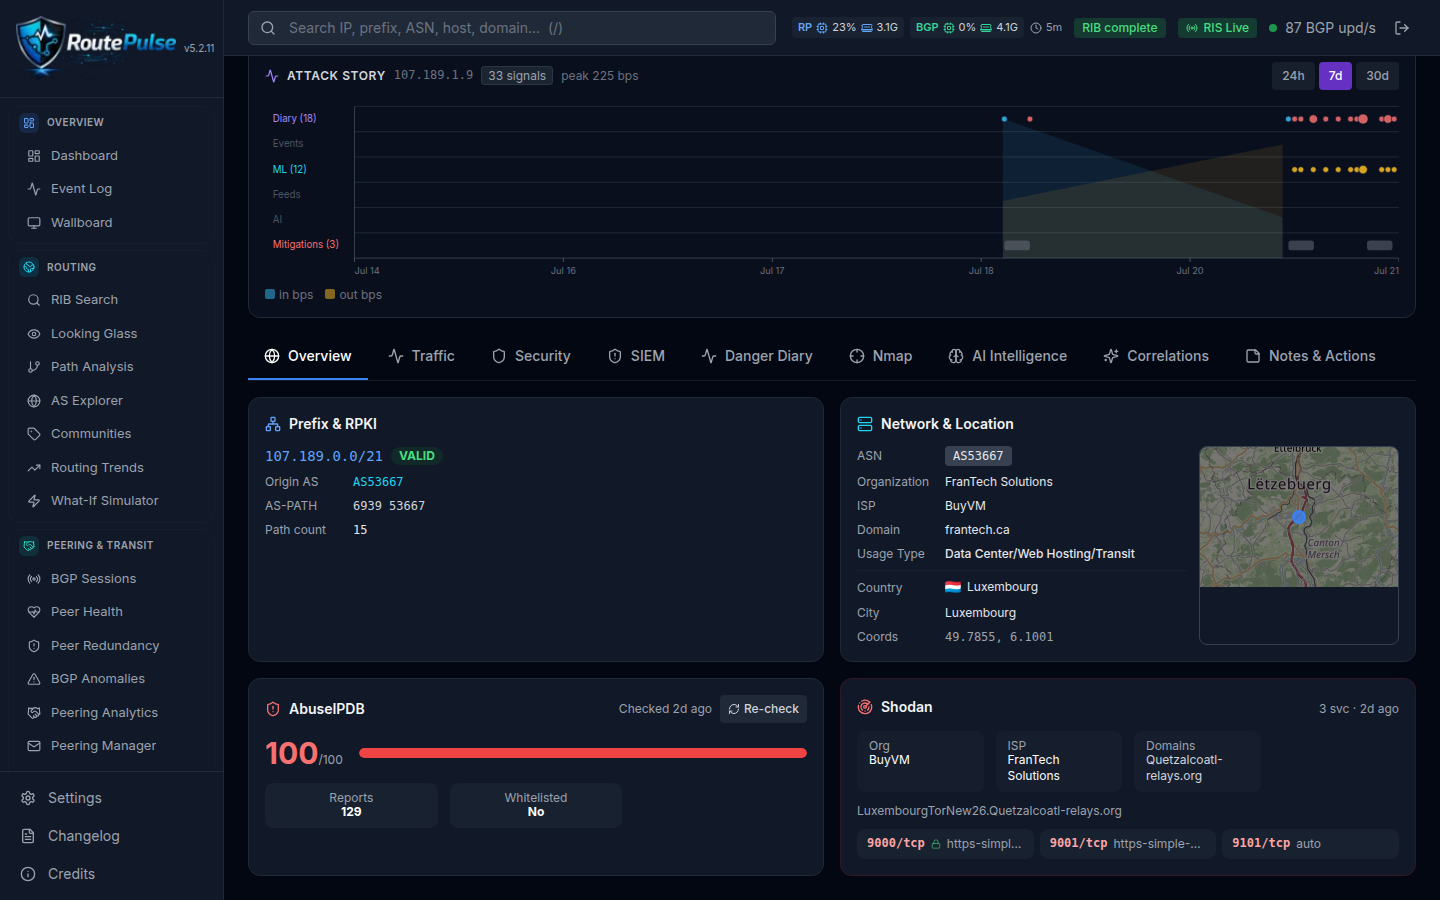
Unified Cybersecurity Dashboard
5-pillar host scoring (Cyber + Behavioral + ML + External + FeedIntel, 0–100), 18 ML models, 42 configurable flow rules, 39 threat feeds (52K+ IoCs). Cross-source from Wazuh SIEM + Suricata IDS + FortiGate + AbuseIPDB + Shodan + Nmap parallel. Now with an interactive 24h attack heatmap (per-hour drill-down) and a live threat ticker streaming the latest events.
Conviction Engine (SPRT + Thompson + Causal)
Five pillars must agree: Sequential Probability Ratio Test to 99% confidence, Thompson Sampling exploration, Causal Verification, 22 CDN/cloud ASN whitelists + 4-layer SSH protection veto, Claude AI arbiter final review. 84% fewer false-positive blackholes.
Security Events Cross-Source
Every cyber event rendered with full context: target IP + hostname + destination port/proto + application + FortiGate action (color-coded block/allow) + FortiGuard CR score + policy ID + Wazuh rule level + agent name + aggregation counters (deny/unique targets/window).
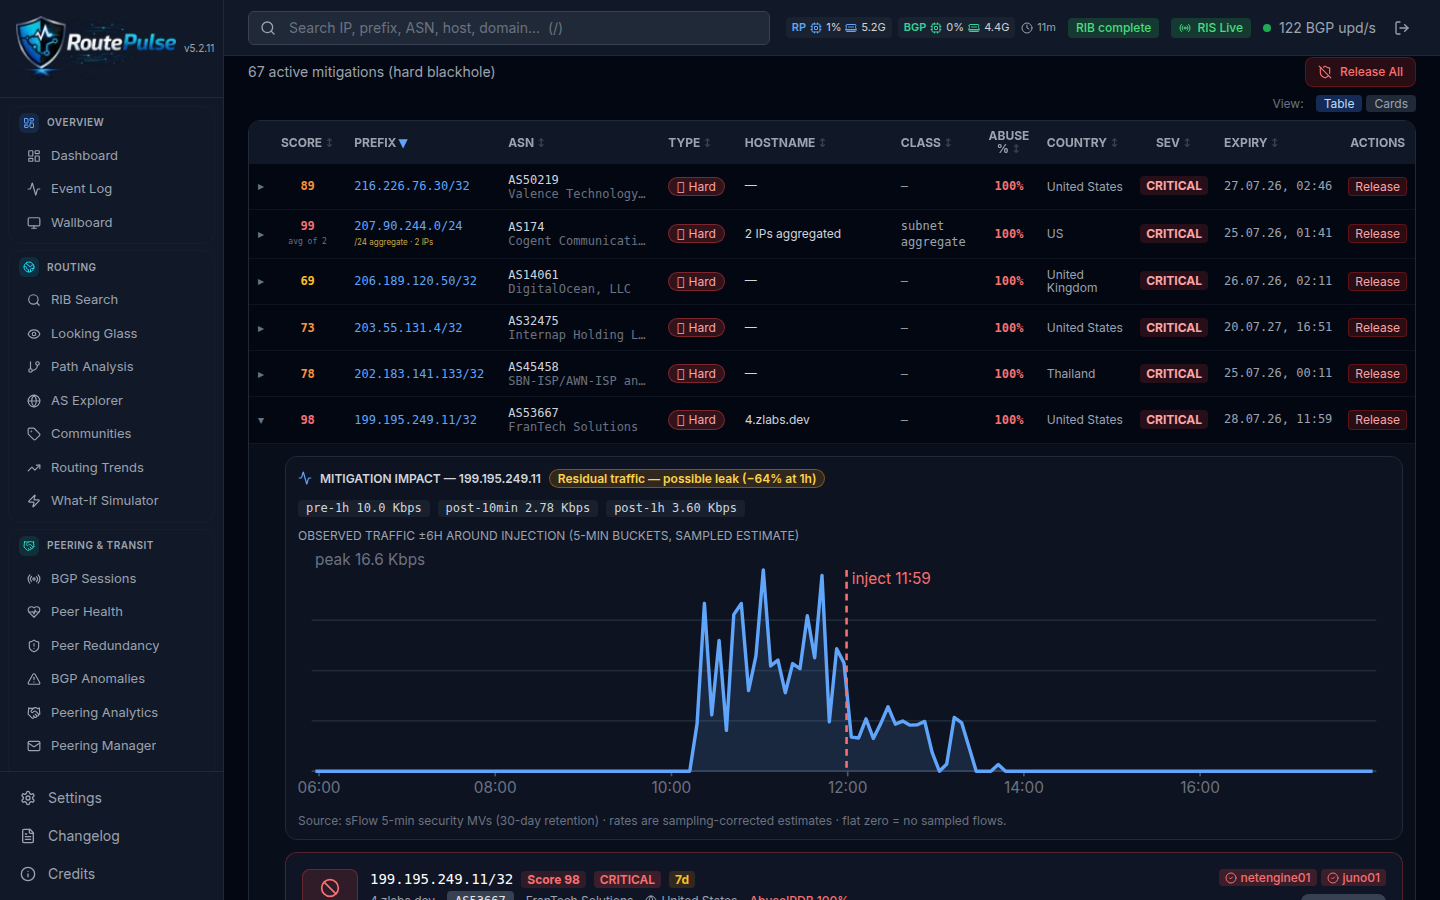
Orchestrated Mitigation: RTBH / FlowSpec / CF MT
Three tools, one engine. RTBH (SSH Juniper + Huawei, BGP 65535:666) for /32-/24 blackholes. BGP FlowSpec (RFC 8955/8956) for surgical rate-limit/redirect/drop. Cloudflare Magic Transit on-demand for volumetric scrubbing. Median 17 seconds from detect to router commit.
ML + NIST/MITRE Tier-1 Detectors
18 unsupervised ML models: 17-feature IsolationForest, K-Means auto-k, Holt-Winters, Markov path-norm, temporal embeddings, beaconing detector. Plus 5 NIST/MITRE Tier-1: QUIC C2, Protocol Mismatch (T1572 tunnels), DGA/Fast-Flux, Encrypted C2 (JA3), BGP-Traffic correlation.
ANIE — 6-Layer Autonomous AI
Claude-powered autonomous intelligence engine. Every AI decision logged with reason, playbook, confidence score. 90-day audit trail for NIS2/DORA. Pre-anonymised prompts, EU endpoint, no training retention. Local-model fallback available for full data isolation.




Command Center & Public Transparency
🖥️ Operations Dashboard
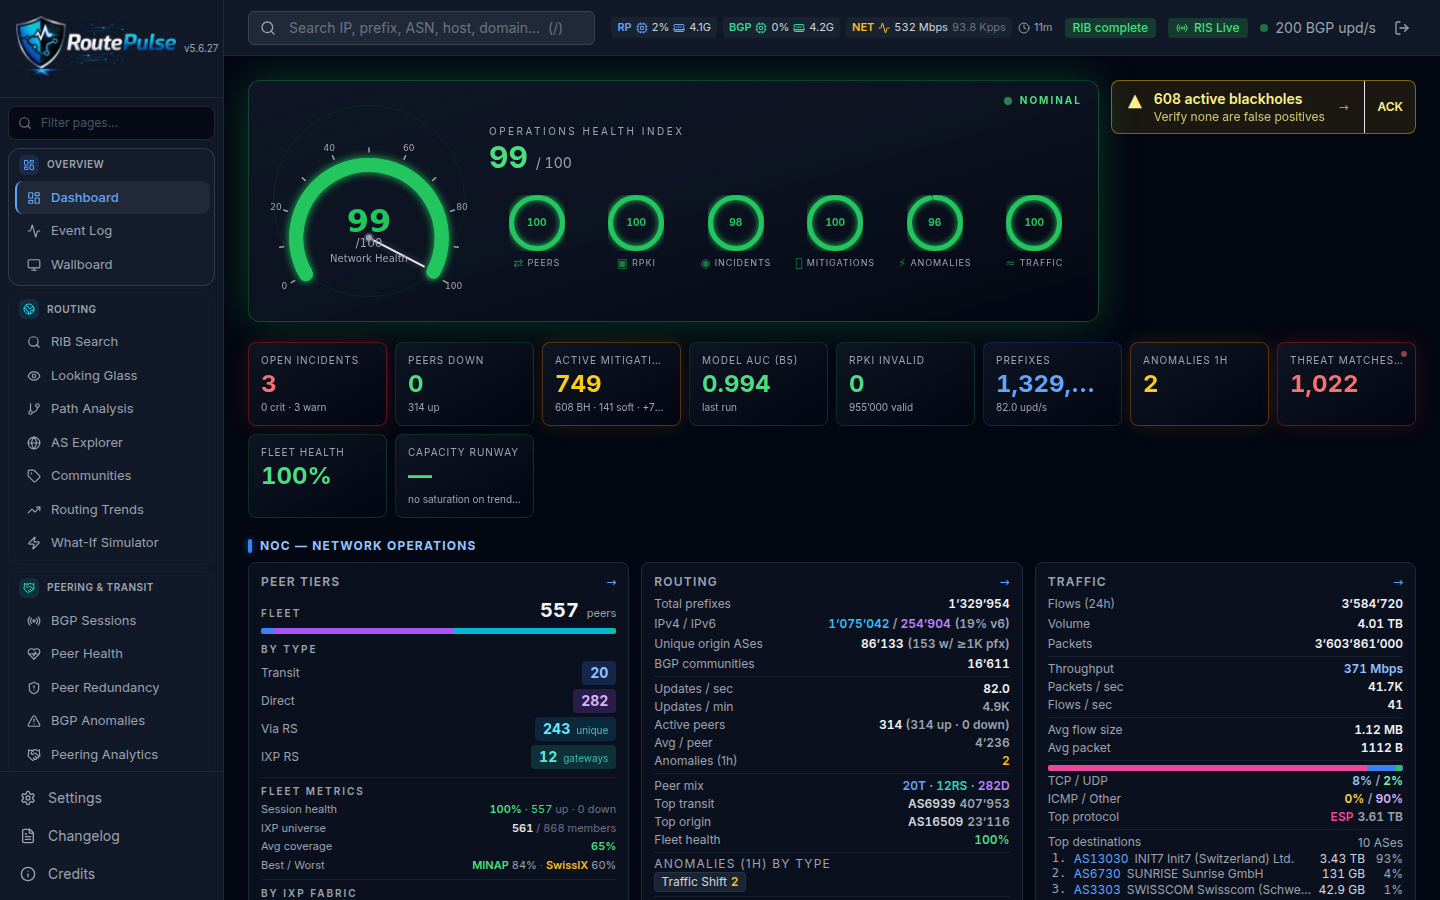
One operations health index over fleet, RPKI, mitigations, anomalies and traffic, with open incidents and active blackholes beside the routing picture.
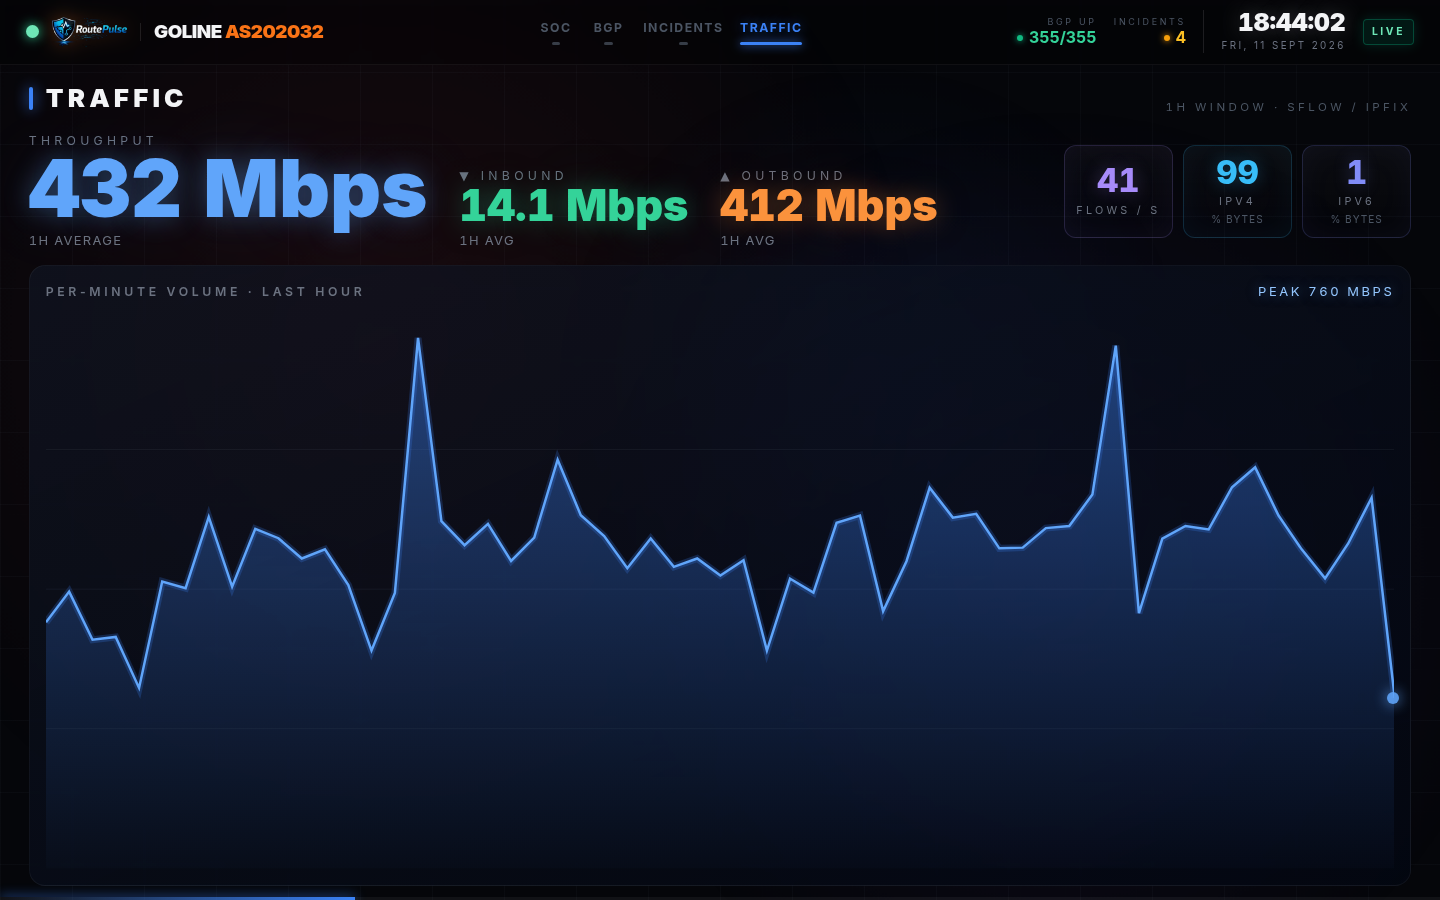
📺 NOC / SOC Wallboard →
A wall display built for the room: incidents, mitigations, peers, traffic and the campaigns being blocked right now.
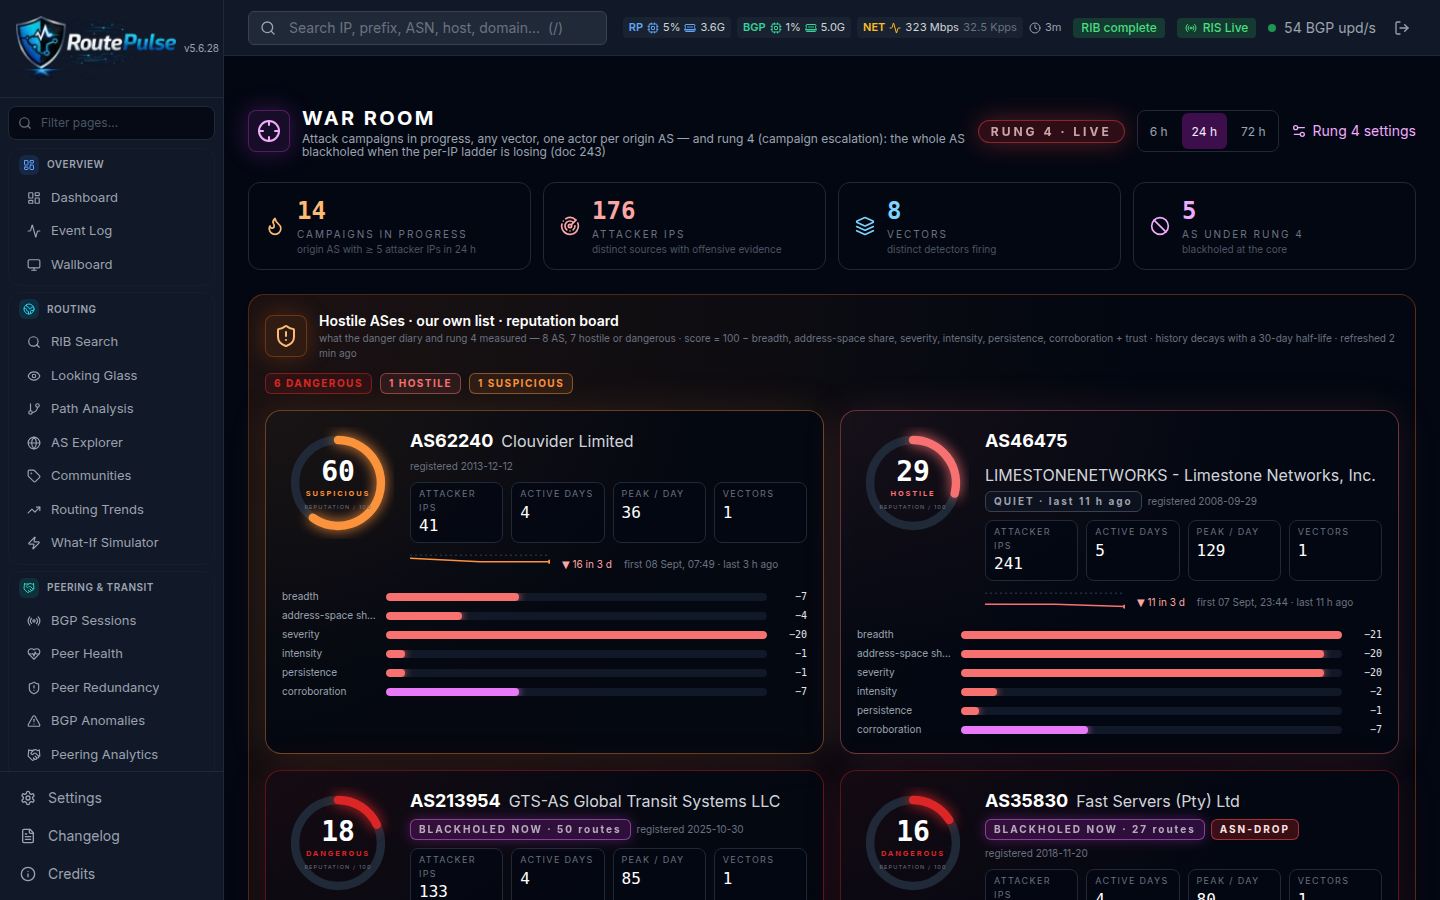
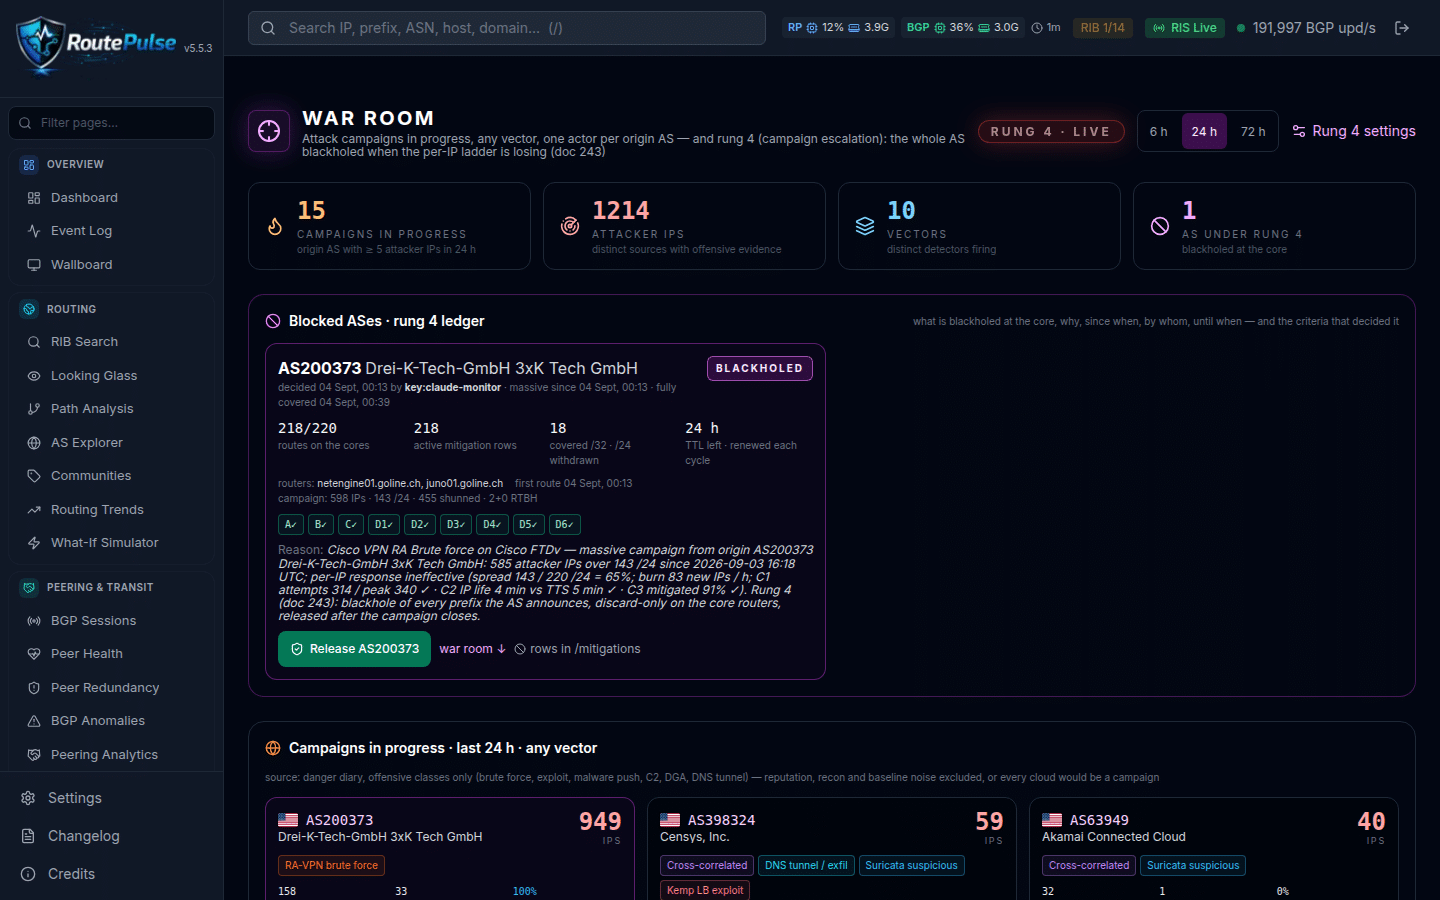
🎯 War Room →
Every attack campaign by origin AS across every vector, AS reputation 0–100, and rung 4: the whole AS blackholed when the per-IP ladder is losing.
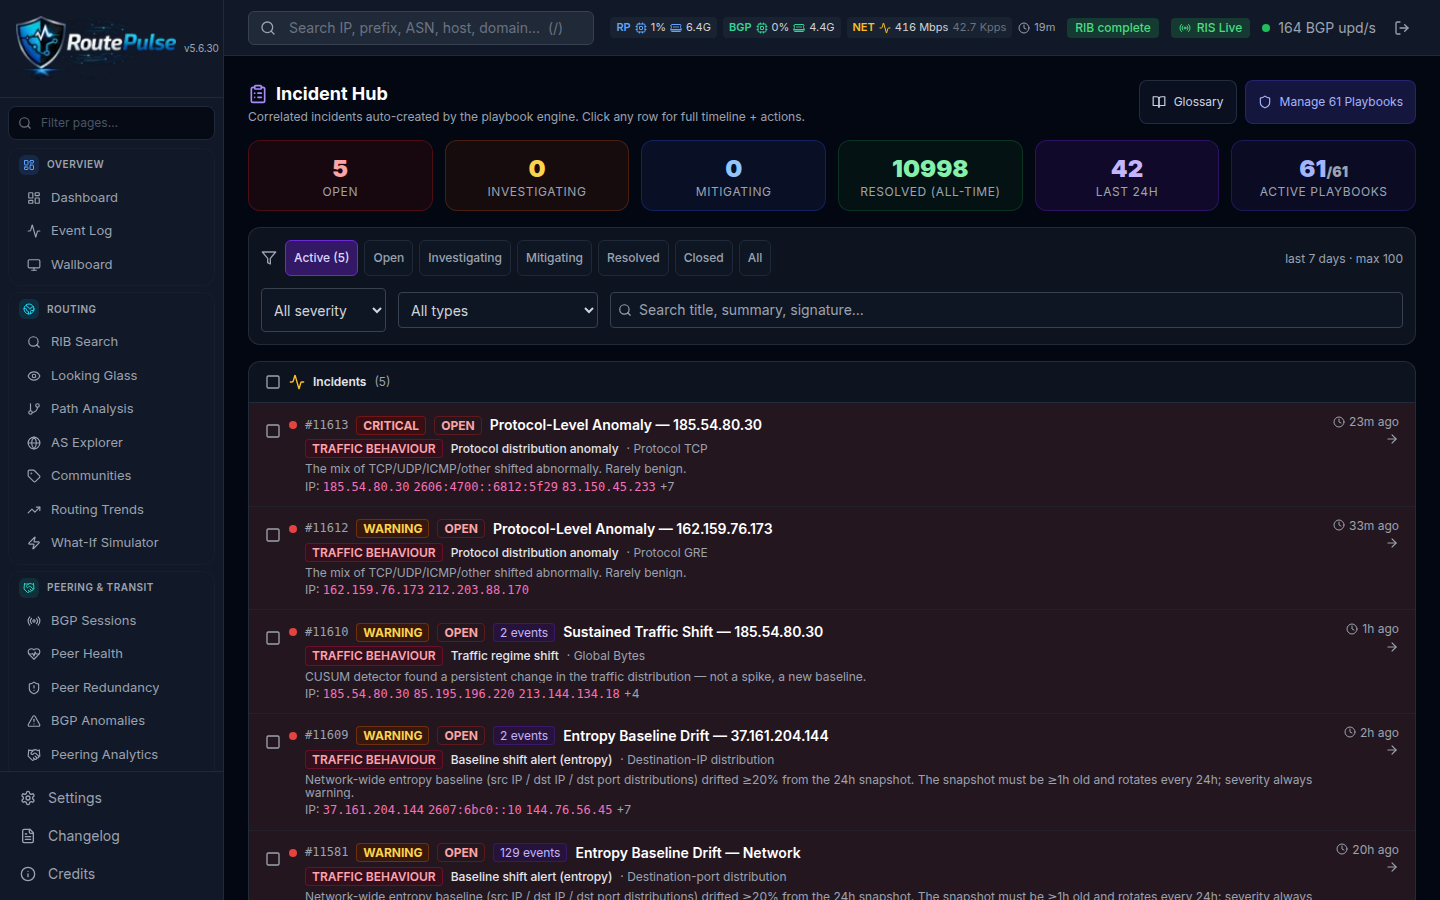
🚨 Incidents & Playbooks →
Anomalies become incidents with a MITRE-tagged playbook attached — 61 playbooks decide what is investigated, mitigated or only recorded.
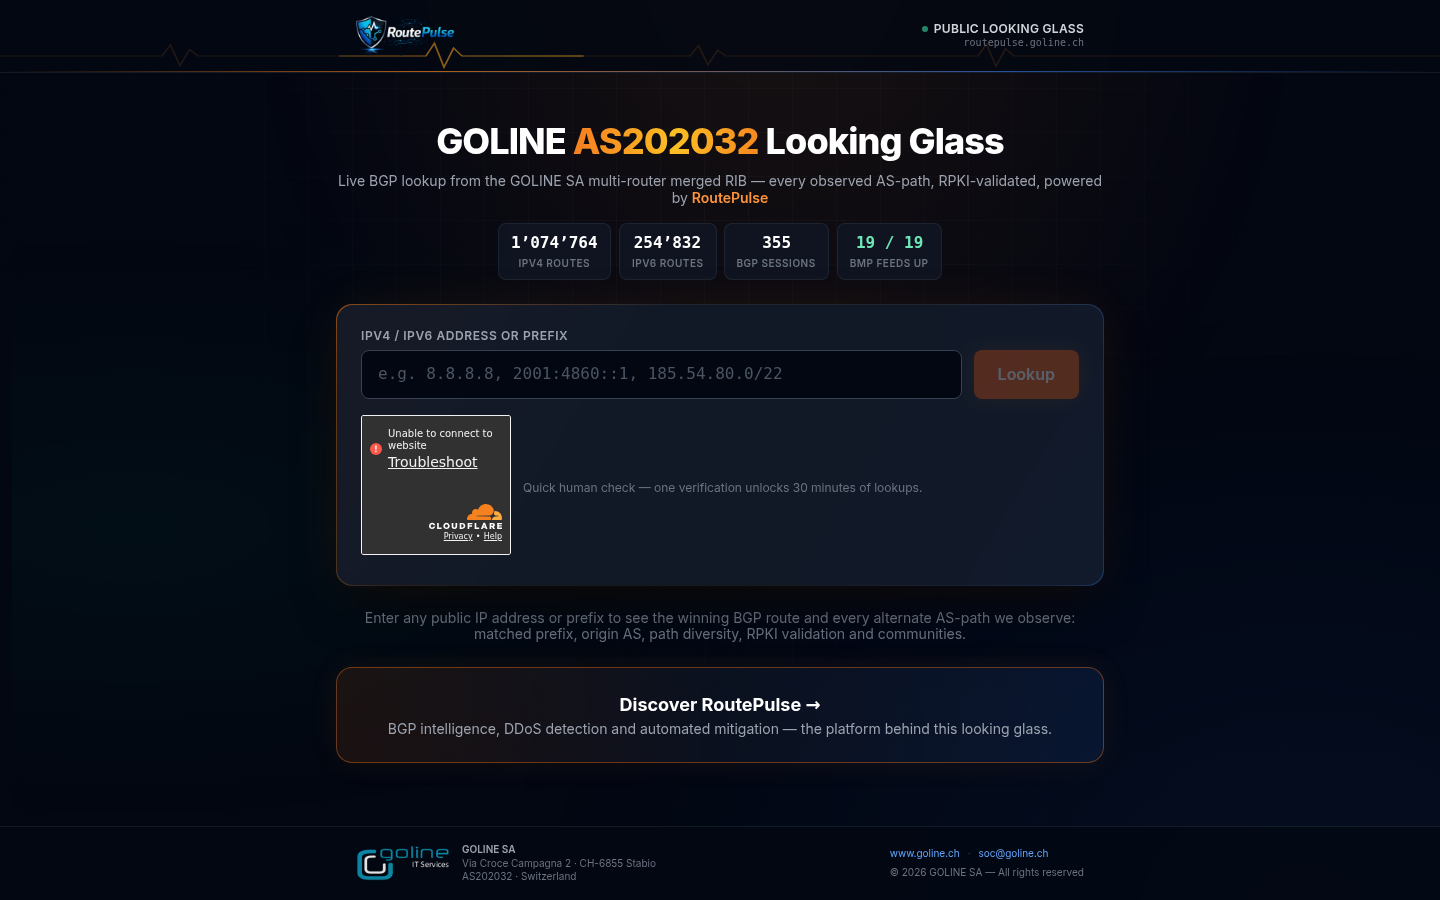
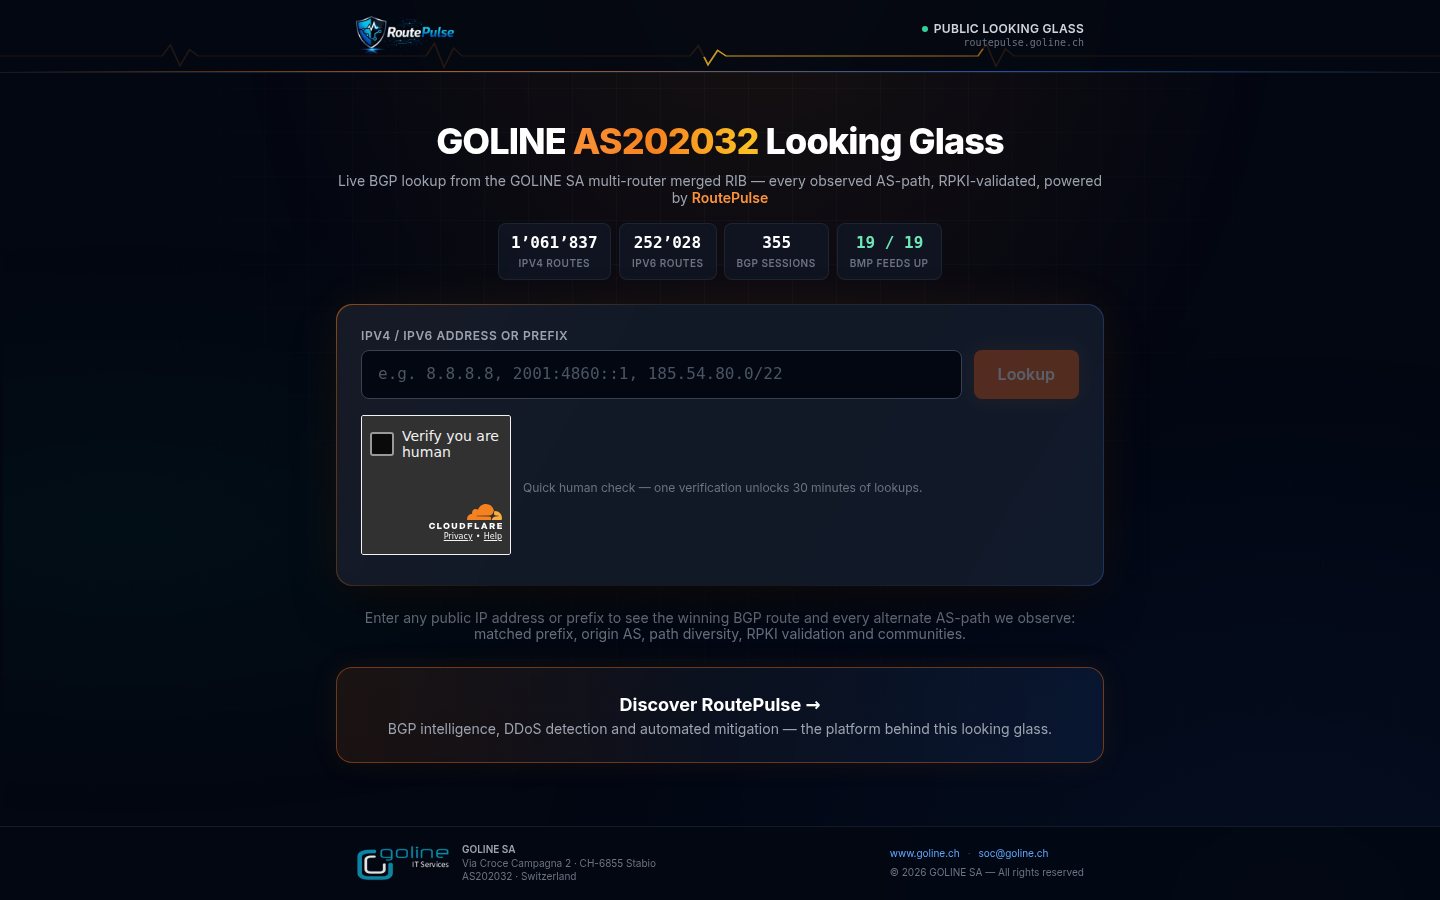
🔭 Public Looking Glass
A public looking glass on your live routing table: best path, RPKI status, AS-PATH and communities for any prefix, Turnstile-protected.
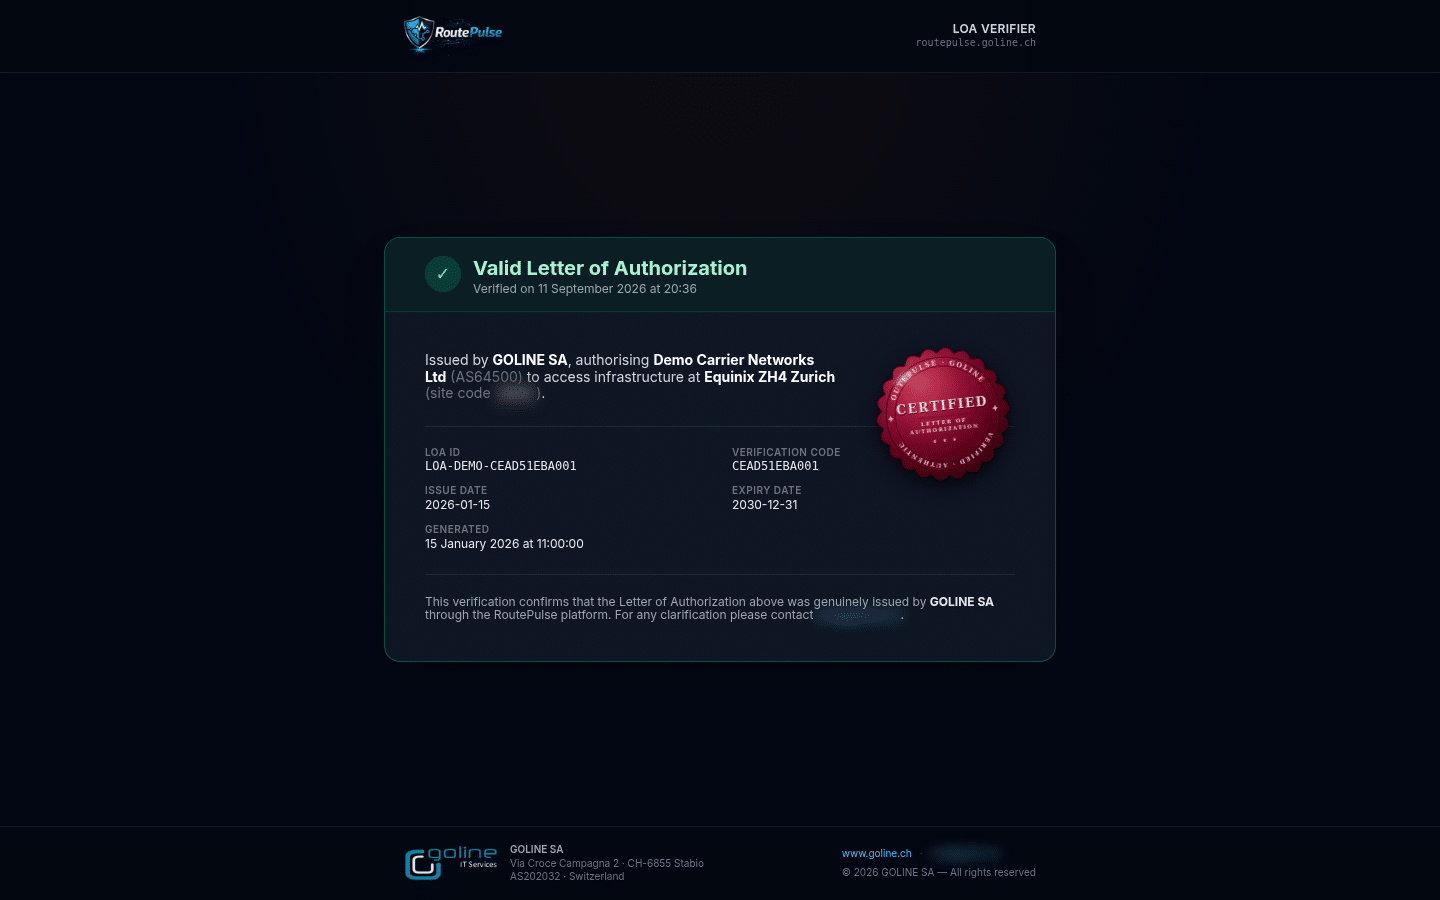
📜 LoA Verifier →
Letters of authorisation signed with Ed25519 and verifiable by anyone at a public URL — the paperwork of peering, made tamper-evident.
🟢 Live public status page & status badge
A public status page with BGP health, peers, prefixes and 24-hour cyber activity — aggregates only, refreshed every 60 seconds — and a live SVG badge you can embed anywhere.

Embed the badge: <img src="https://routepulse.goline.ch/api/v1/badge.svg">
BGP Intelligence
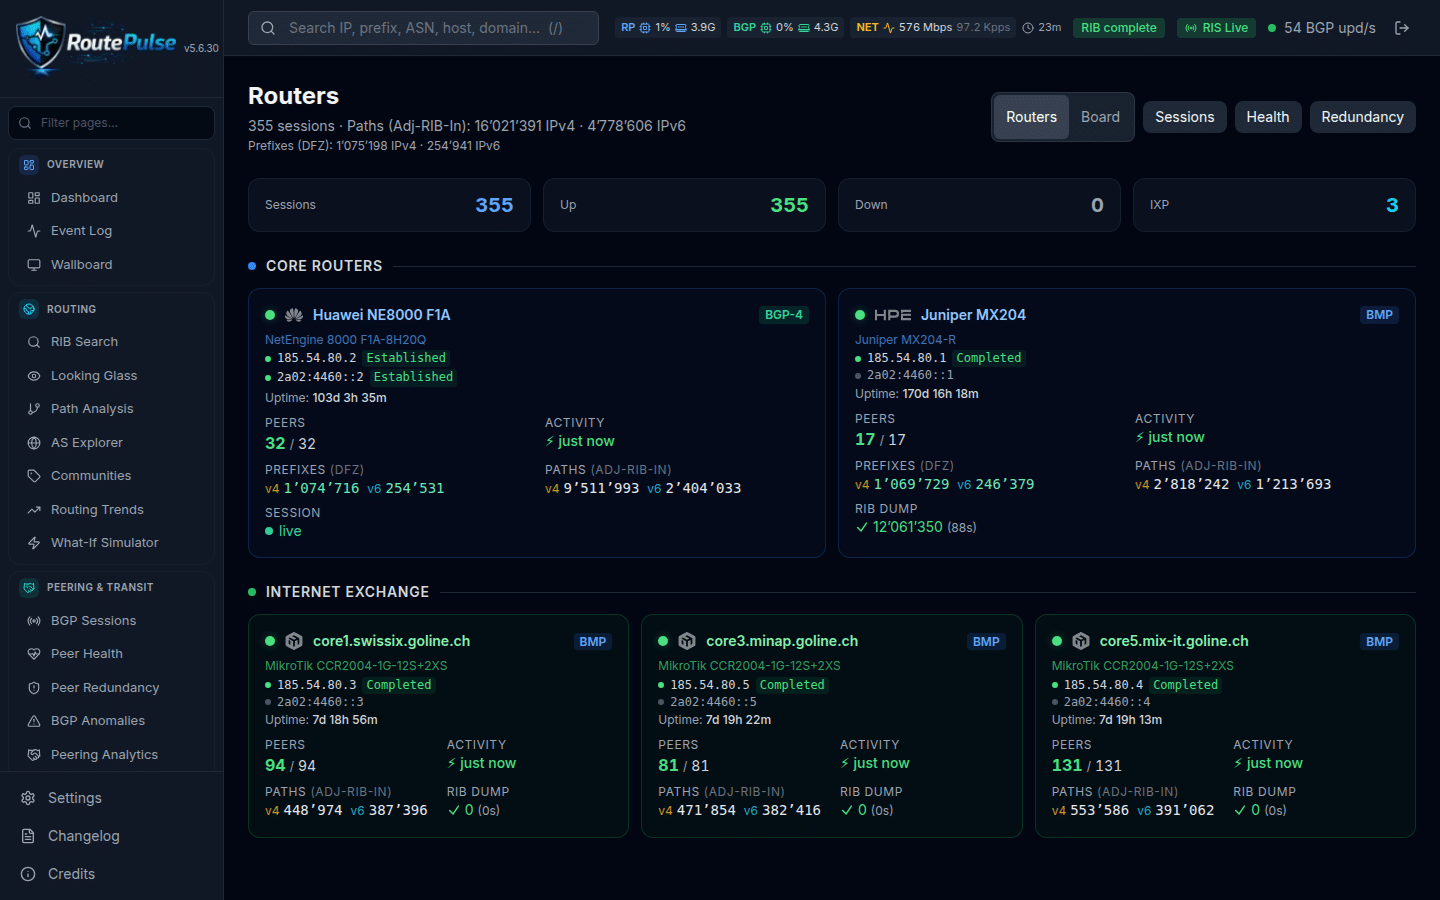
🛰️ BMP / BGP-4 Collectors
Multi-router BMP with Juniper MX and Huawei NetEngine, a native BGP-4 receiver, Loc-RIB monitoring (RFC 9069) and BGP-LS topology (RFC 7752).
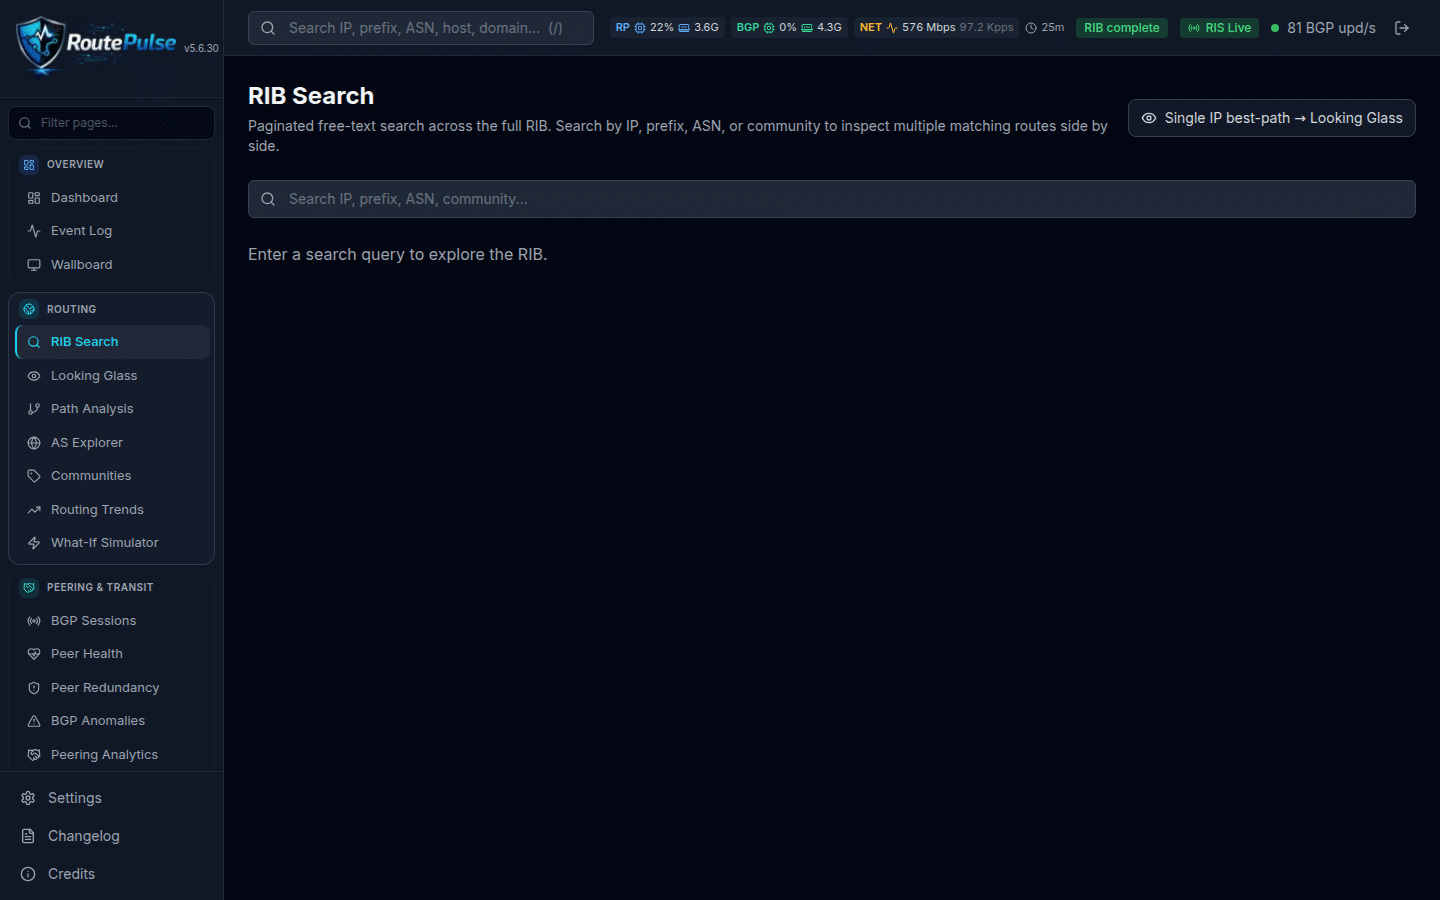
🔎 RIB Search & Looking Glass
Faceted search across the whole table by prefix, origin, AS-PATH or community; single-IP lookup with RPKI status and a BGPlay-style path timeline.
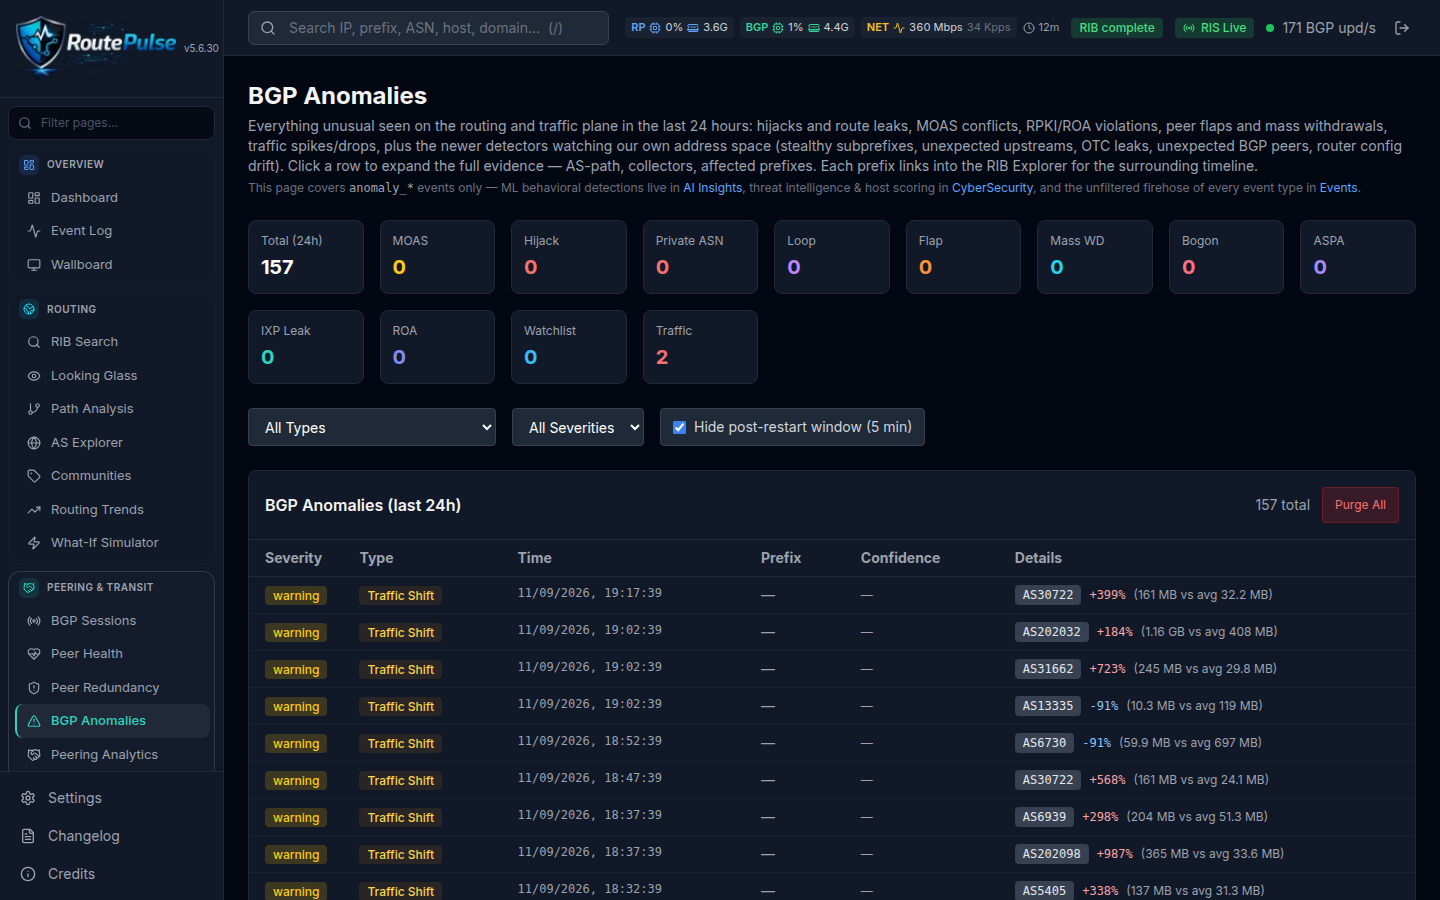
⚠️ BGP Anomaly Detection →
Nineteen routing anomaly classes — MOAS, sub-prefix hijack, route leak, AS-PATH loop, bogon, ASPA invalid — detected on your live table and corroborated with RIPE RIS.
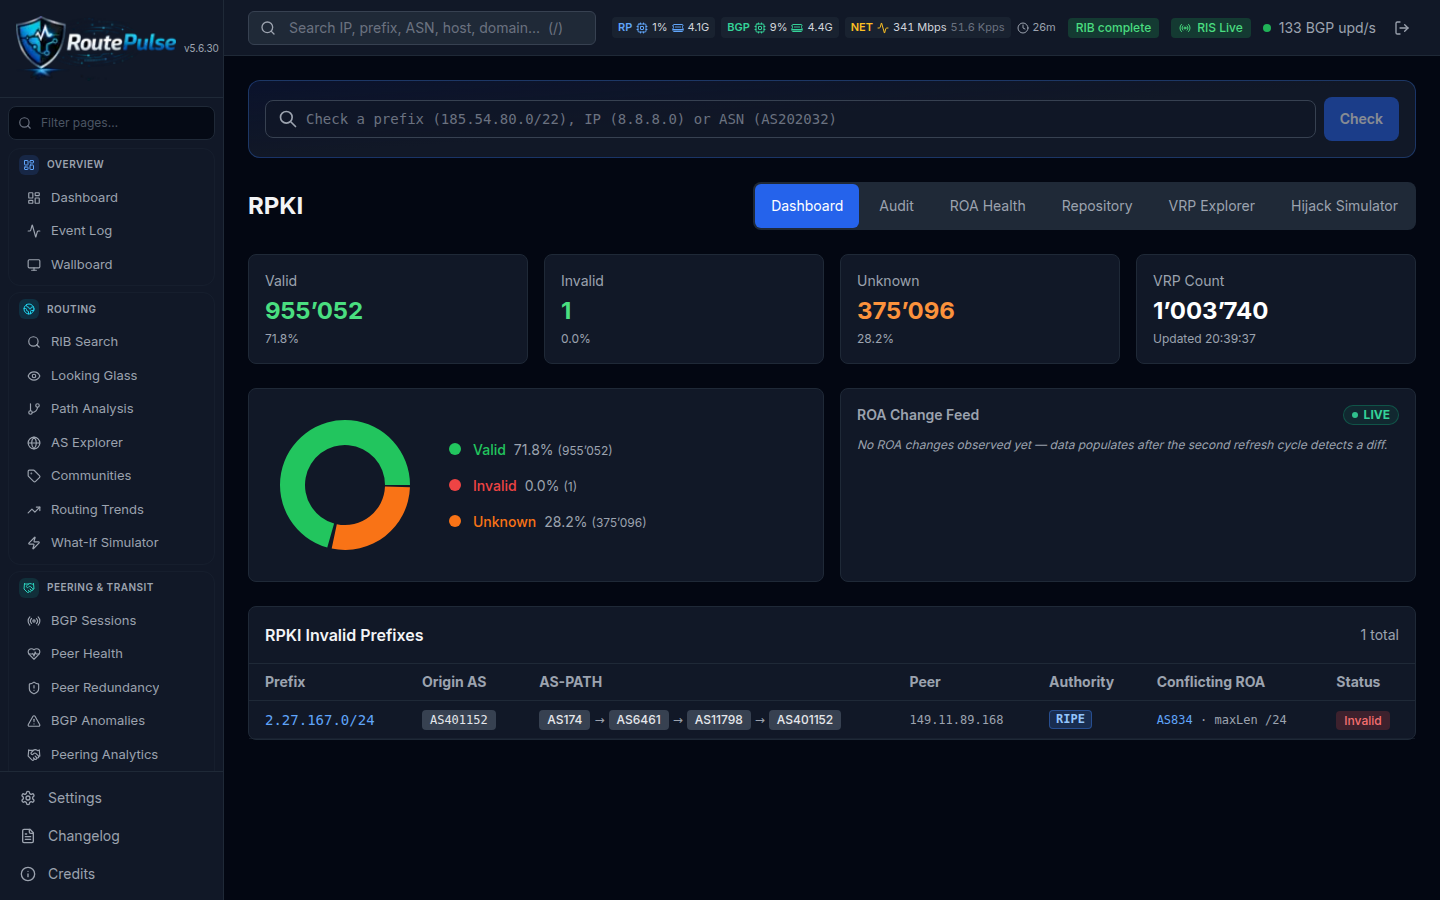
🛡️ RPKI + ASPA →
RPKI validation on every path and ASPA (RFC 9234) route-leak detection, with invalid routes listed and explained, ROA lifecycle monitoring and an audit view.
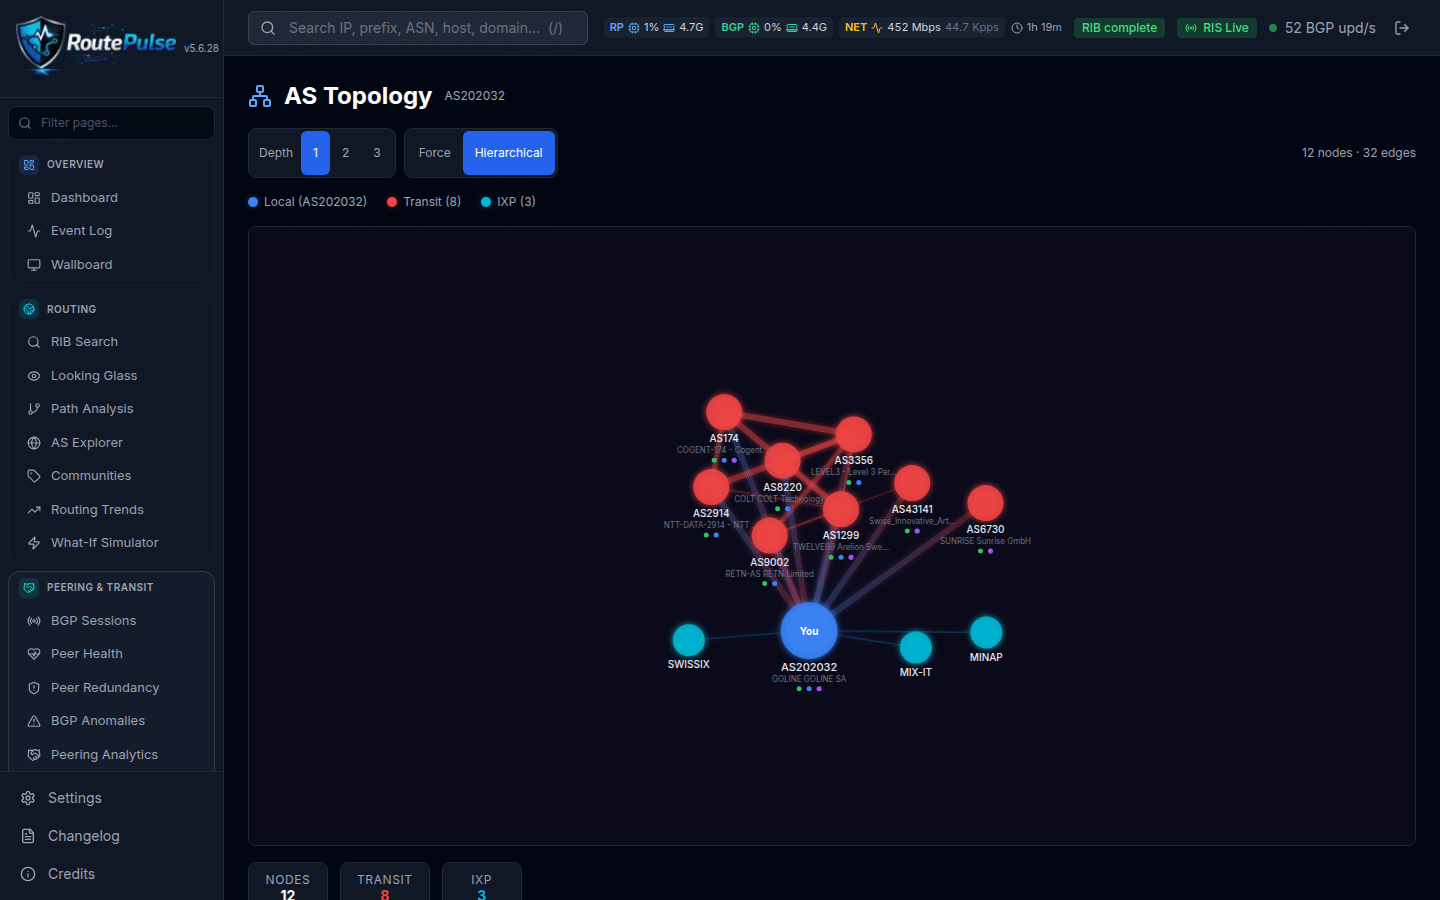
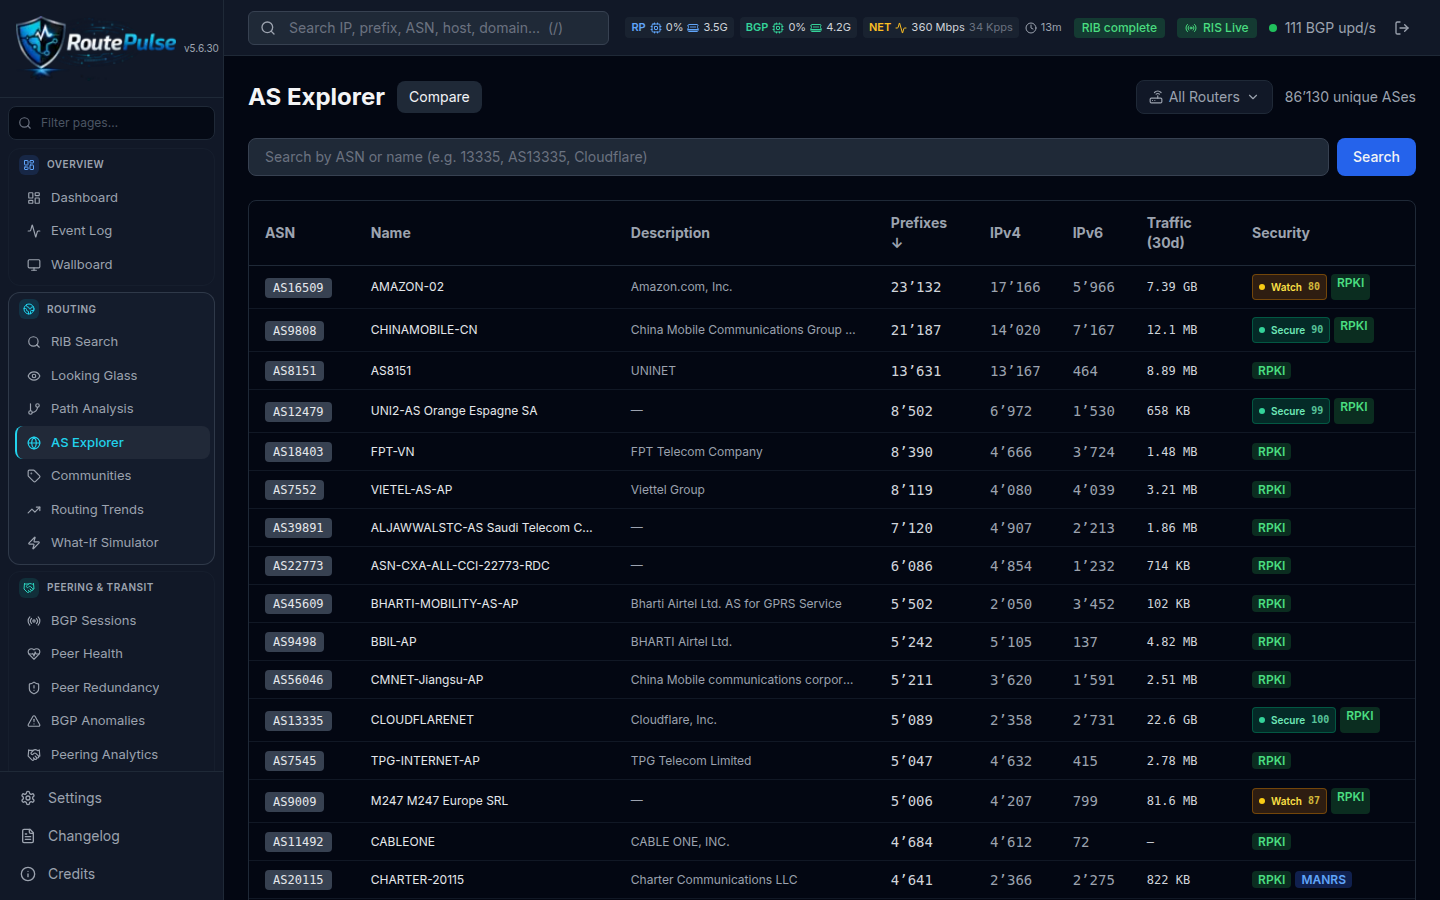
🌐 AS Explorer & Topology →
Every autonomous system with its prefixes, relationships, traffic, security badges and reputation, one click from any alert; animated topology and path analysis.
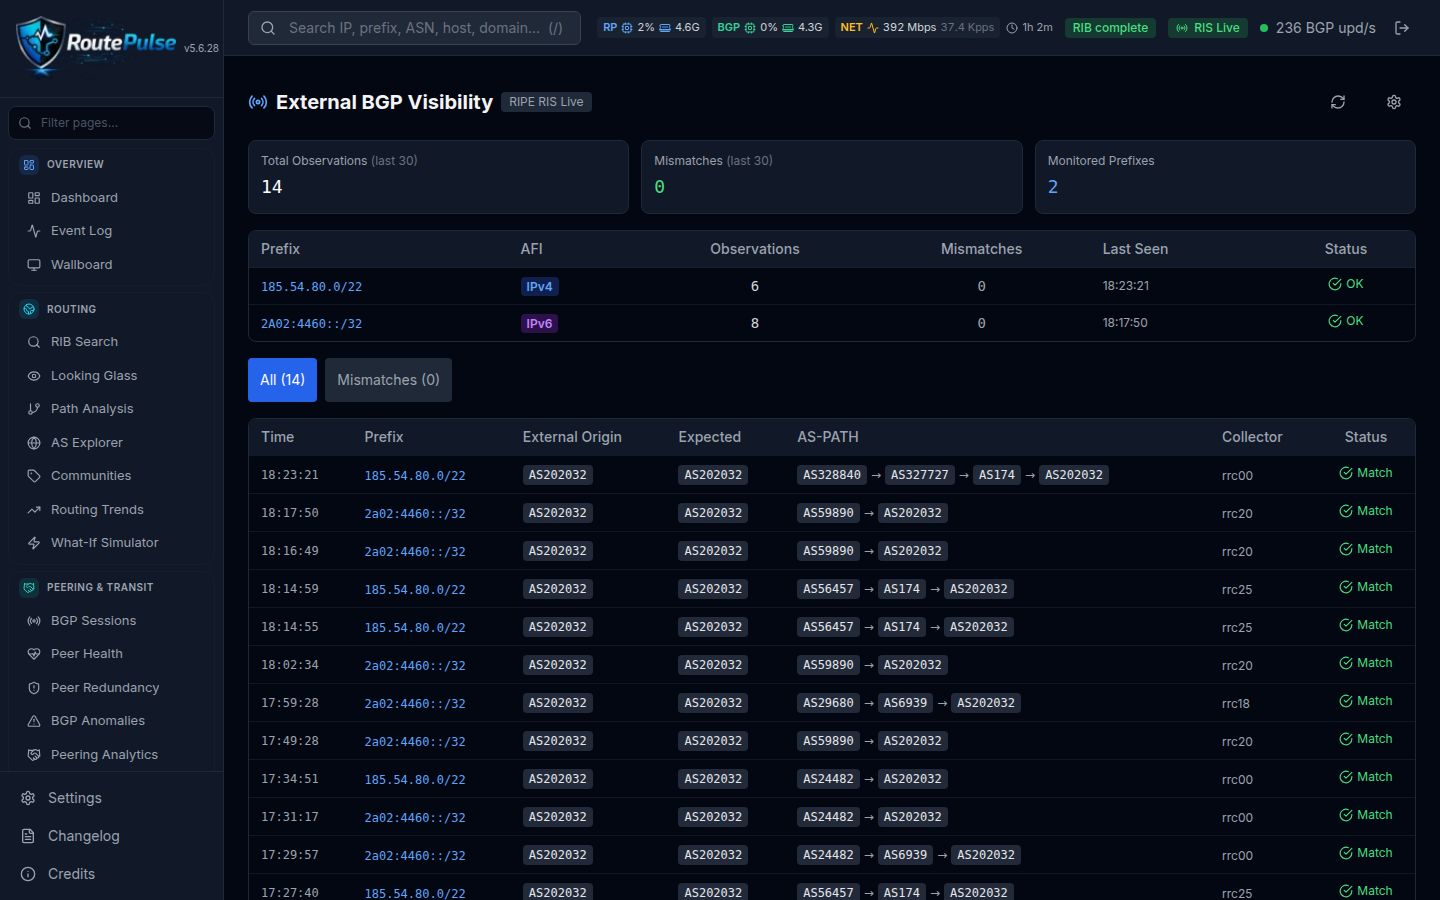
👁️ External Visibility & Prefix Monitoring →
How the Internet sees your prefixes, live from RIPE RIS, with alerts when a prefix disappears, moves or is announced by someone else.
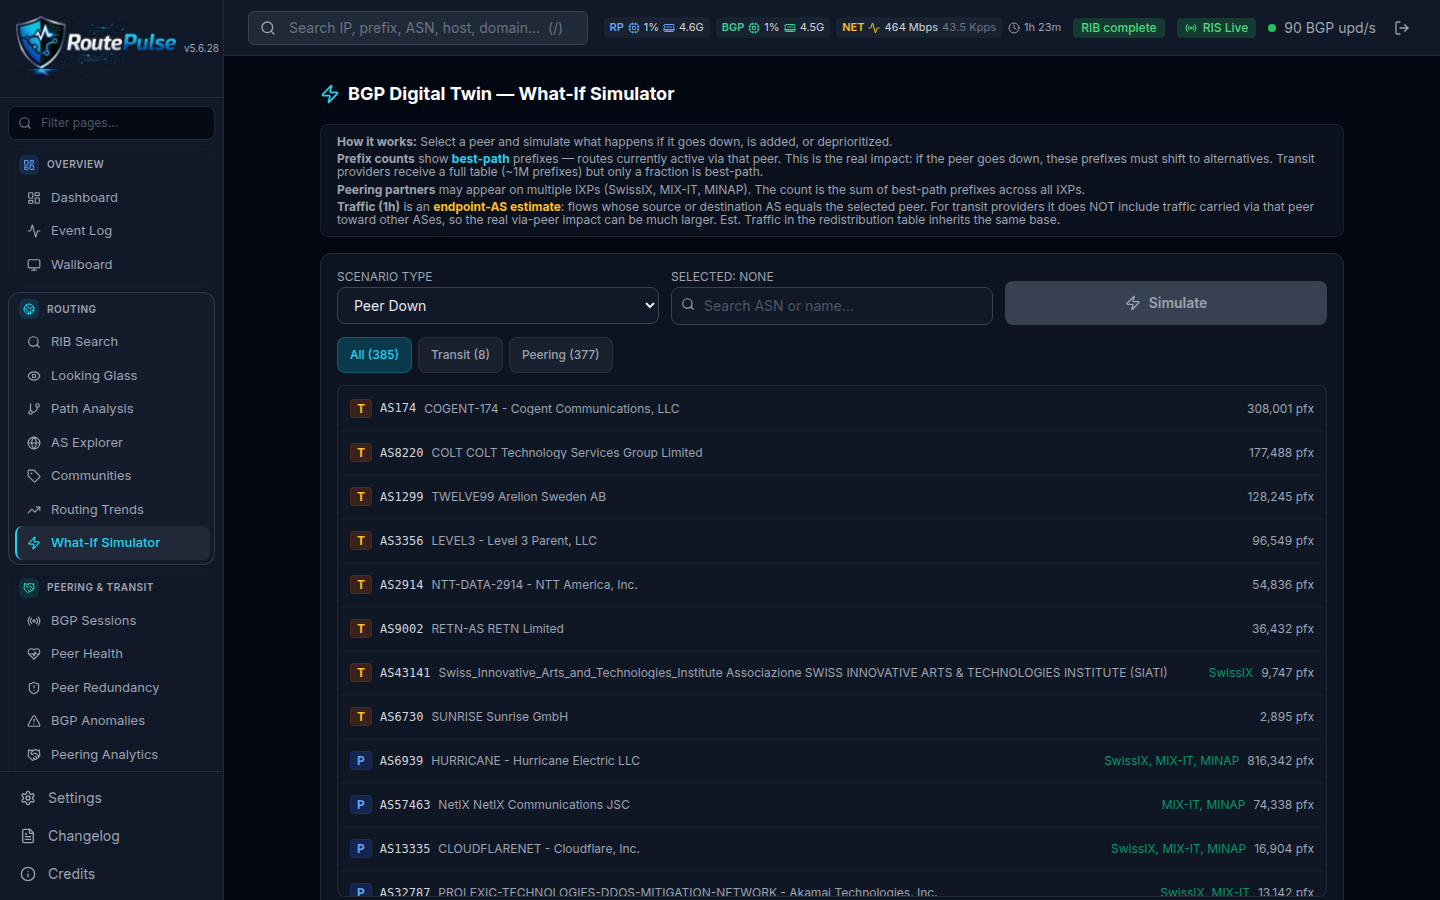
🧪 BGP Digital Twin (What-If)
Simulate a transit outage, a new peer or a hijack on your real RIB and see where traffic would go before it happens.
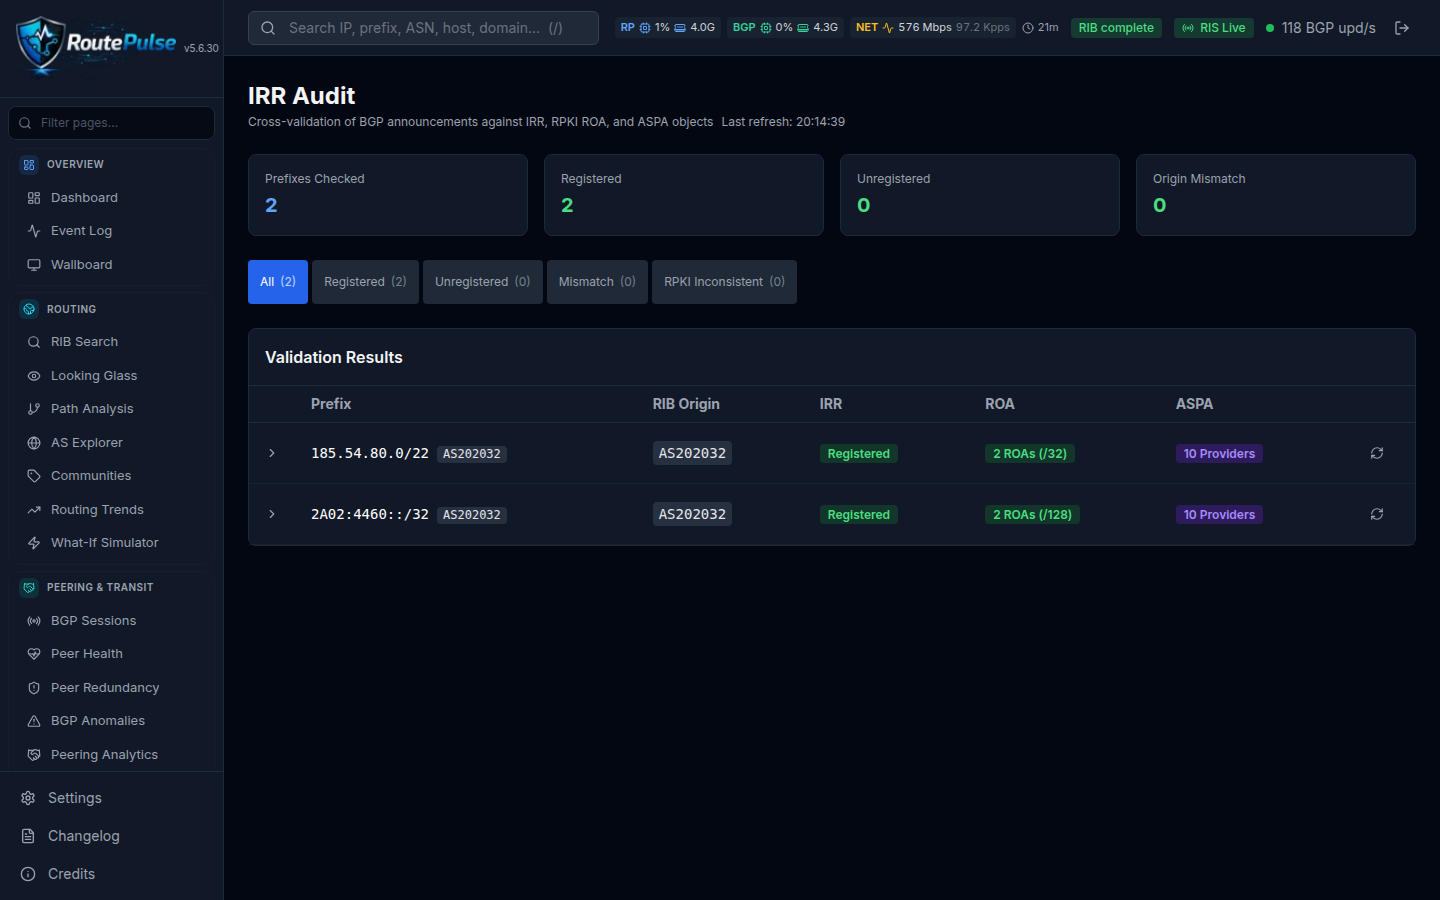
🗂️ IRR Audit & RIPE DB Editor →
Route objects cross-checked against what is actually announced, and the RIR estate edited from the NOC with a three-gate safety net.
Flow Analytics & Traffic
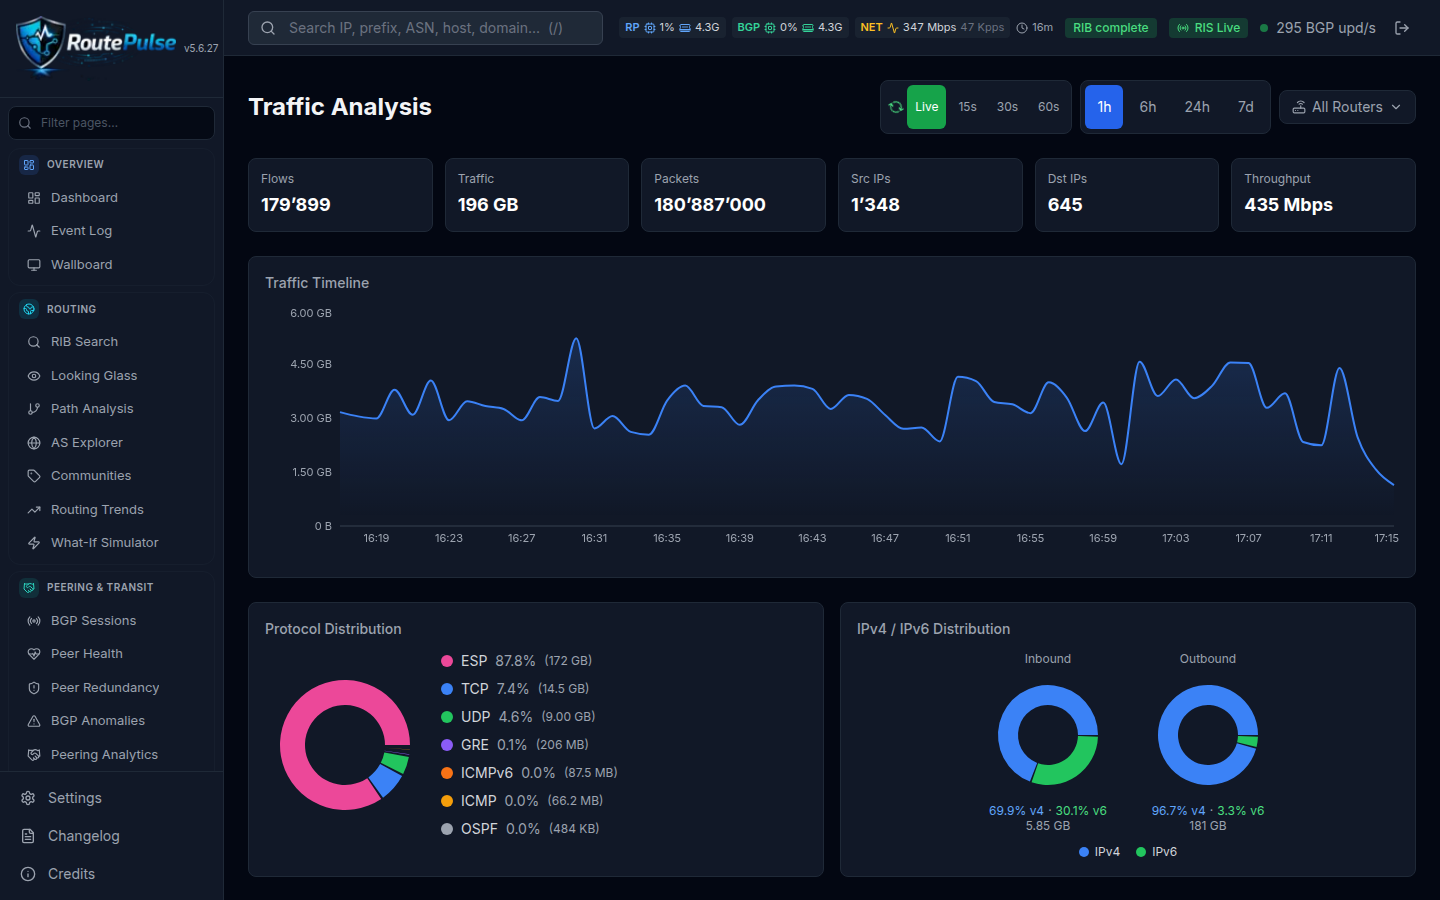
📊 Traffic Analytics →
Per-interface, per-peer and per-AS breakdowns, protocol mix, IPv4/IPv6 split and DPI application classification on flows you can reconcile with SNMP.
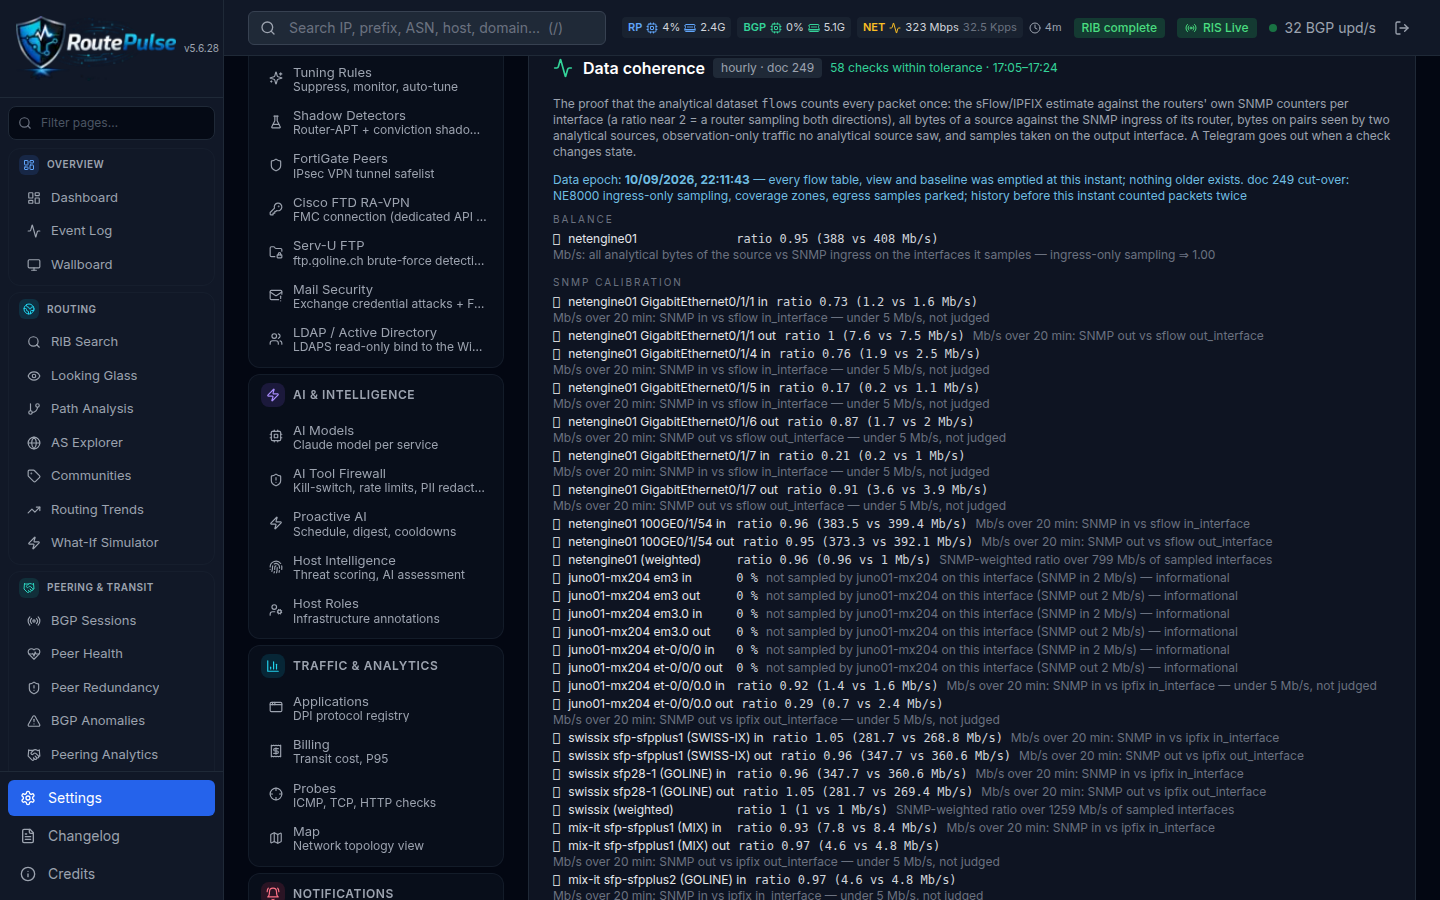
📐 Data Coherence — proven hourly
An hourly job compares every flow source with the routers’ own SNMP counters, overlap between sources, traffic no source sees and egress double-counting. Two datasets: analytical (every packet once) and observation-only.
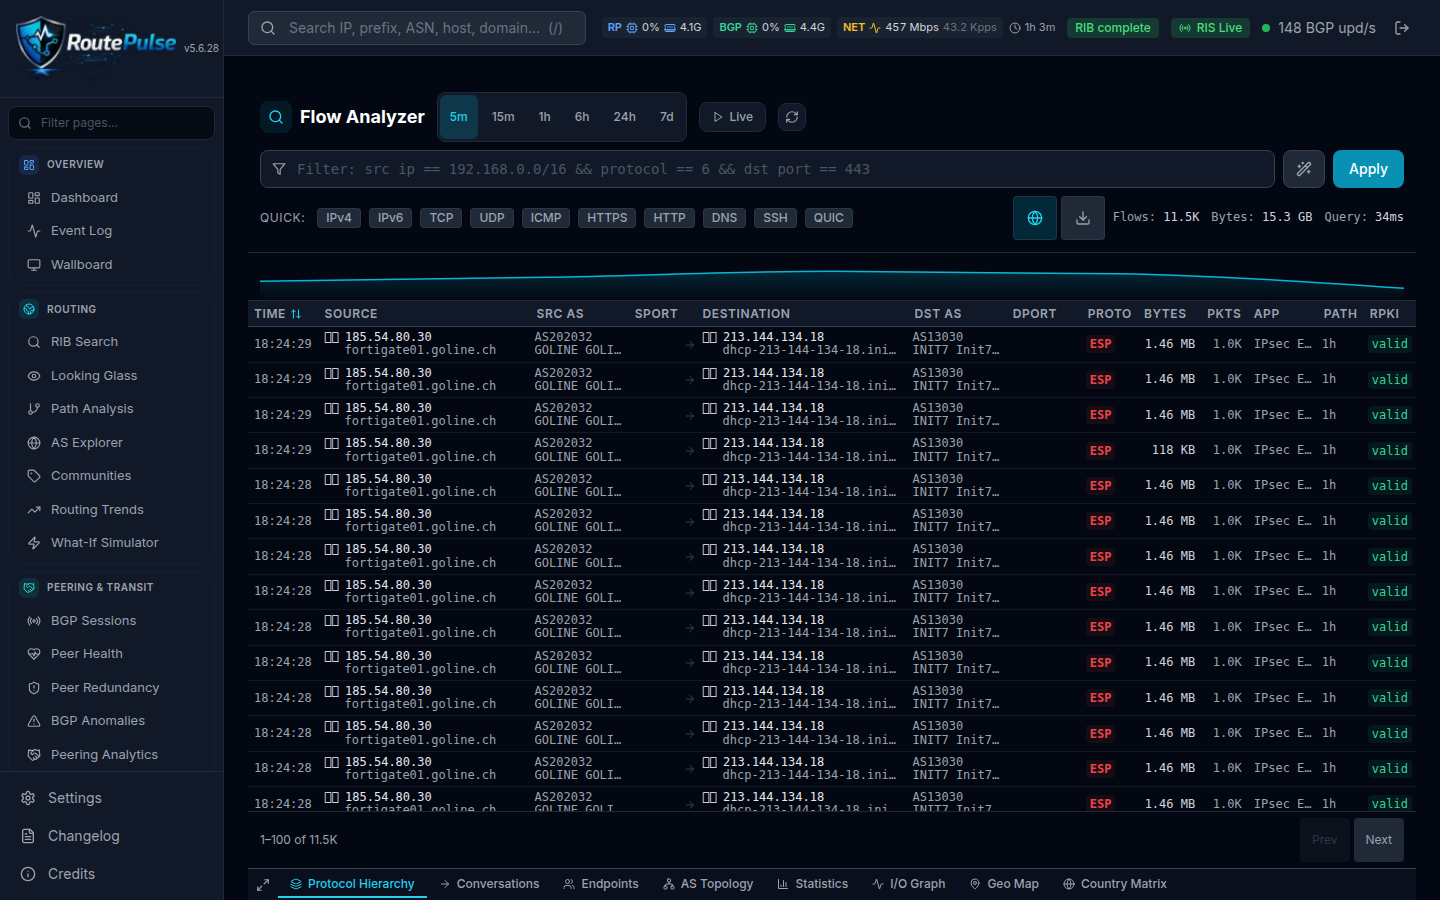
🧬 Flow Analyzer →
Ask the flow table anything: live mode, filters on every field, drill-down from a peak to the hosts that caused it.
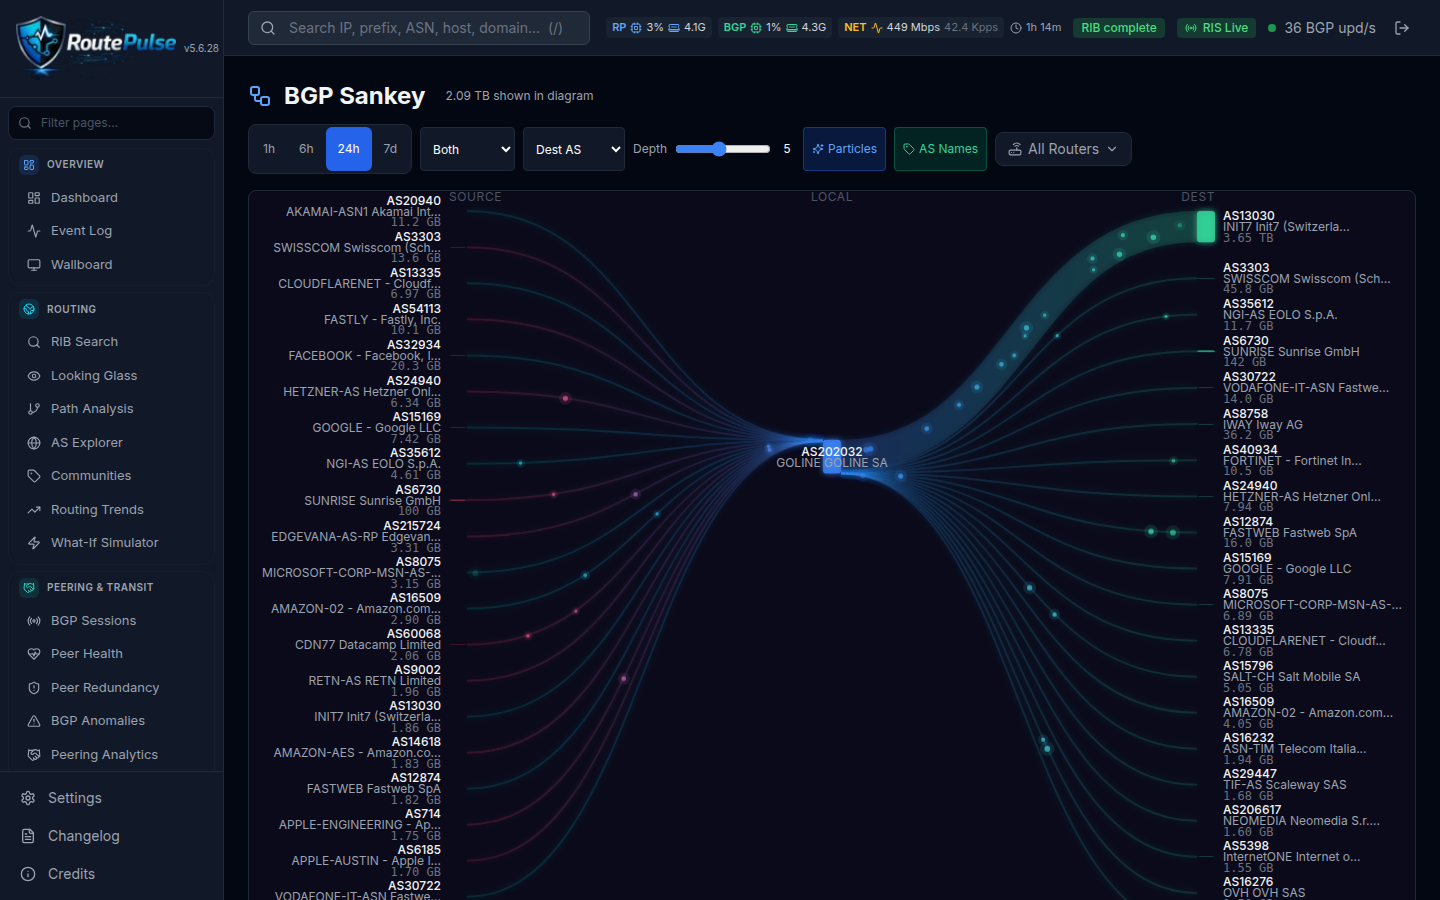
🌊 Traffic Sankey →
Where your traffic really goes, source to destination, as a living flow diagram with particles.
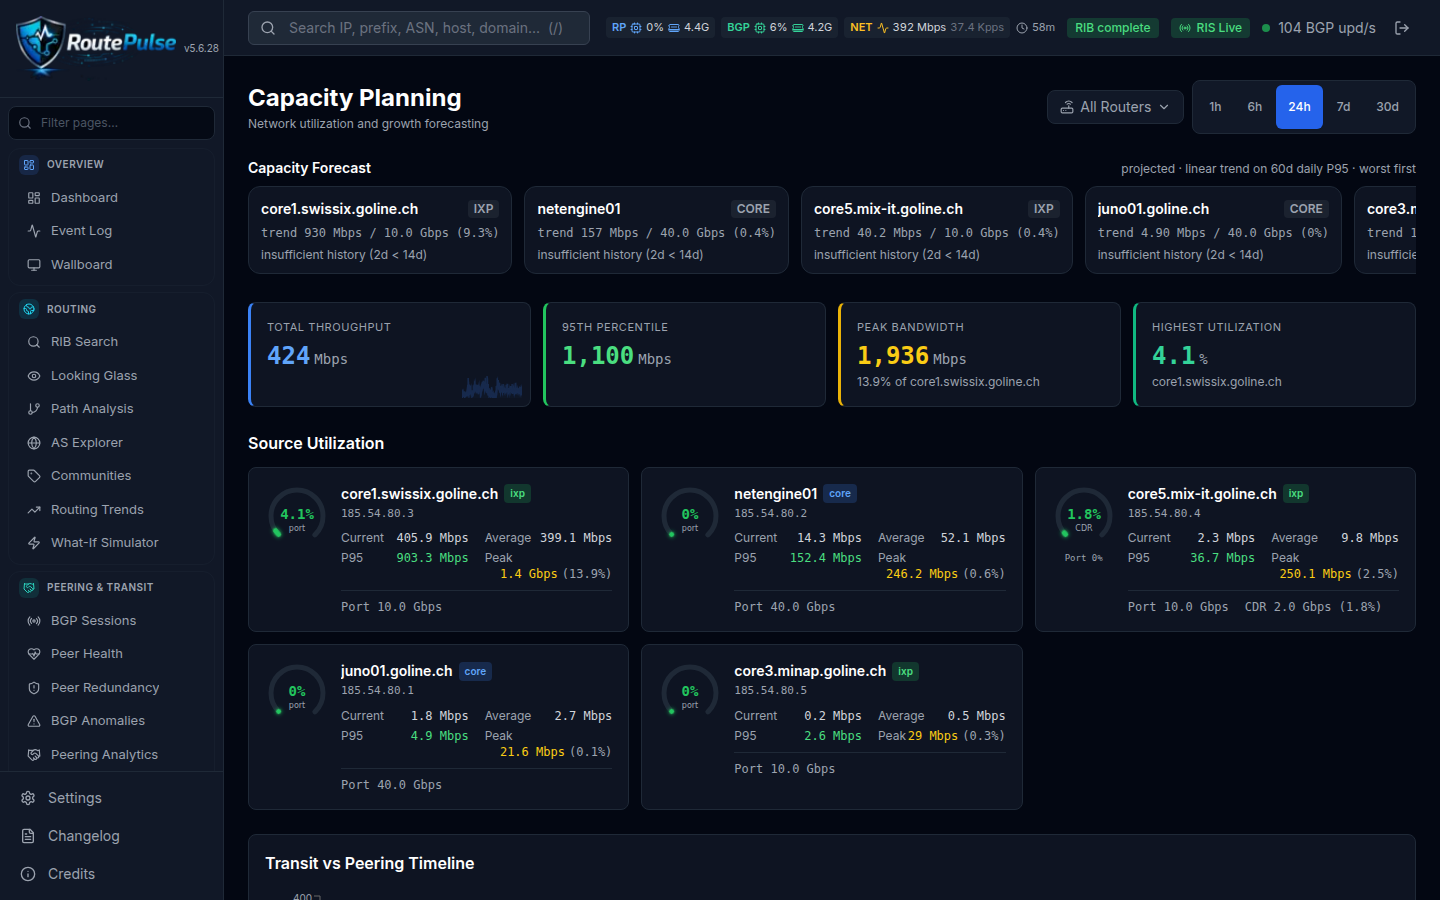
📈 Capacity Planning →
95th-percentile billing, forecasts, commit burn and thresholds per source and per peer — with anomalies when the trend breaks.
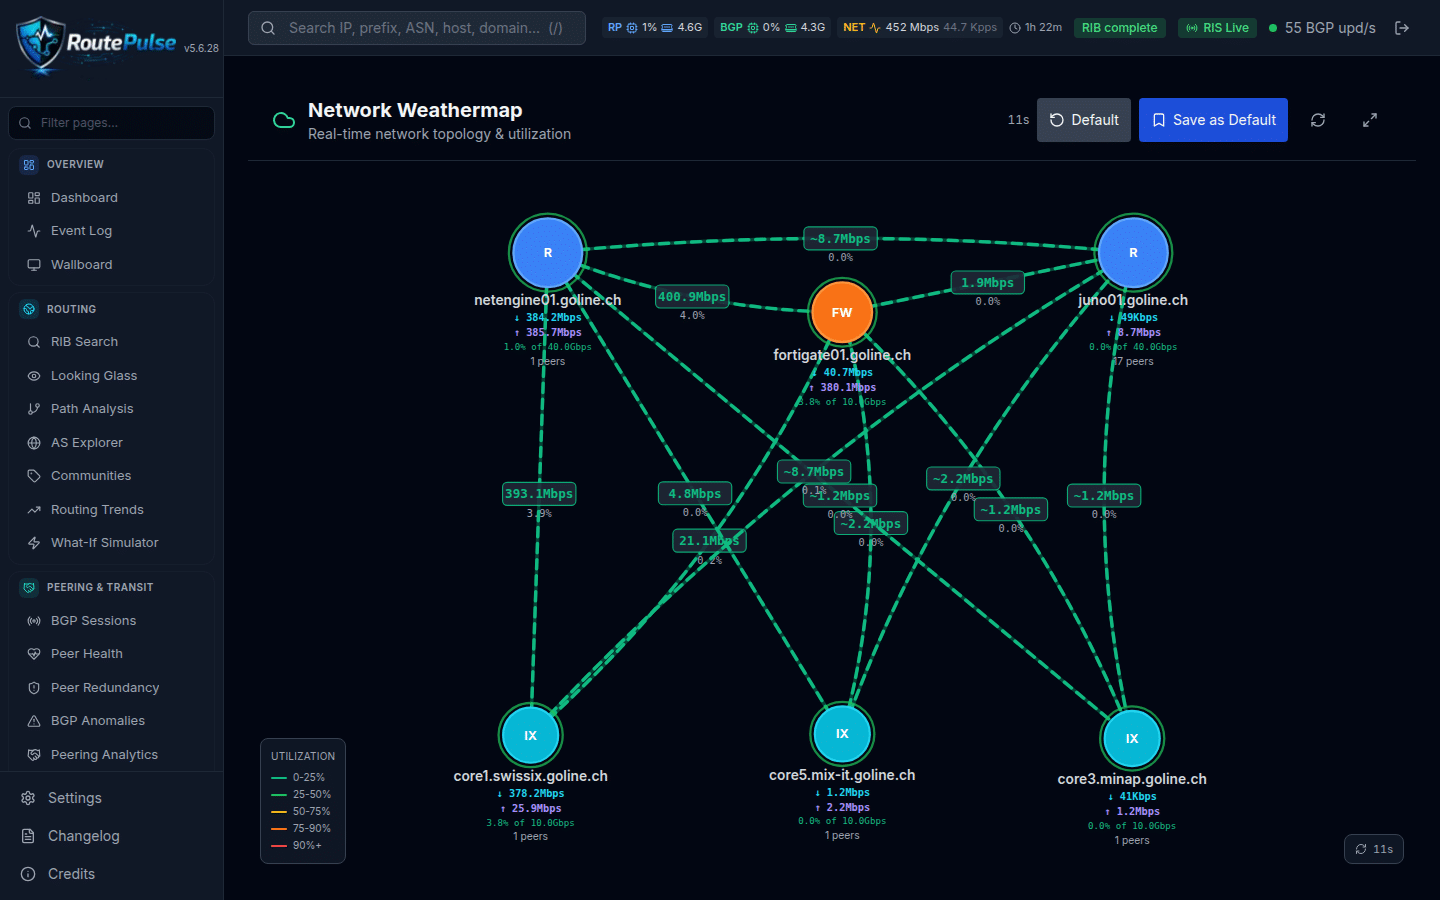
💶 Transit Cost & Weathermap →
What each transit really costs, when it runs out, and a live weathermap of the network as it is right now.
Peering & ISP Management
🤝 Peering Analytics →
Peering candidates ranked by real traffic and AS-path adjacency, enriched with PeeringDB, so the next session pays for itself.
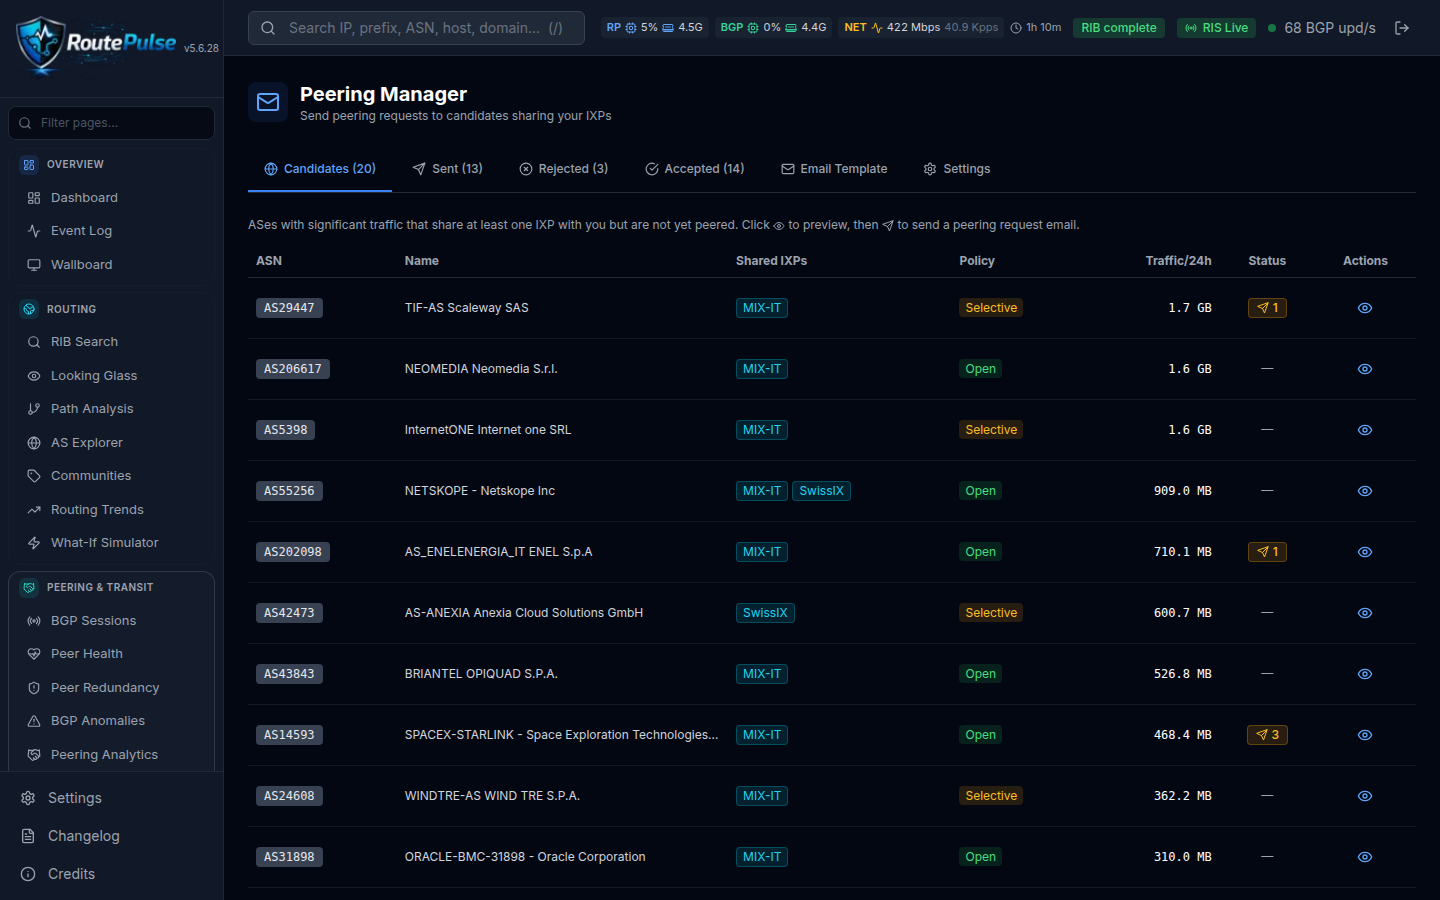
📋 Peering Manager
Session board, requests, IXP presence and a PeeringDB mirror of 64 k netixlan rows — the peering desk in one page.
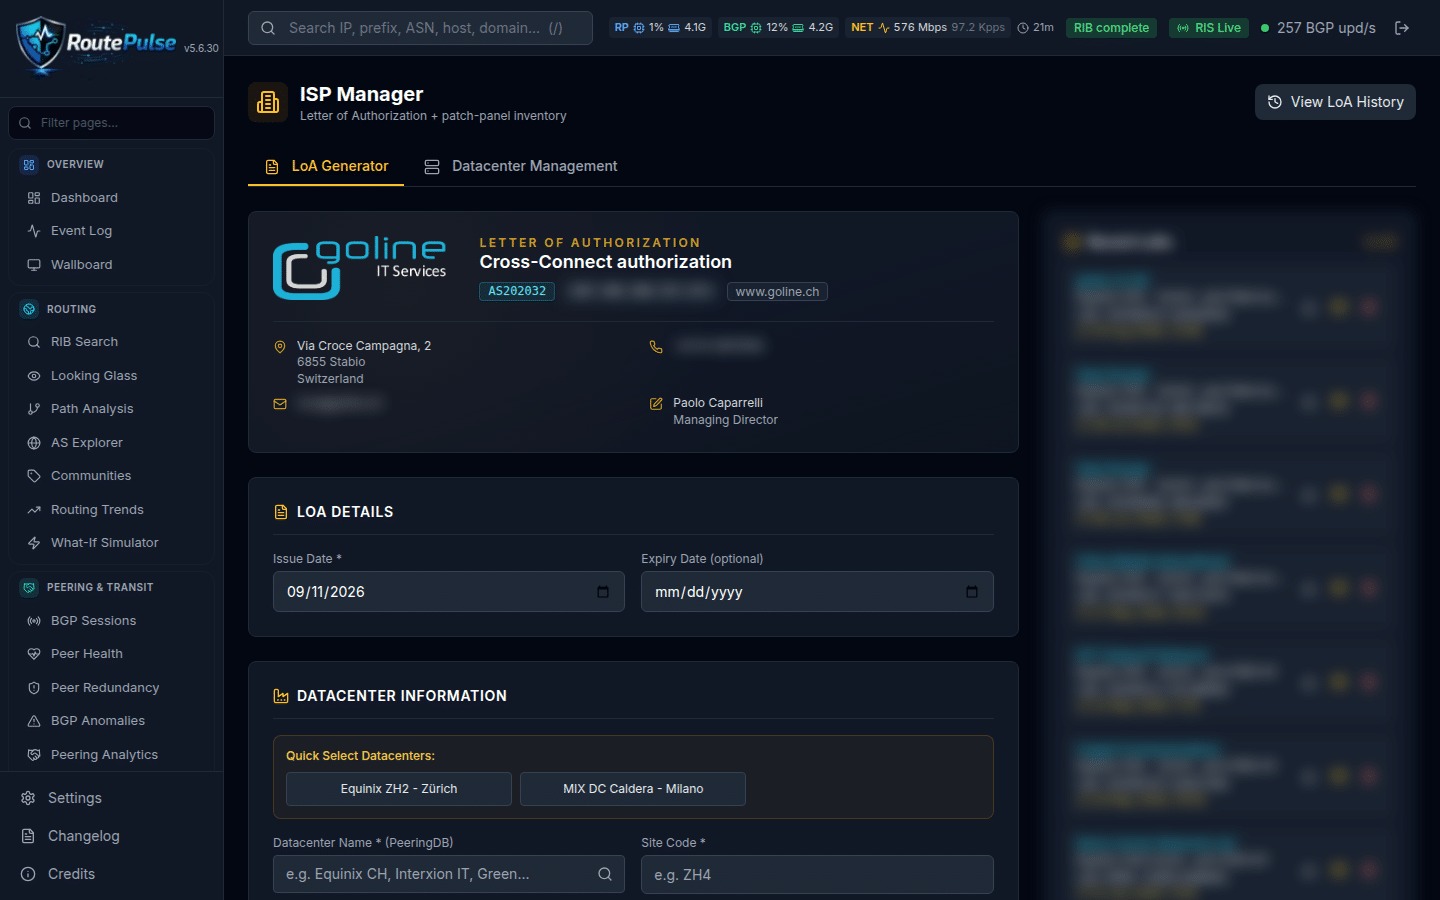
🏢 ISP Infrastructure Manager
Customers, prefixes, letters of authorisation with a public verifier, and the RIR objects behind them.
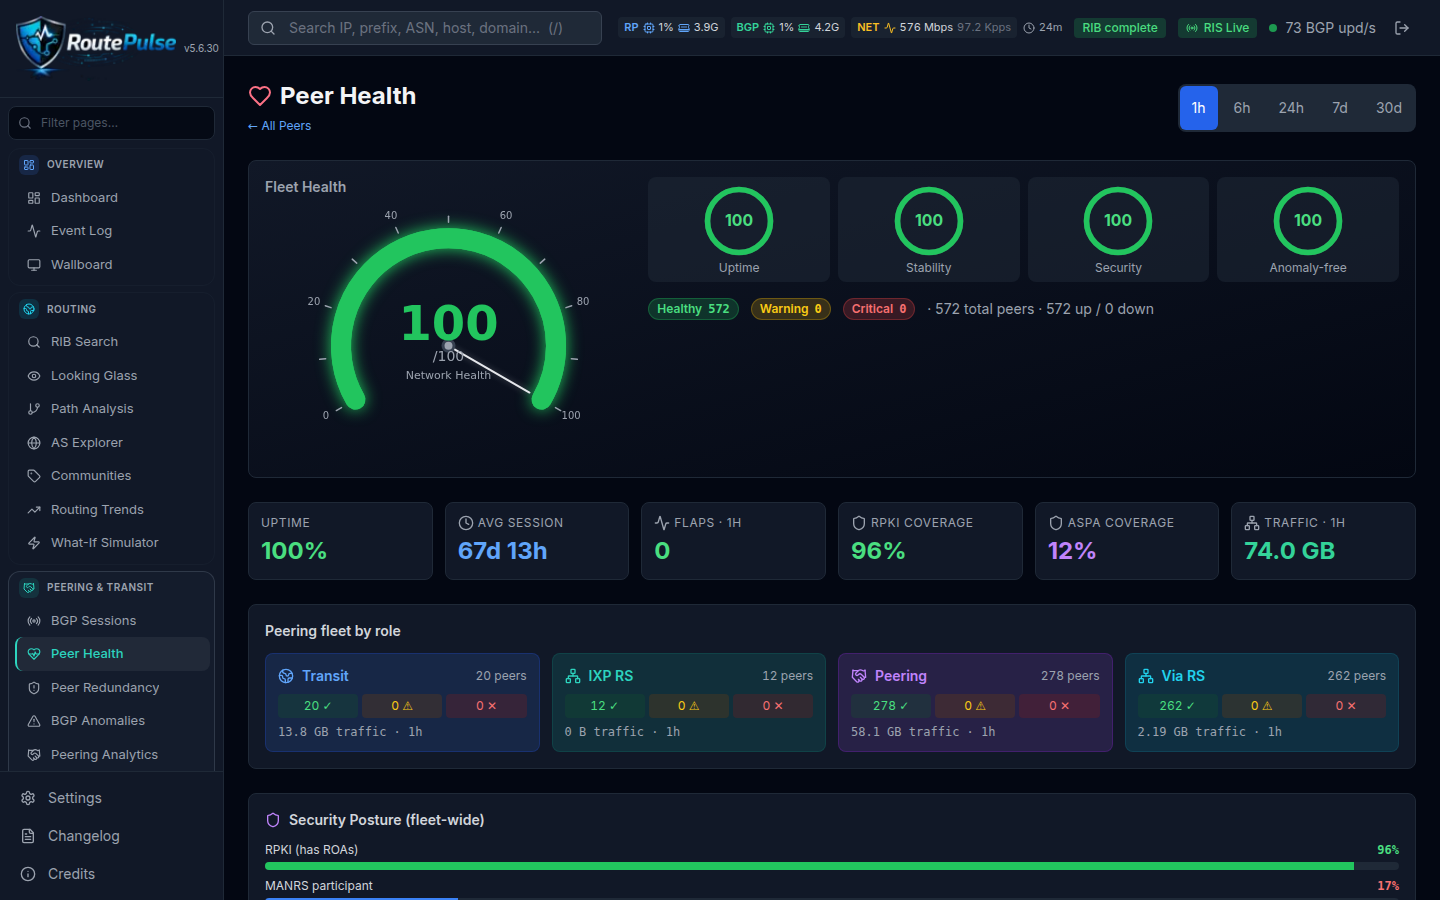
🔁 Routers, Sessions, Health & Redundancy
Every router and BGP session with uptime, flaps and SNMP state, peer health over time and a redundancy view per transit.
Threat Detection & Intelligence
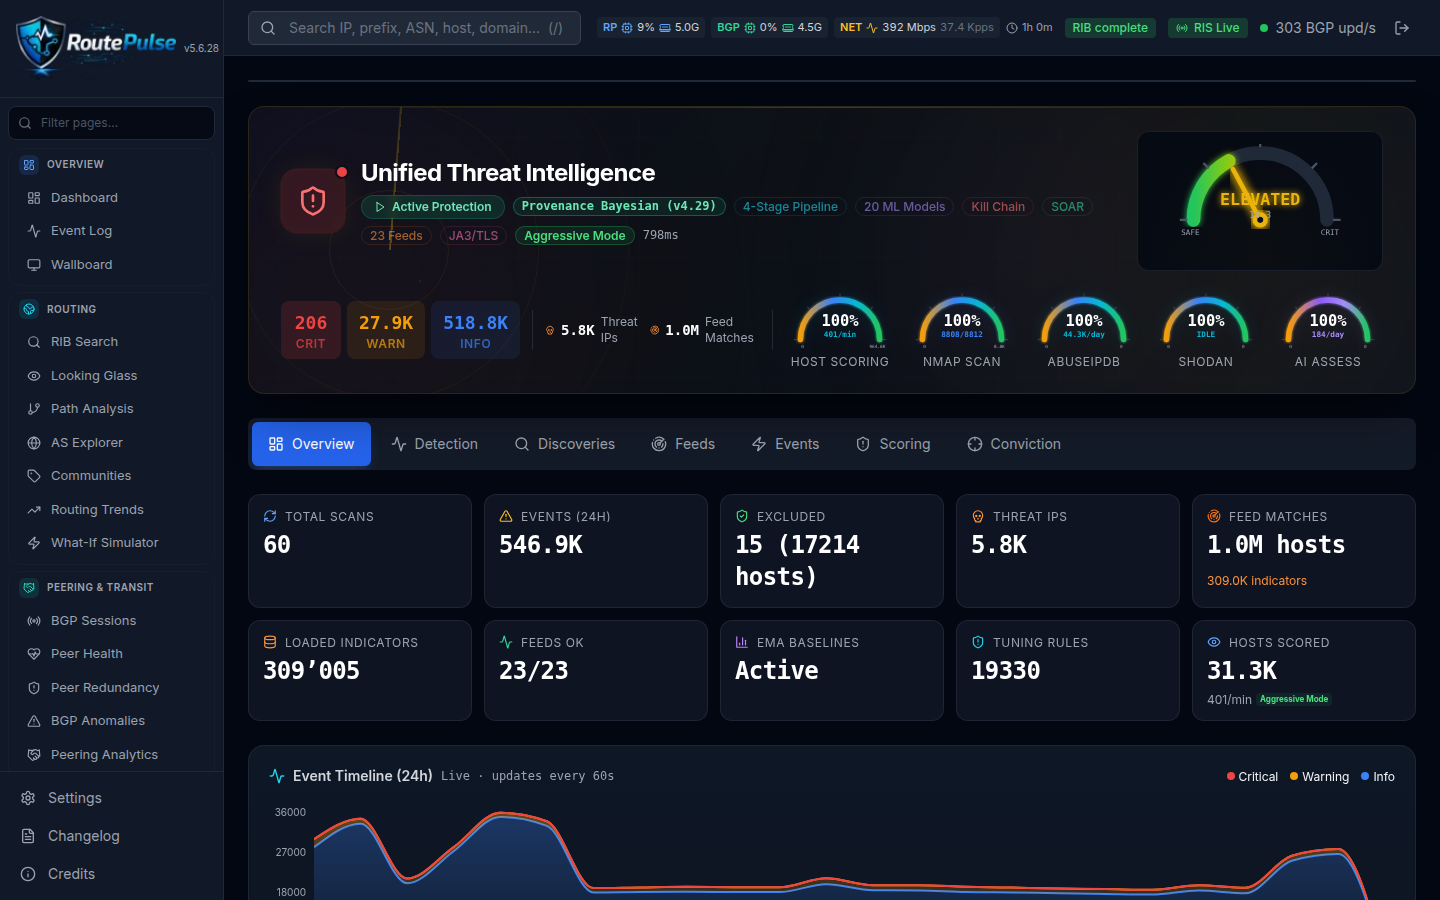
🧮 5-Pillar Threat Scoring →
Cyber events, behaviour, machine learning, reputation and feeds fused into one 0–100 score for every host that touches your network.
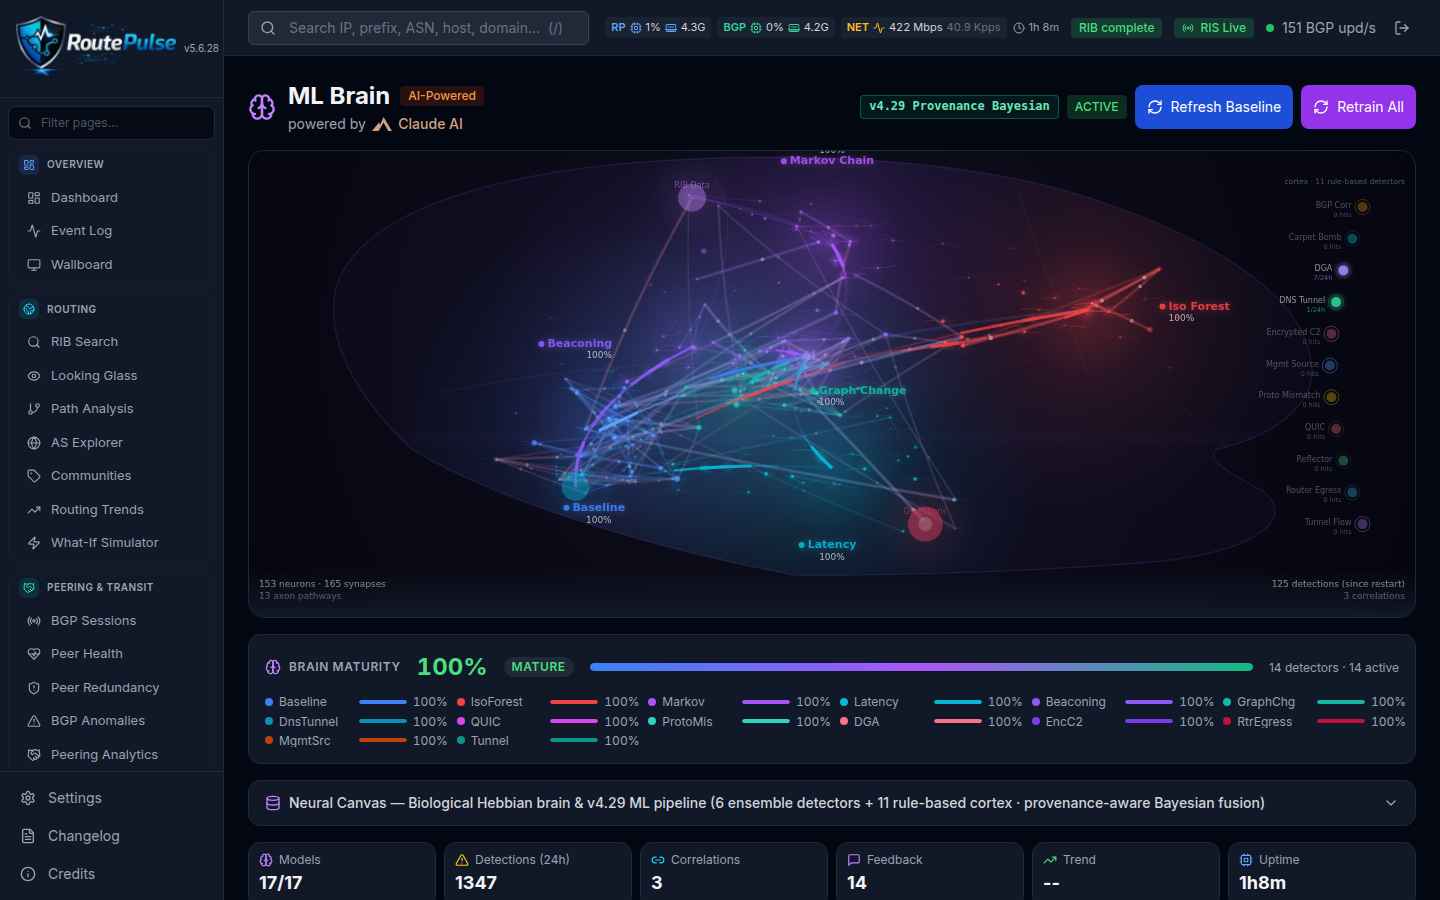
🧠 ML Brain — 21 models →
Isolation forest, Markov chains, beaconing, graph change and more; an ensemble with ADWIN/DDM drift detection and per-role baselines.
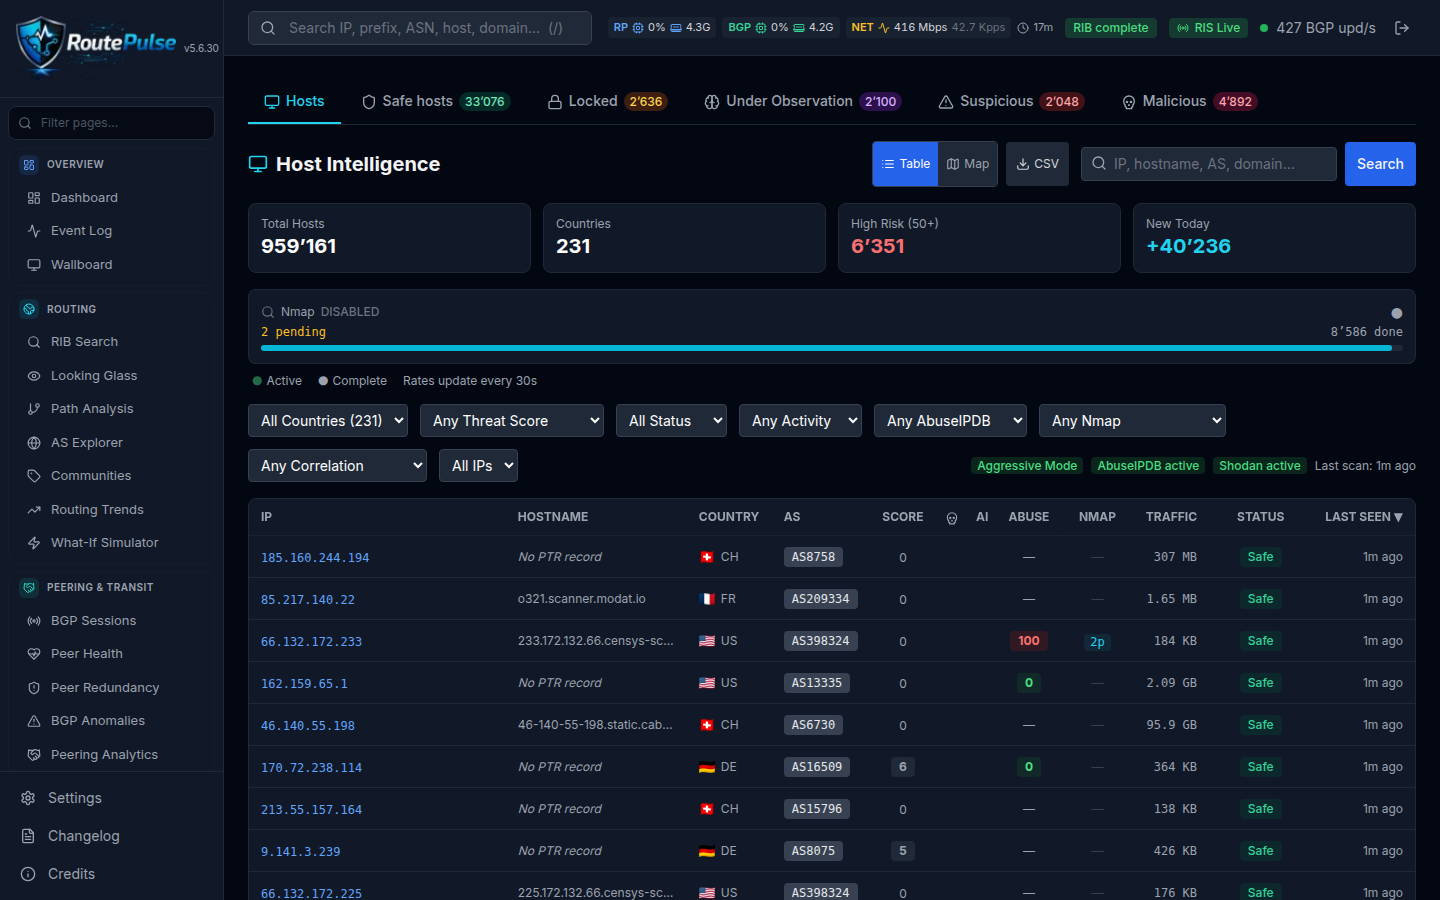
🃏 Host Intelligence →
A card and a behaviour diary for 966 K hosts: what it did, when the score moved, and why. Two-tier AI assessment where a verdict would change a status.
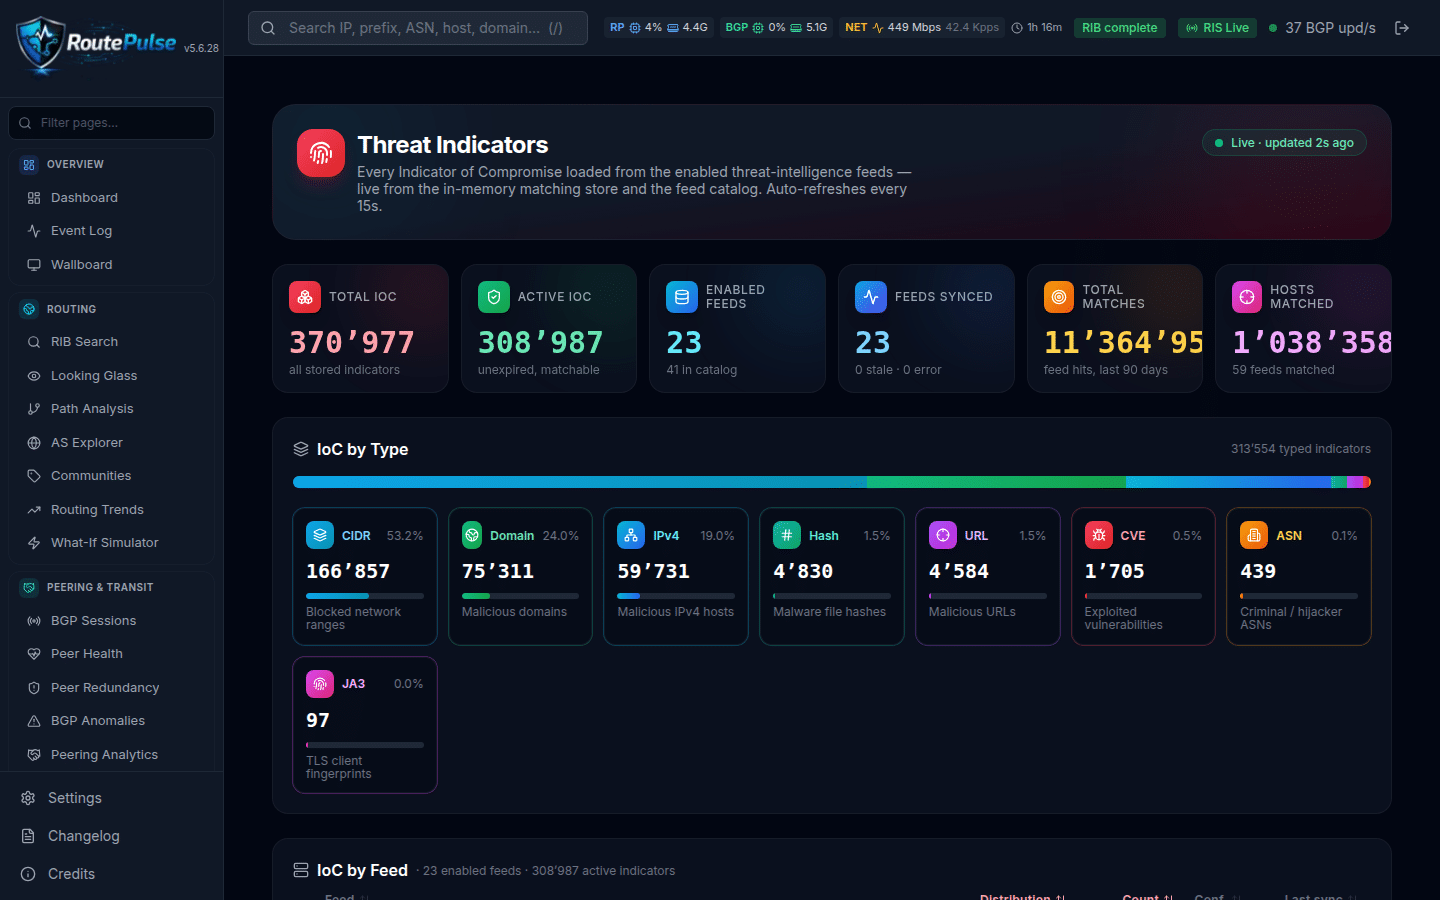
🔗 Threat Feeds & CISA AIS
41 feeds including CISA Automated Indicator Sharing over mutual TLS, MISP both ways, 370 K indicators with bloom and CIDR-trie matching.
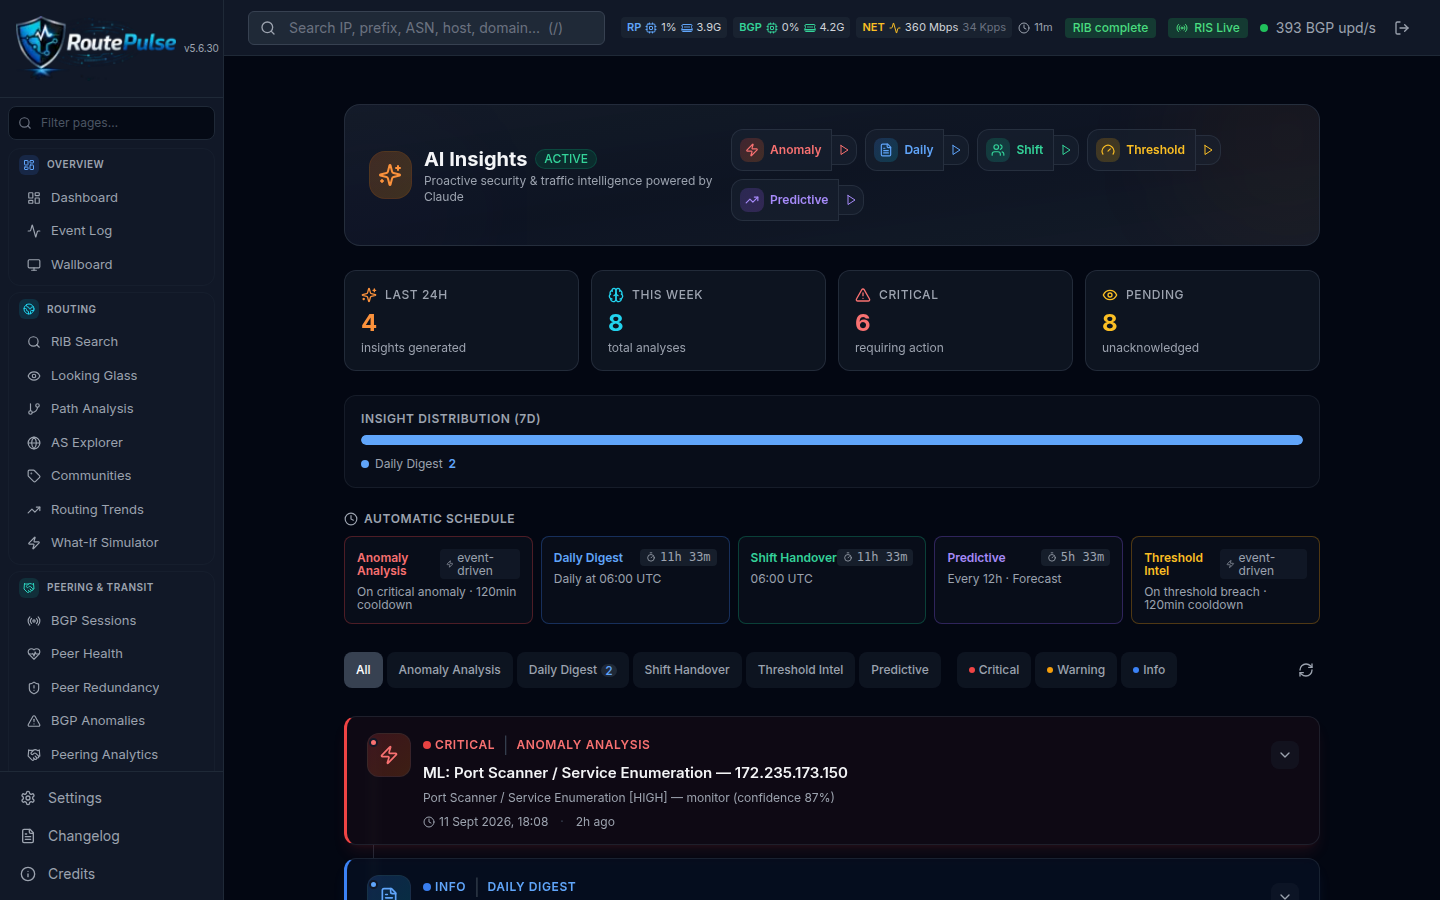
🕵️ ANIE, AI Analyst & AI Insights →
An autonomous SOC pipeline that investigates correlations, a chat analyst that runs tools on your real data, and scheduled digests with the measured flow section.
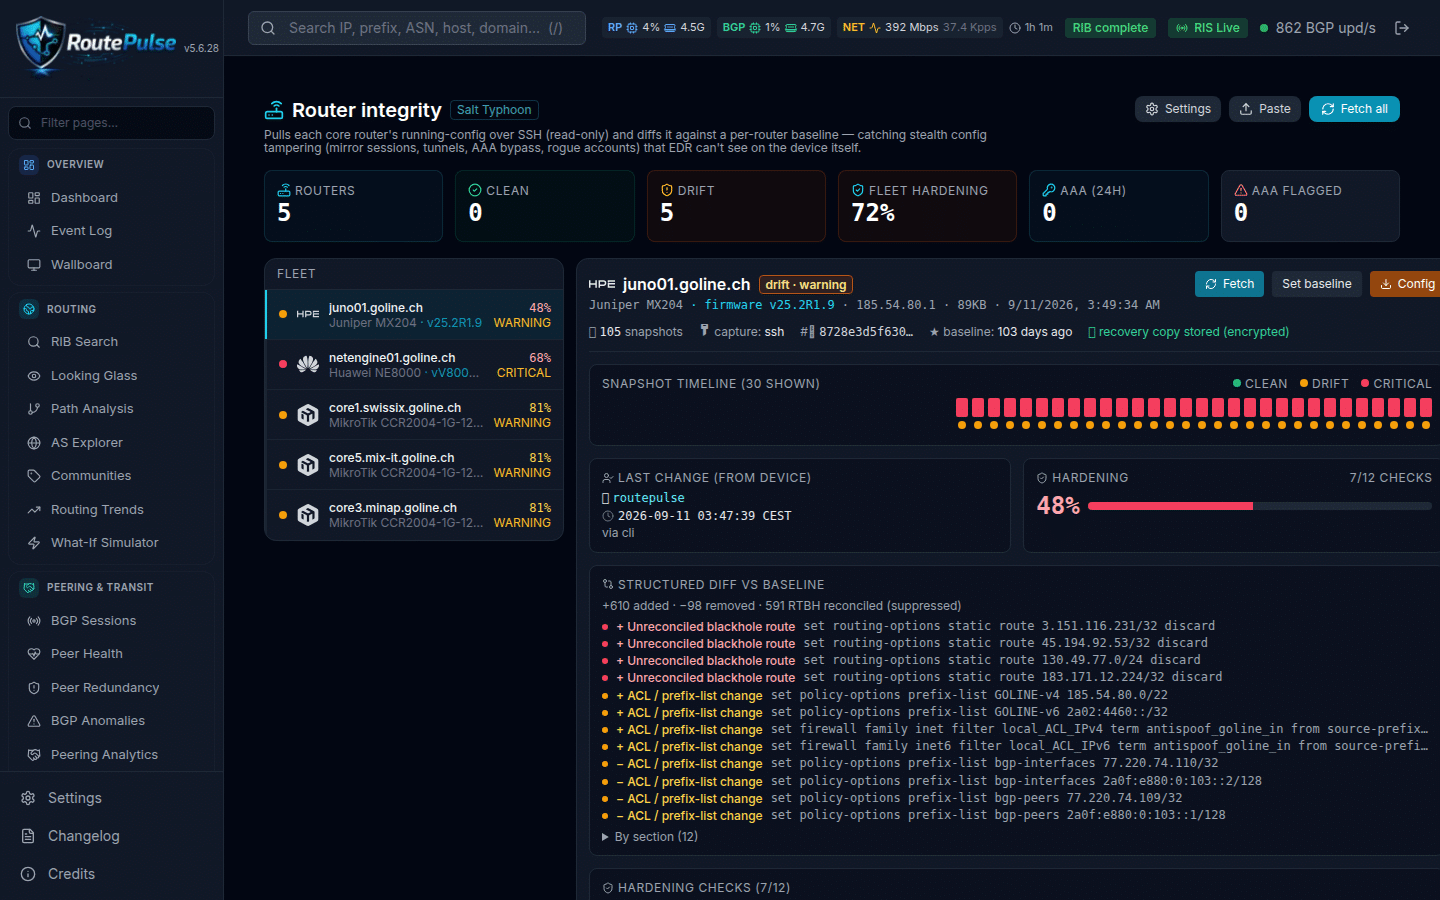
🔩 Router Config-Integrity (Salt Typhoon)
Config drift against a baseline, per-vendor hardening score, change attribution and an encrypted emergency recovery vault — the compromise class EDR cannot see.
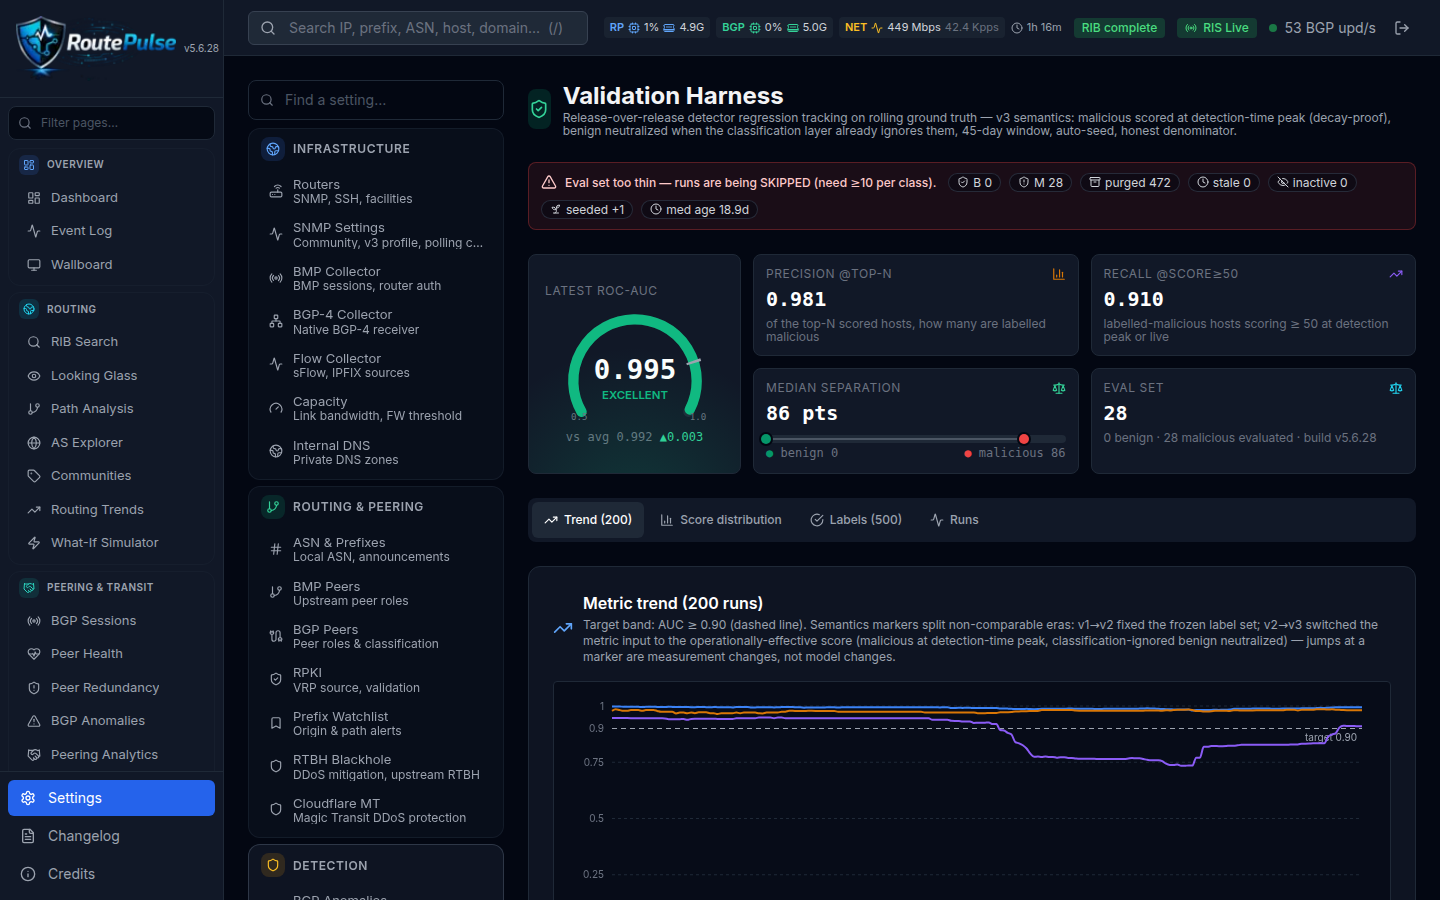
📏 Validation Harness
The score grades itself nightly against operator verdicts and feed corroboration — ROC-AUC 0.994 on 11 Sep 2026 — and conformal prediction bounds the false-discovery rate.
Active Defense
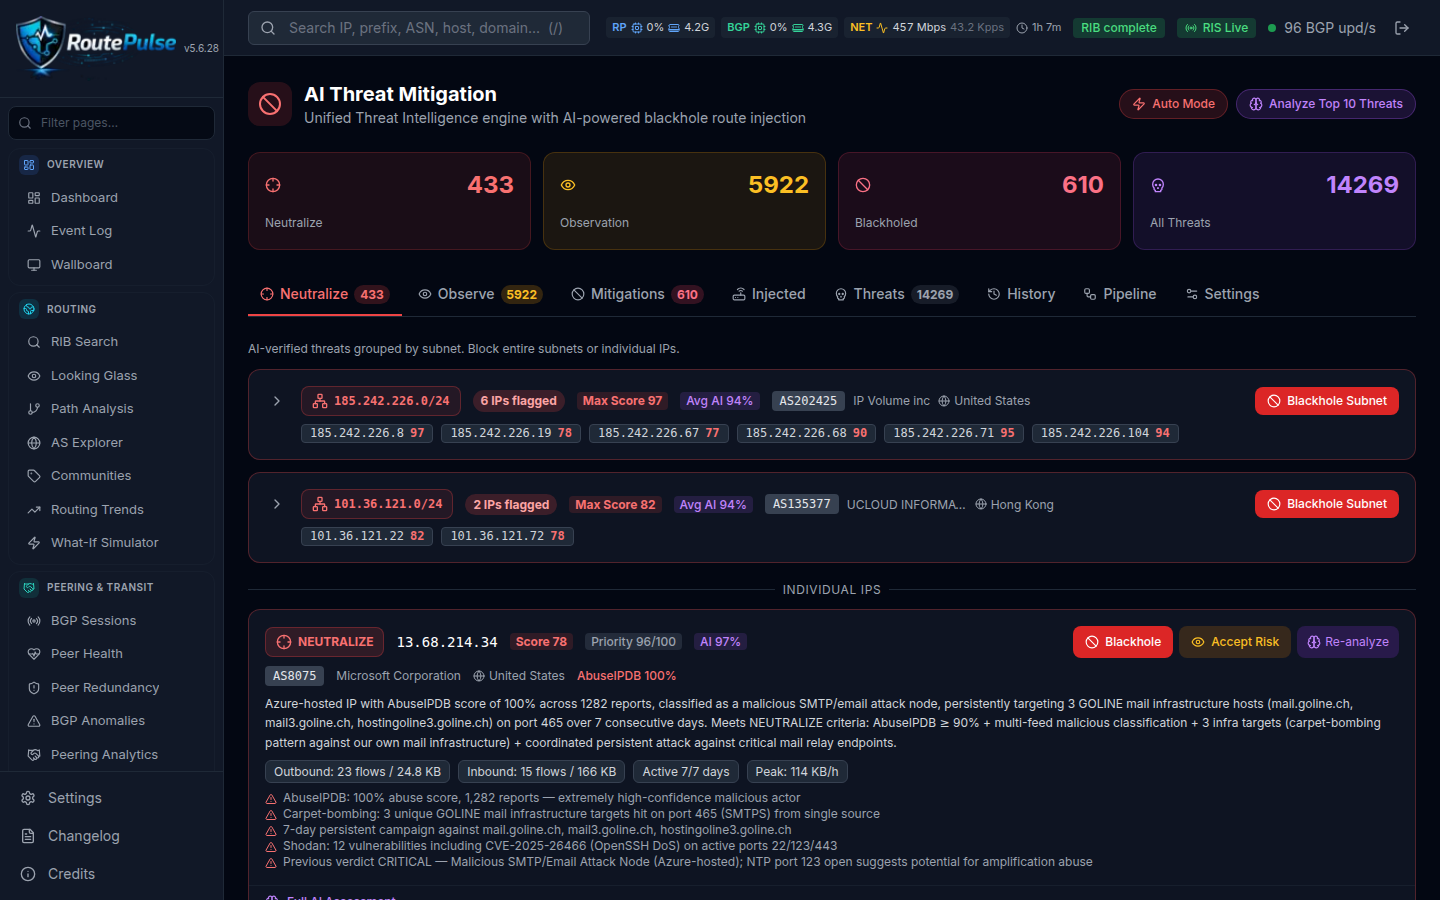
⚡ Automated Mitigation & Conviction Engine →
A 5-tier ladder — observe, monitor, rate-limit, FlowSpec, RTBH — driven by SPRT, Thompson sampling and conformal guarantees, executed over SSH on your core routers.
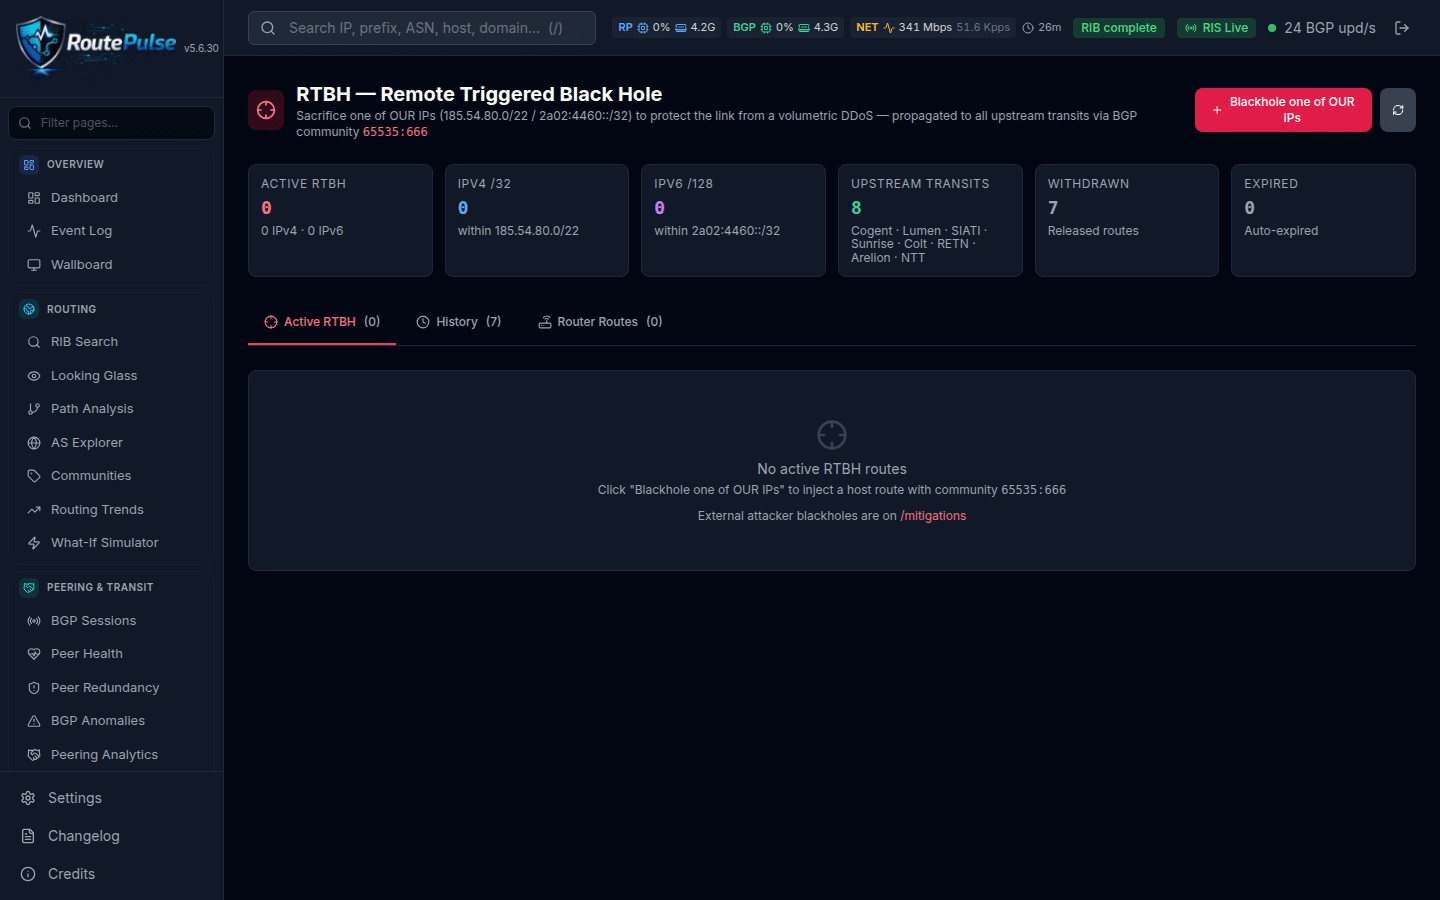
🕳️ RTBH & FlowSpec
Remote-triggered blackholing across transit providers (RFC 5635/7999) and BGP FlowSpec v4/v6, with whitelists, TTLs and a reconciliation loop.
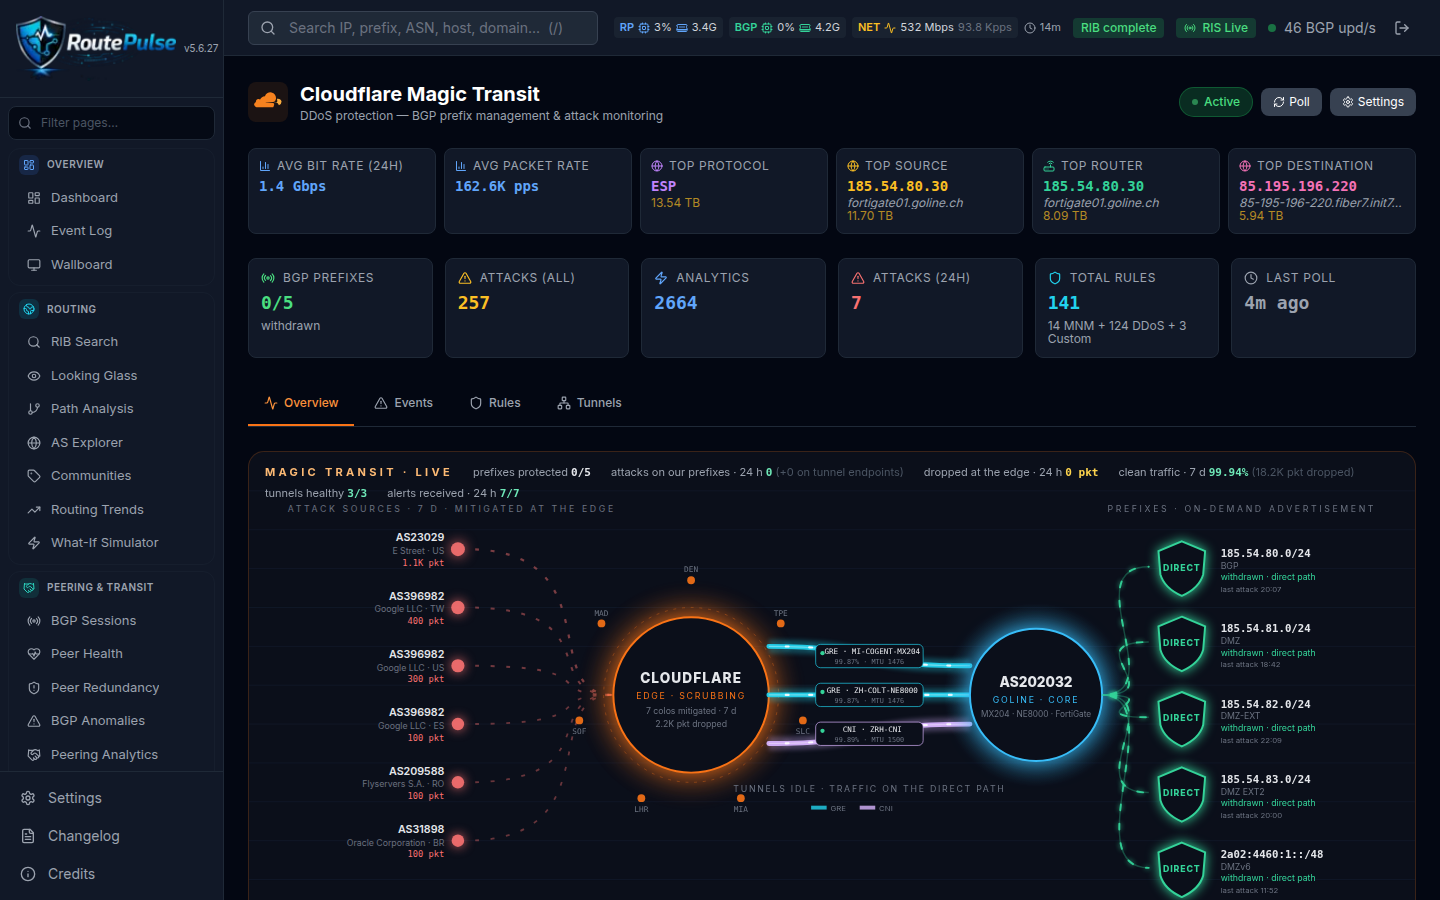
☁️ Cloudflare Magic Transit Stage
Every Cloudflare alert replayed against your own flows: who saw what at the edge and in the core, prefix coverage, flood signature vs mitigated-at-edge.
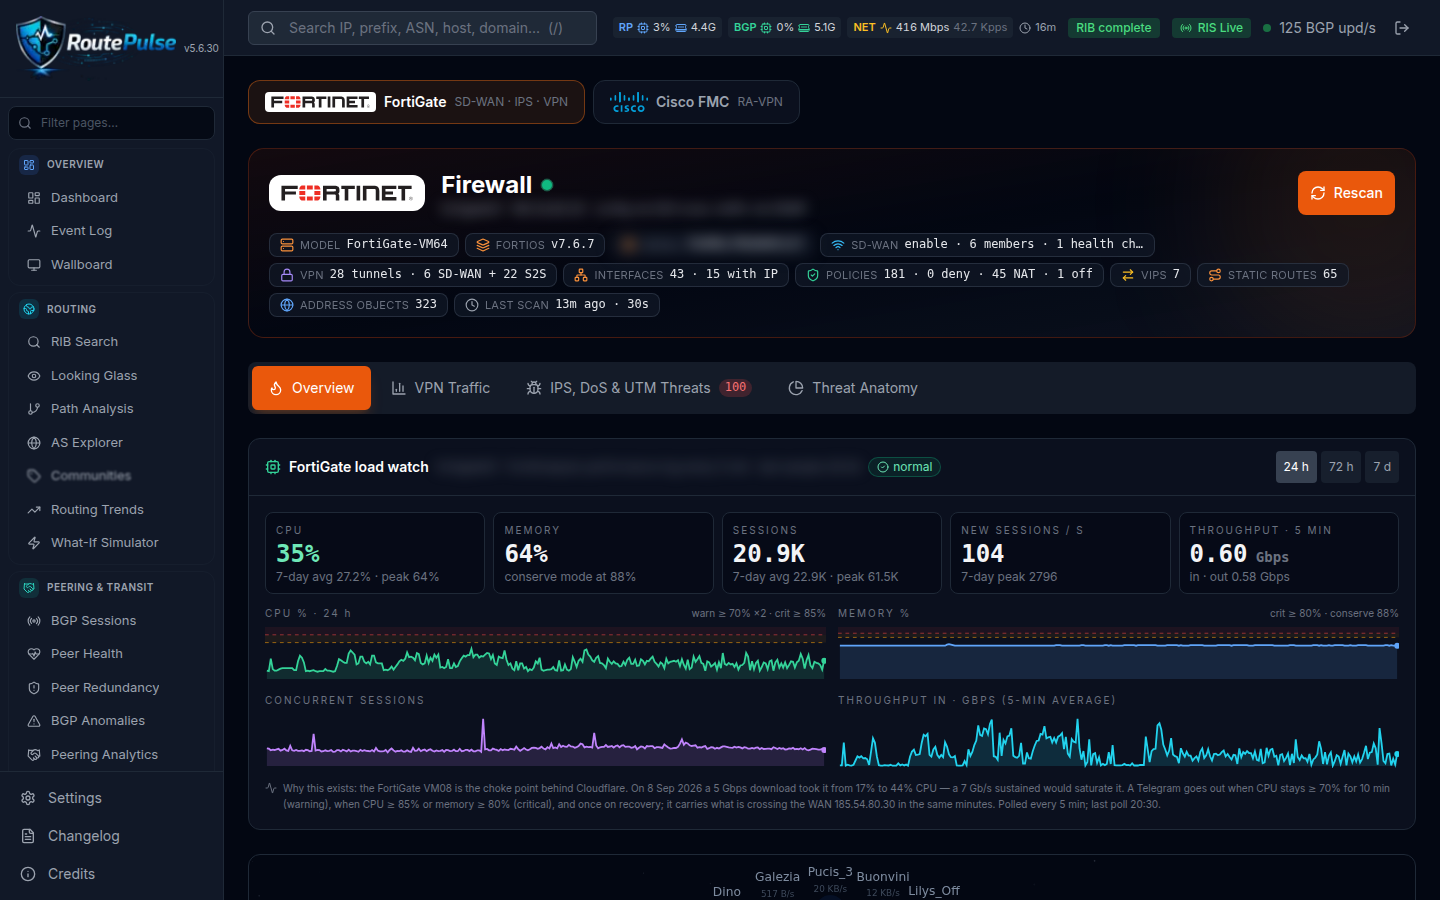
🔐 RA-VPN Siege Ladder (Cisco Secure Firewall) →
The firewall as sensor and actuator: managed shun at 3 real failures, slow-spray catch, /24 at the second IP under siege, origin AS upstream. Default group sinkholed by API.
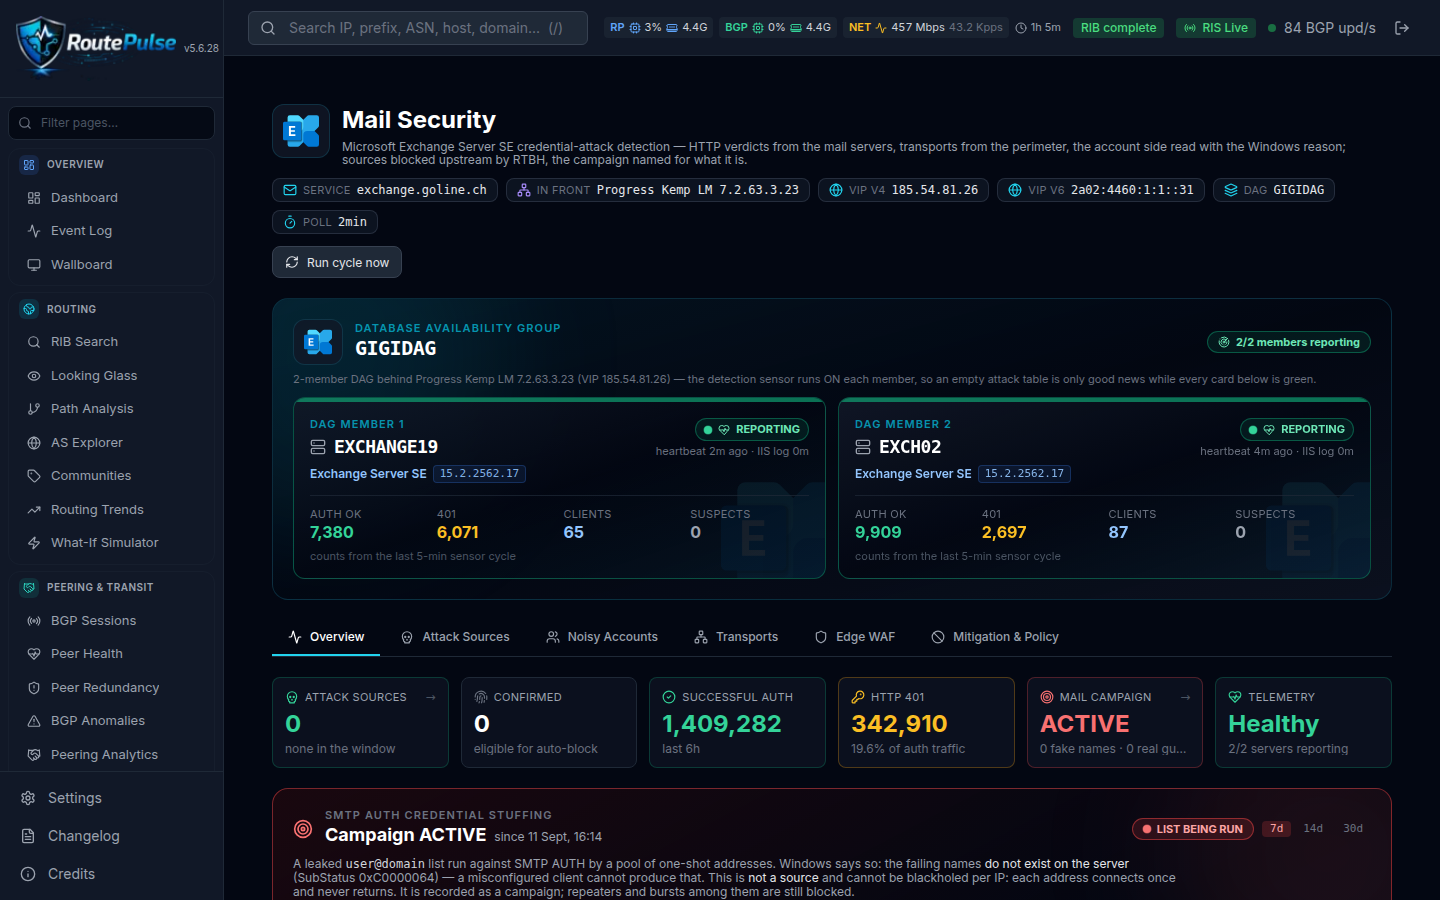
📧 Mail, FTP & Malware Defense →
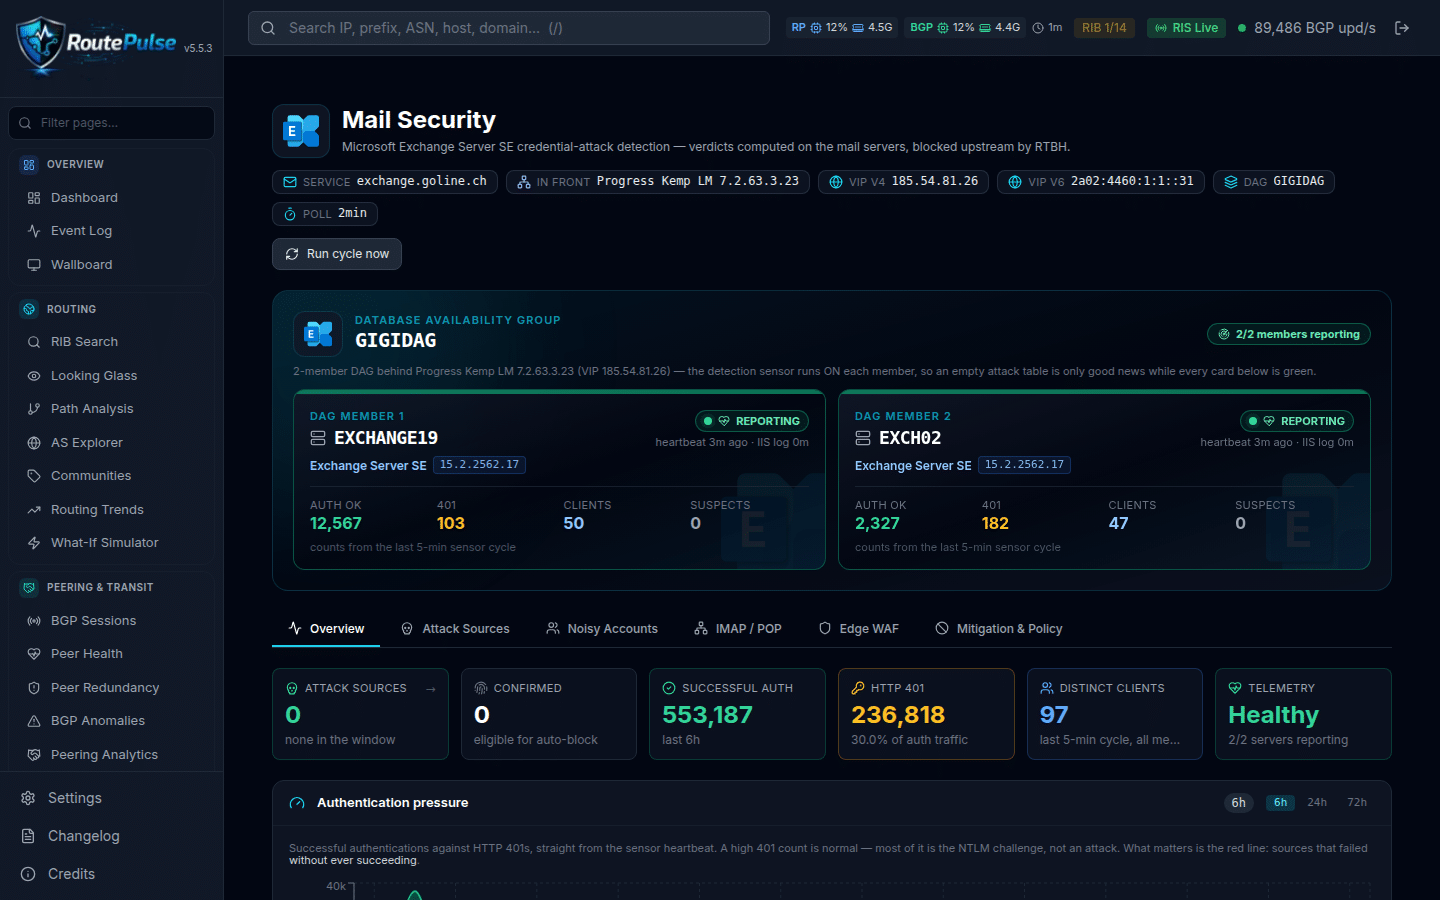
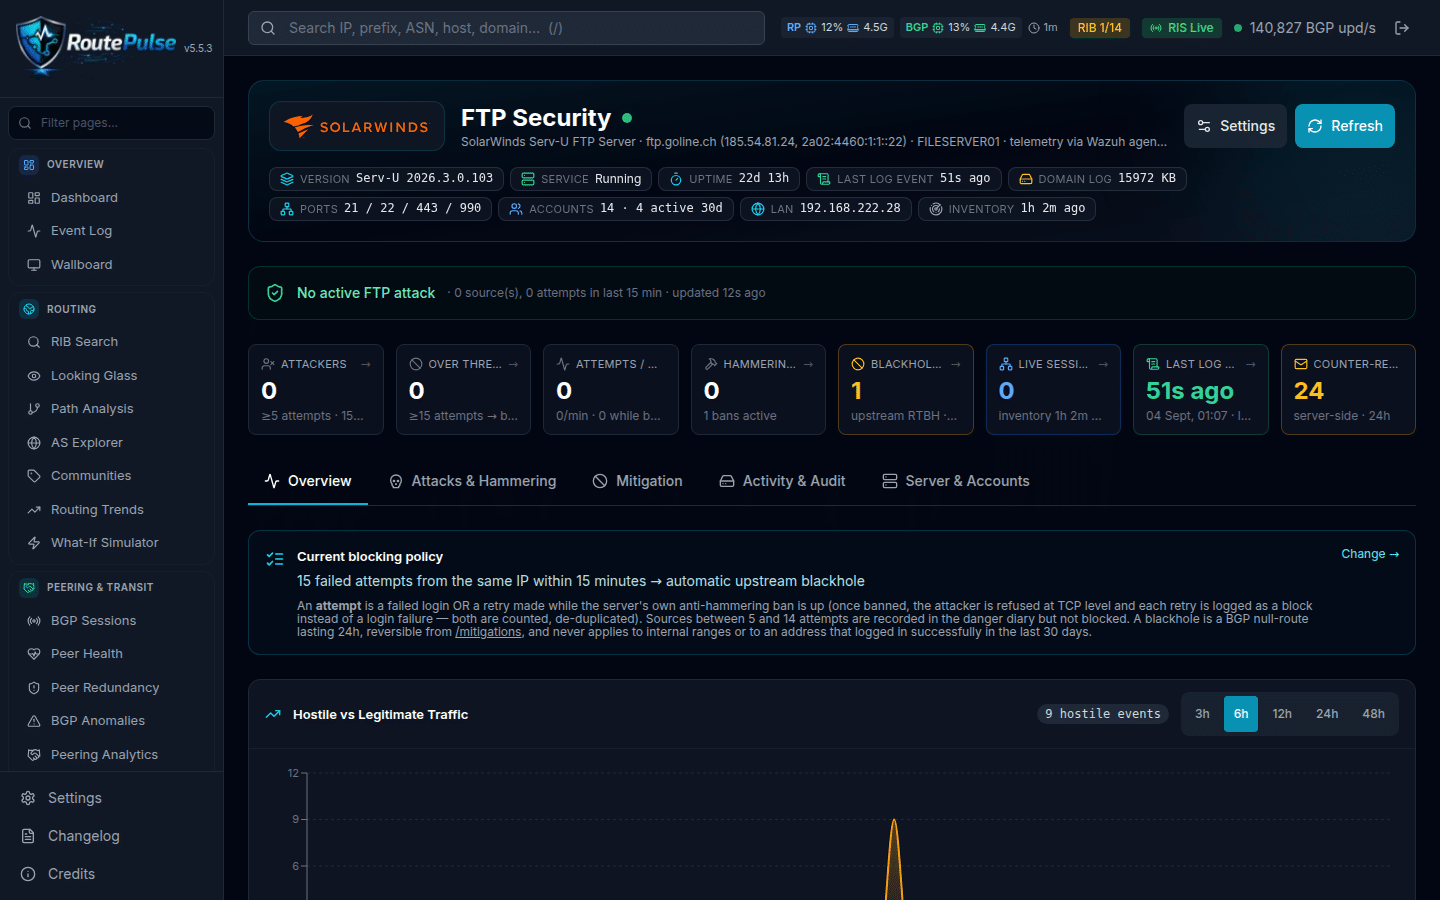
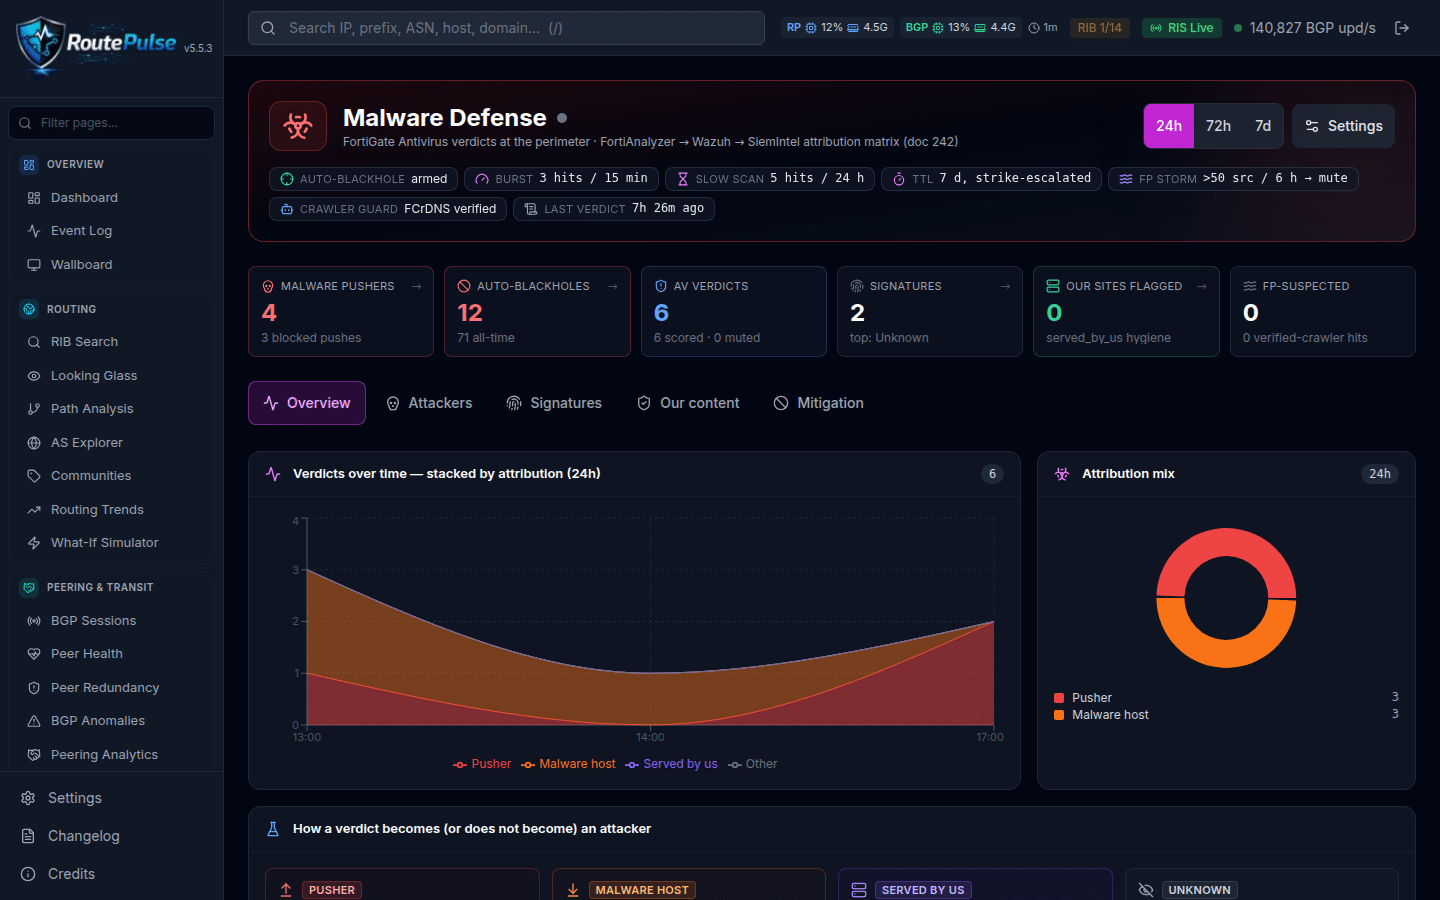
Credential stuffing on Exchange read per account, FTP hammering, perimeter AV blocks attributed by direction — the source is blocked upstream, not just the file.
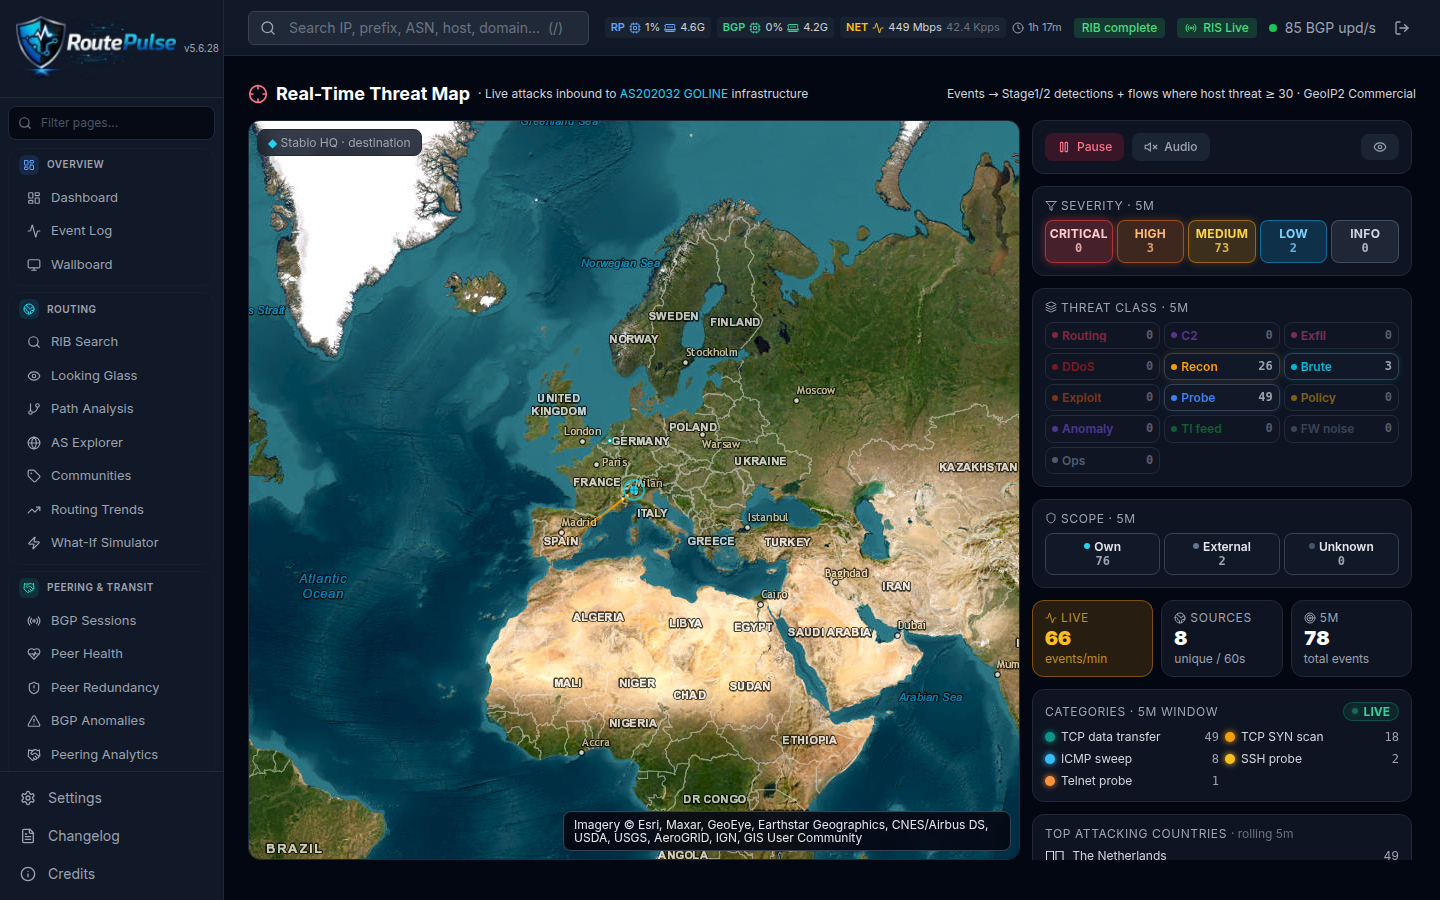
🗺️ Real-Time Threat Map
Every attack in flight on one map, drawn from your own flows and SIEM events, with drill-down to the host behind each arc.
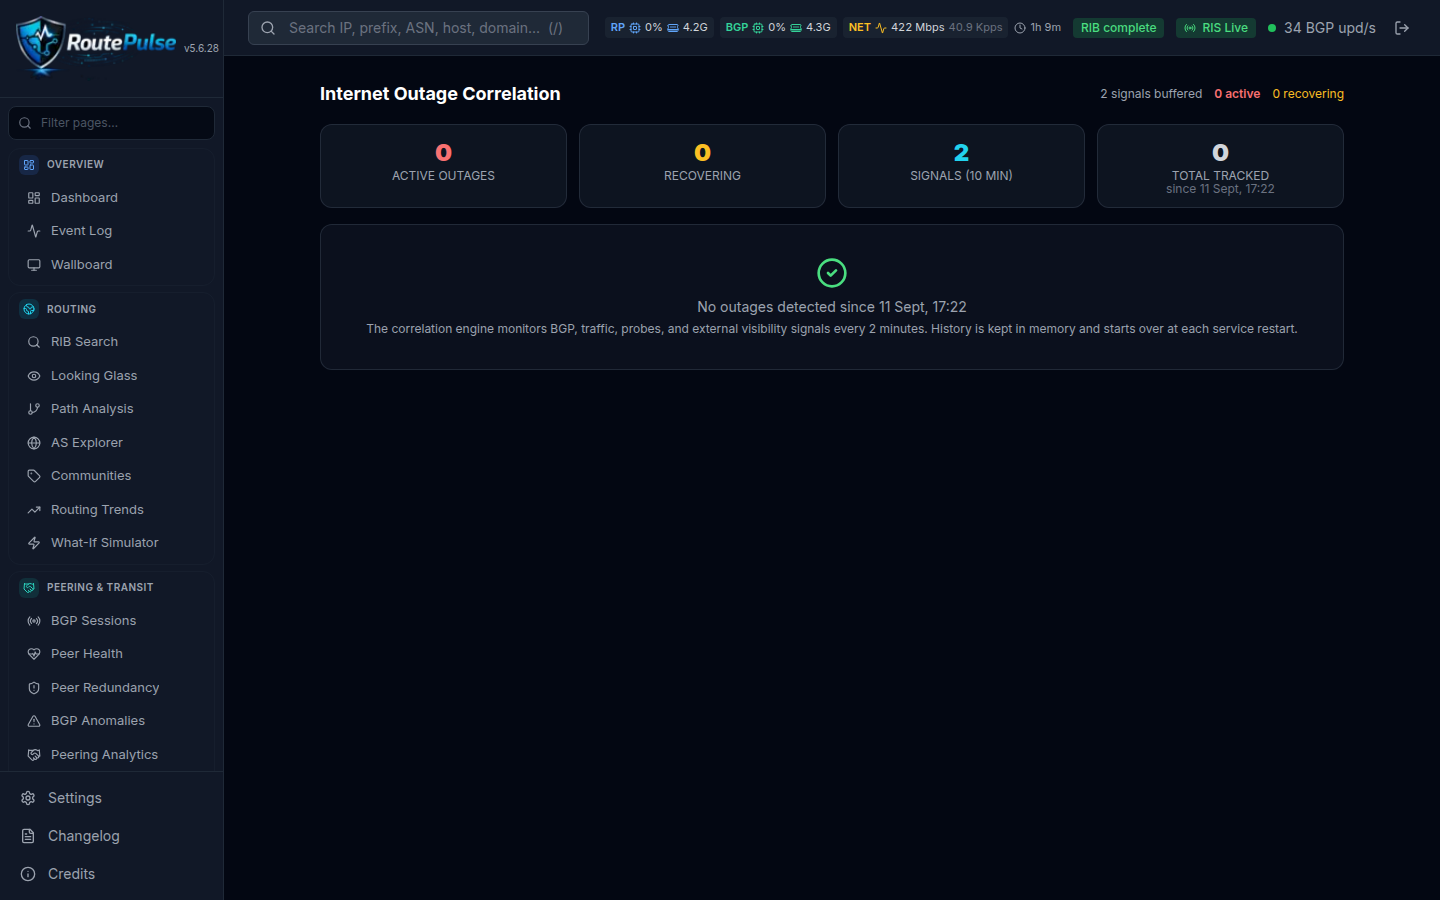
📡 Outage Correlation
Is it us or is it them? Traffic drops correlated with BGP withdrawals, probes and external visibility before the phone rings.
Identity & Endpoint Hygiene
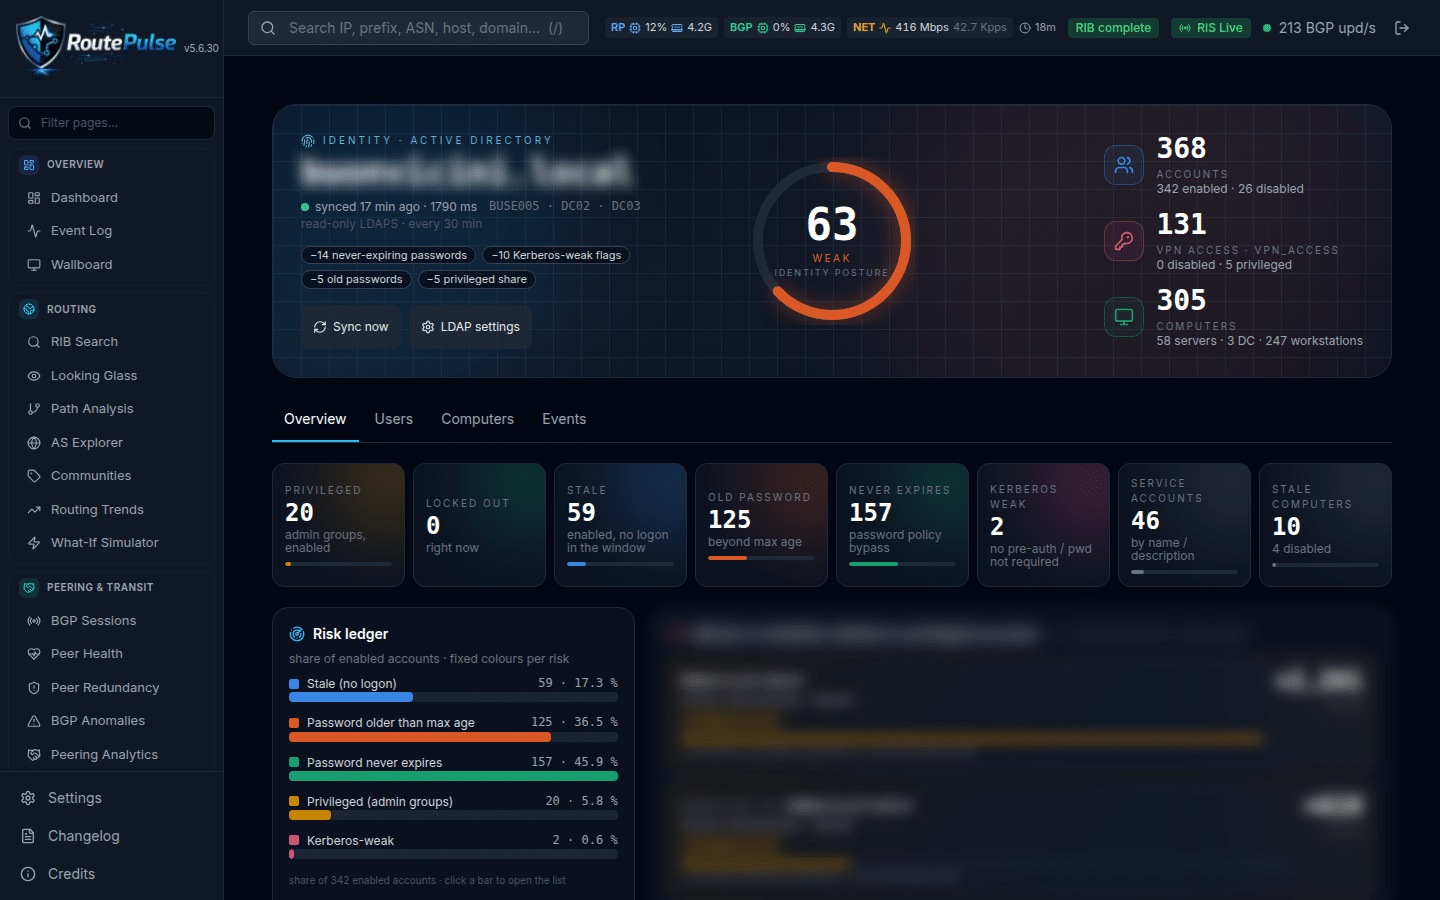
🪪 Active Directory, live
LDAPS lookup of every account seen on VPN, mail and FTP: enabled, entitled, OU, last logon — with the OU tree as a war room.
🧷 One Identity, Every Channel
The same account failing on the VPN, then on Exchange, from a hoster abroad — read as one attack on one person, not three unrelated events.
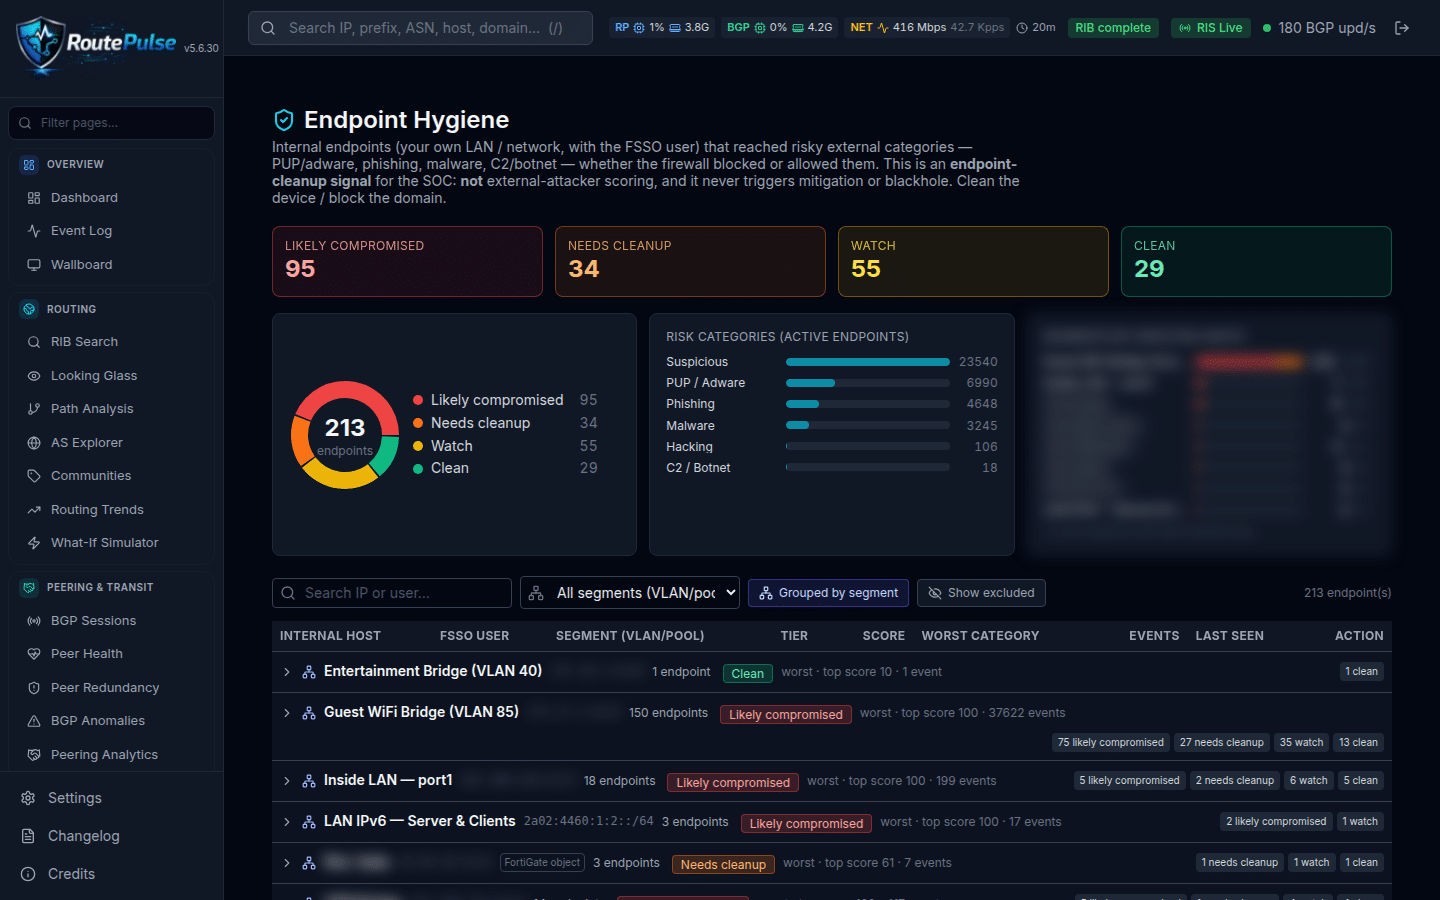
🧹 Endpoint Hygiene
Internal segments from the firewall’s own address objects; an infected host shown with the AD user behind it, so the ticket goes to a person.
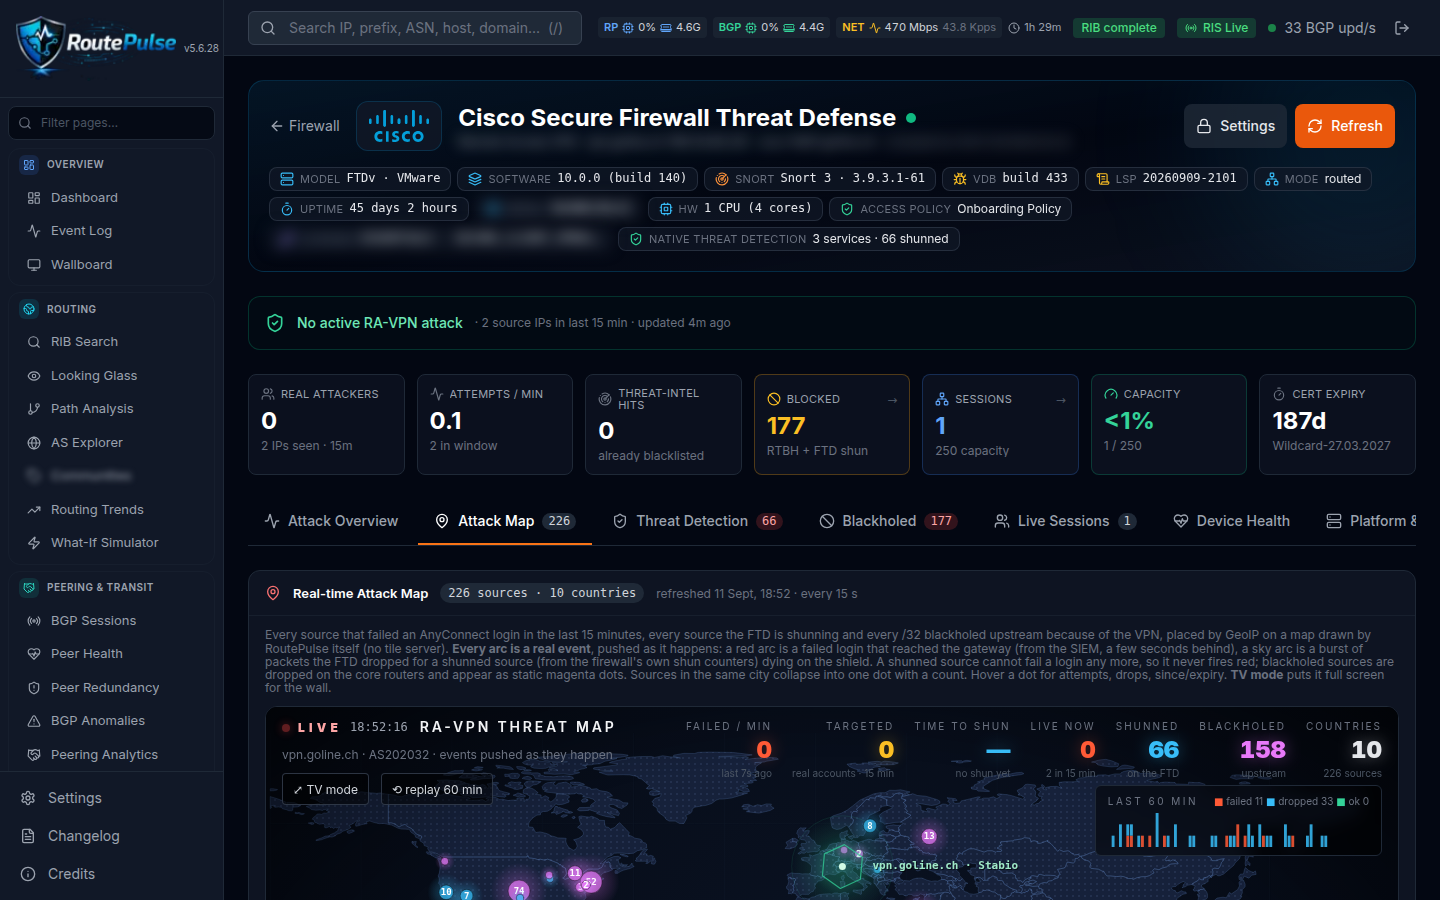
⚖️ The Compromise Judge
A successful login from an attacking source is CRITICAL only on evidence; a real user locked out by the firewall is released automatically.
Compliance & Trust
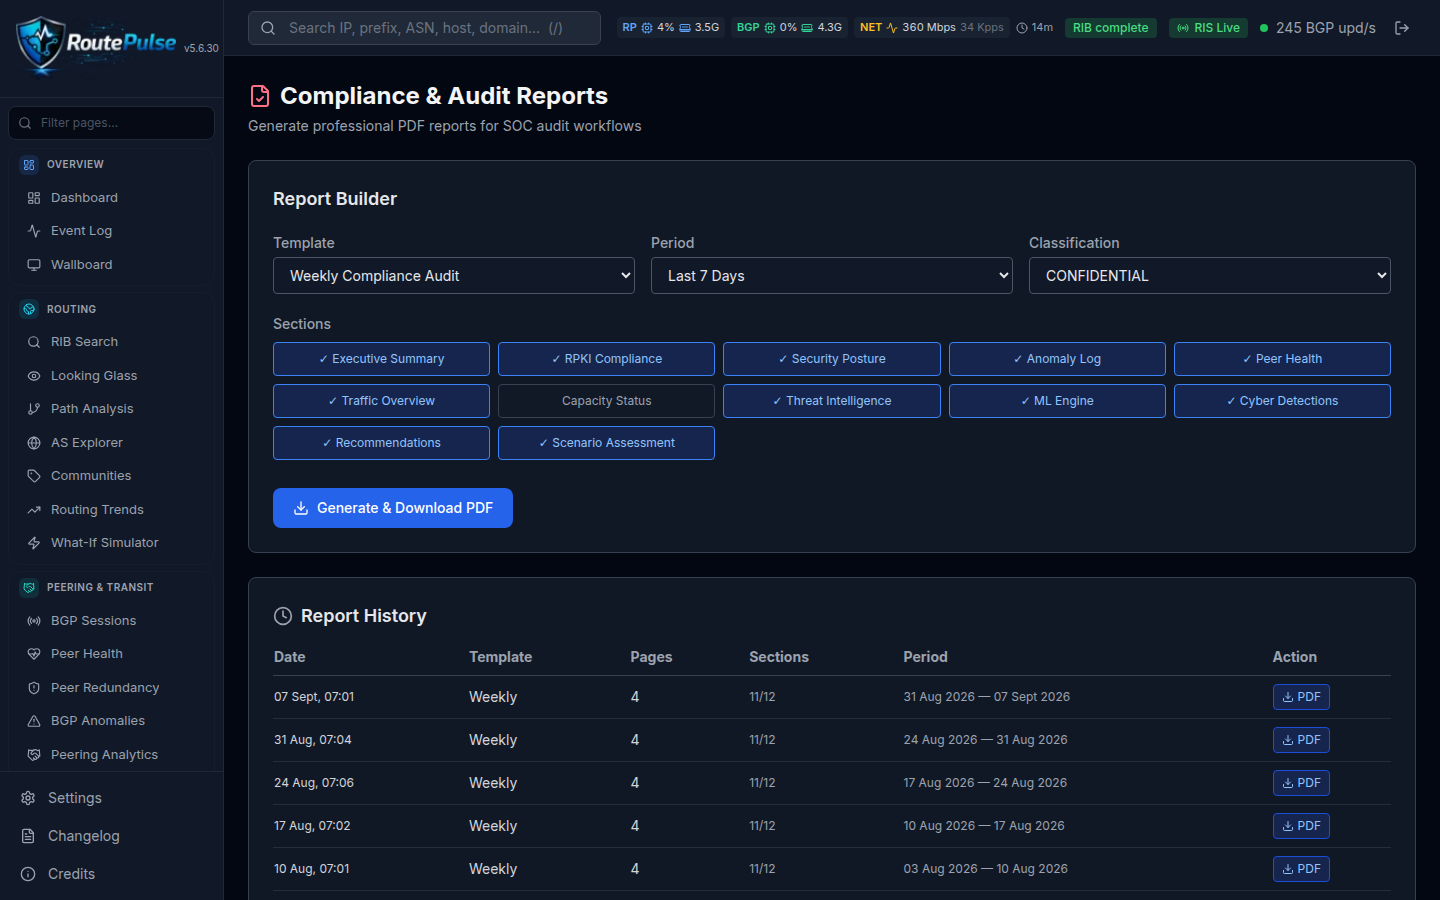
🇪🇺 NIS2 in one click →
Three-stage filing (24 h / 72 h / 30 d) to 30 EU regulators, DORA Article 17 classification, all Ed25519-signed.
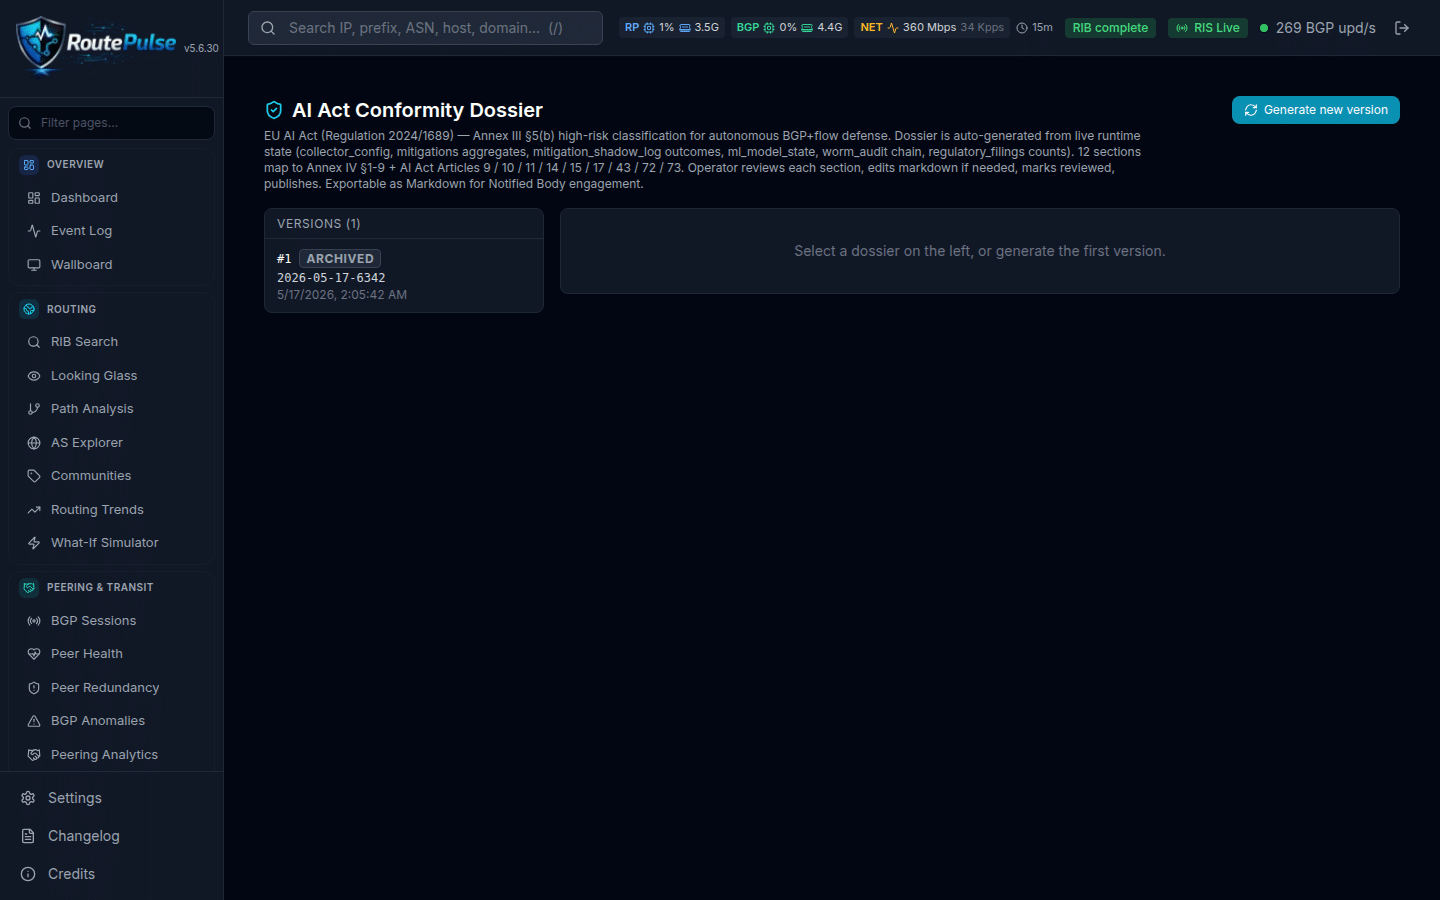
🤖 EU AI-Act Annex IV Dossier
A dossier for the models that take decisions on your network, with bias analysis — unique in the category.
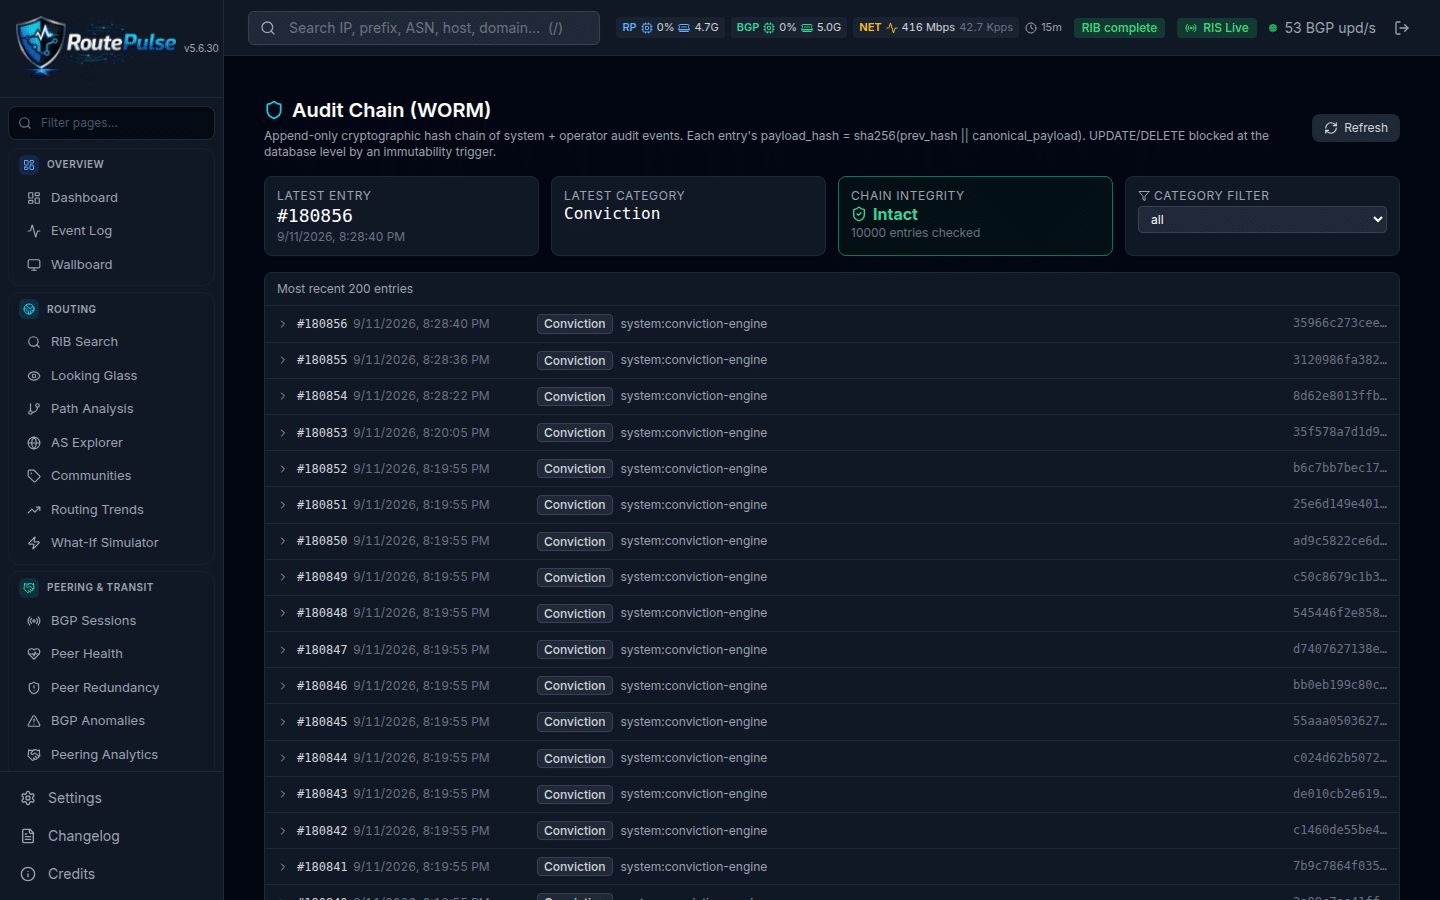
⛓️ WORM Audit Chain
180 K tamper-evident records and counting: every mitigation, every operator action, every configuration change, hash-chained.
🔏 Router Config Snapshots
Daily snapshots of every router, secret-masked, diffed against the baseline — 524 so far on the reference network.
AI Economics & Platform
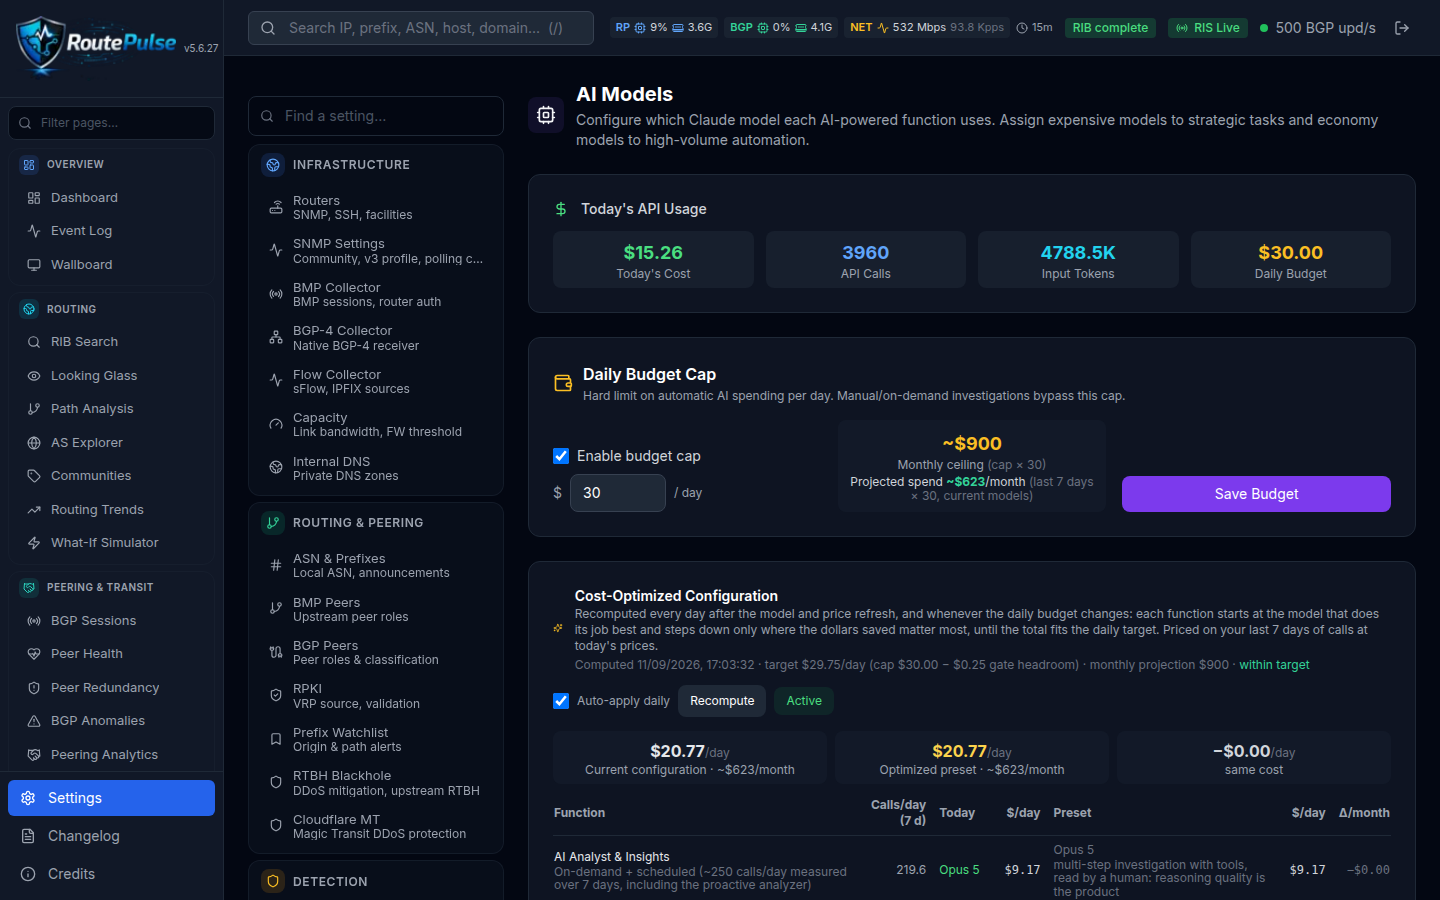
📚 Self-updating Model Catalog
Current Claude models and official prices read daily; every selector, preset and cost estimate follows, retired models resolve to their successor.
💰 Cost Optimizer & Budget Cap
Ideal-to-floor models per function fitted to your daily cap, re-fitted when prices move, with a hard circuit-breaker and a tool firewall.
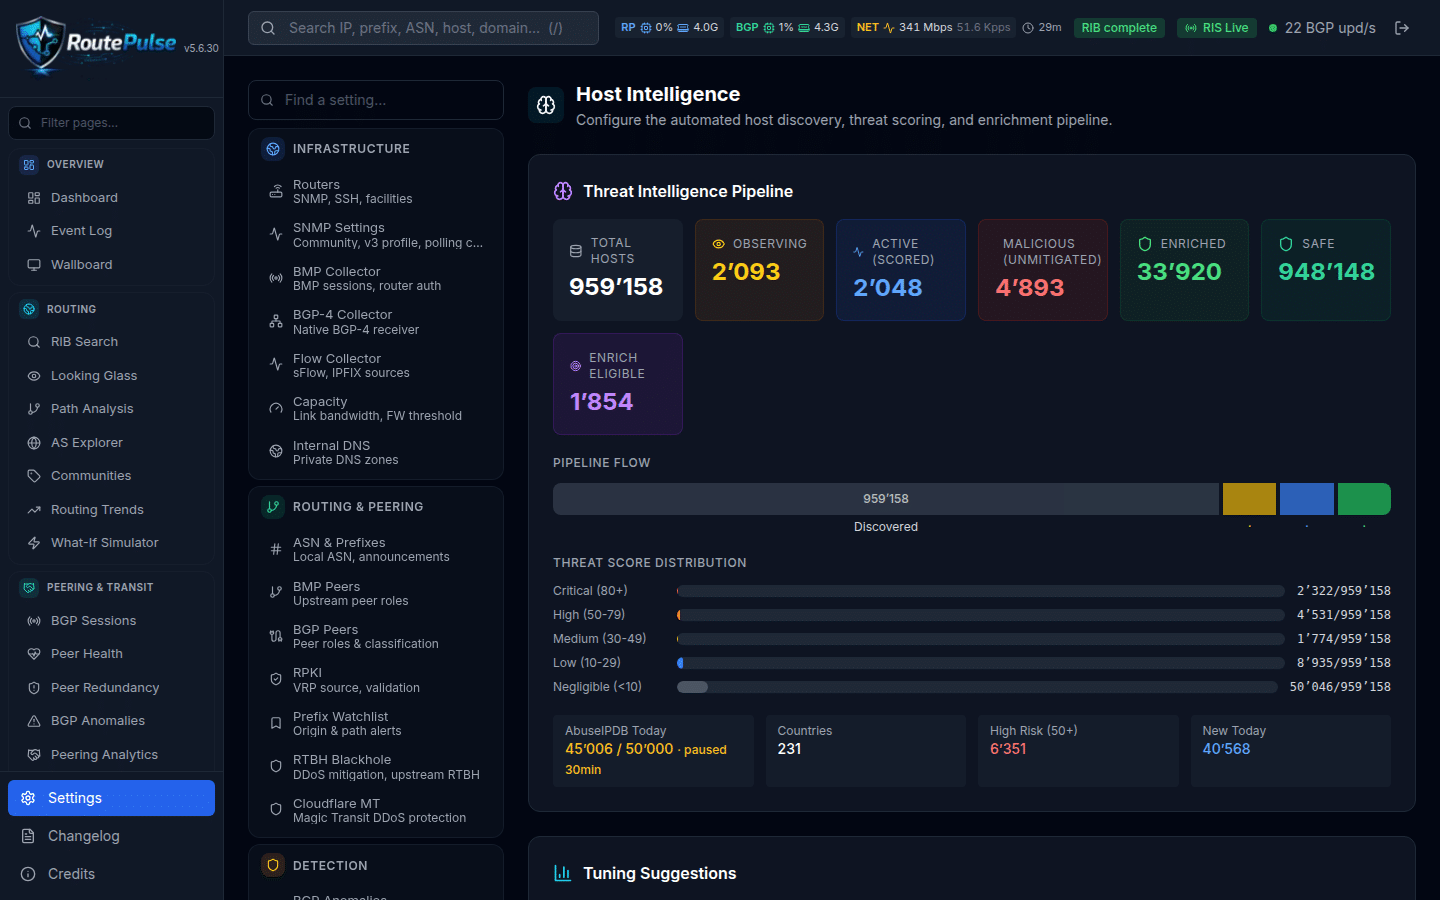
🎚️ Two-tier Host Assessment
A fast model for the bulk, a stronger second opinion only when a verdict would change a host’s status — 3,200 assessments a day for about $11.
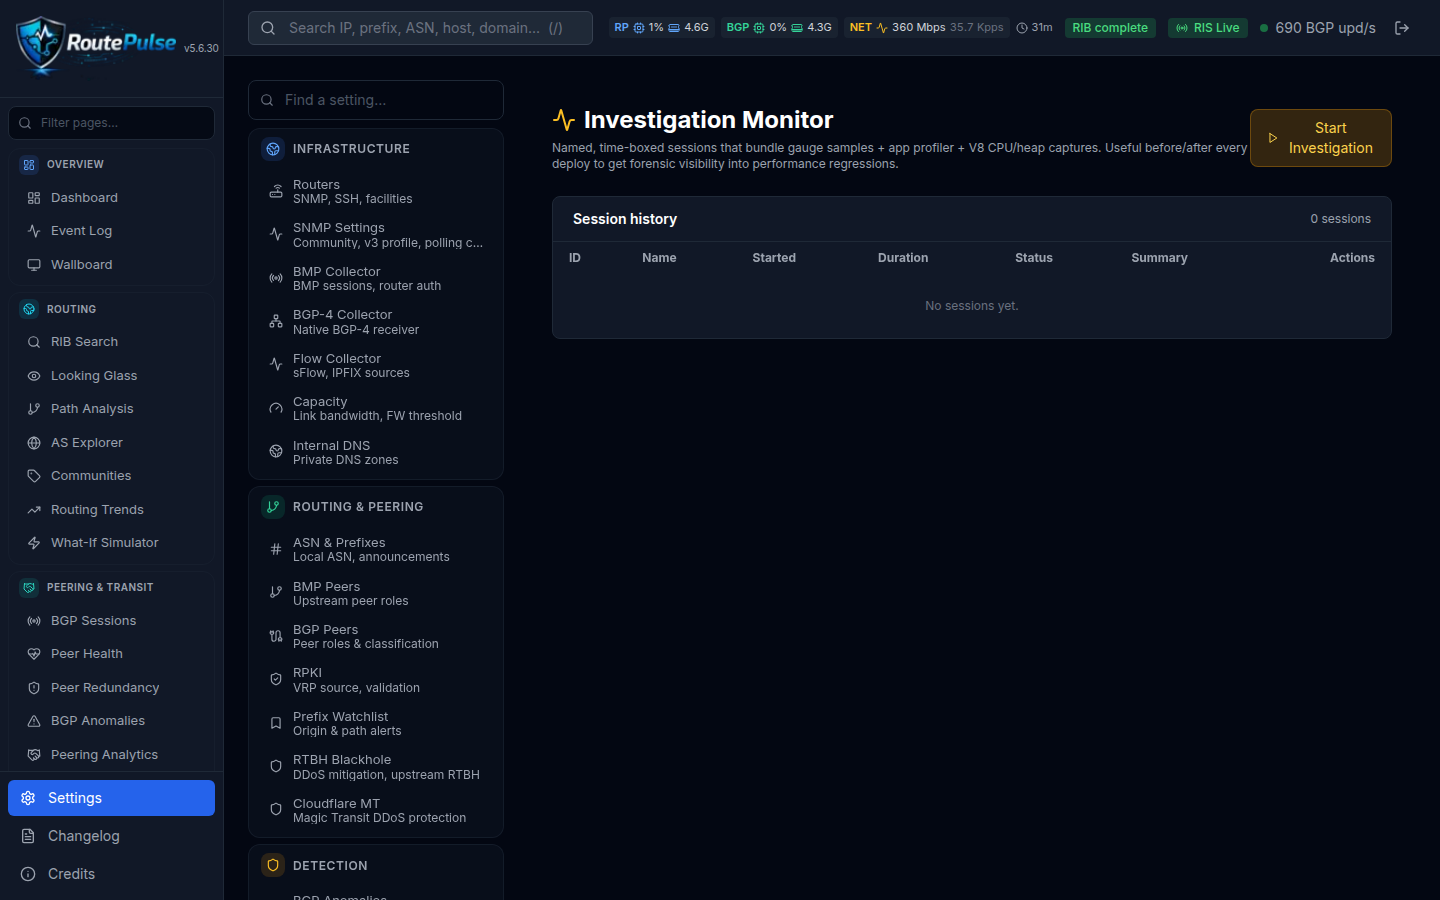
📟 Prometheus, Grafana & Alertmanager
132 metrics, 75+ rich alert templates to Telegram, a profiler with on-demand CPU profiles and heap snapshots.
🔌 Public REST API & MCP Server
/api/v1 with API keys and rate limits, an MCP server for AI integration, scheduled reports and RBAC.
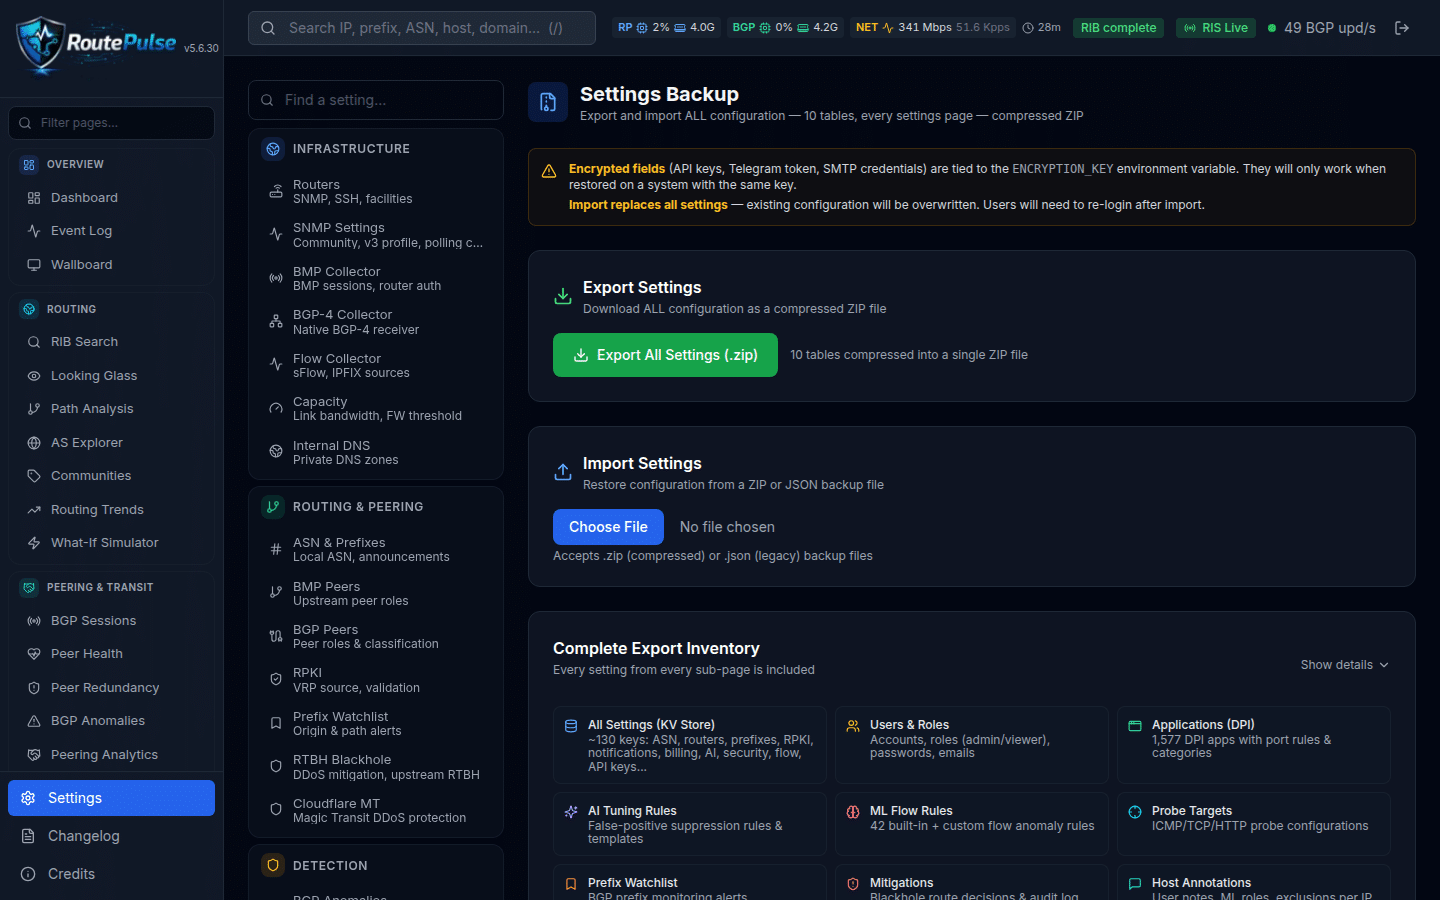
🗄️ Backup, Retention & Data Epoch
Settings backup and restore, retention per table, and a data epoch that marks the day the flow history became comparable.
Integrations & SIEM
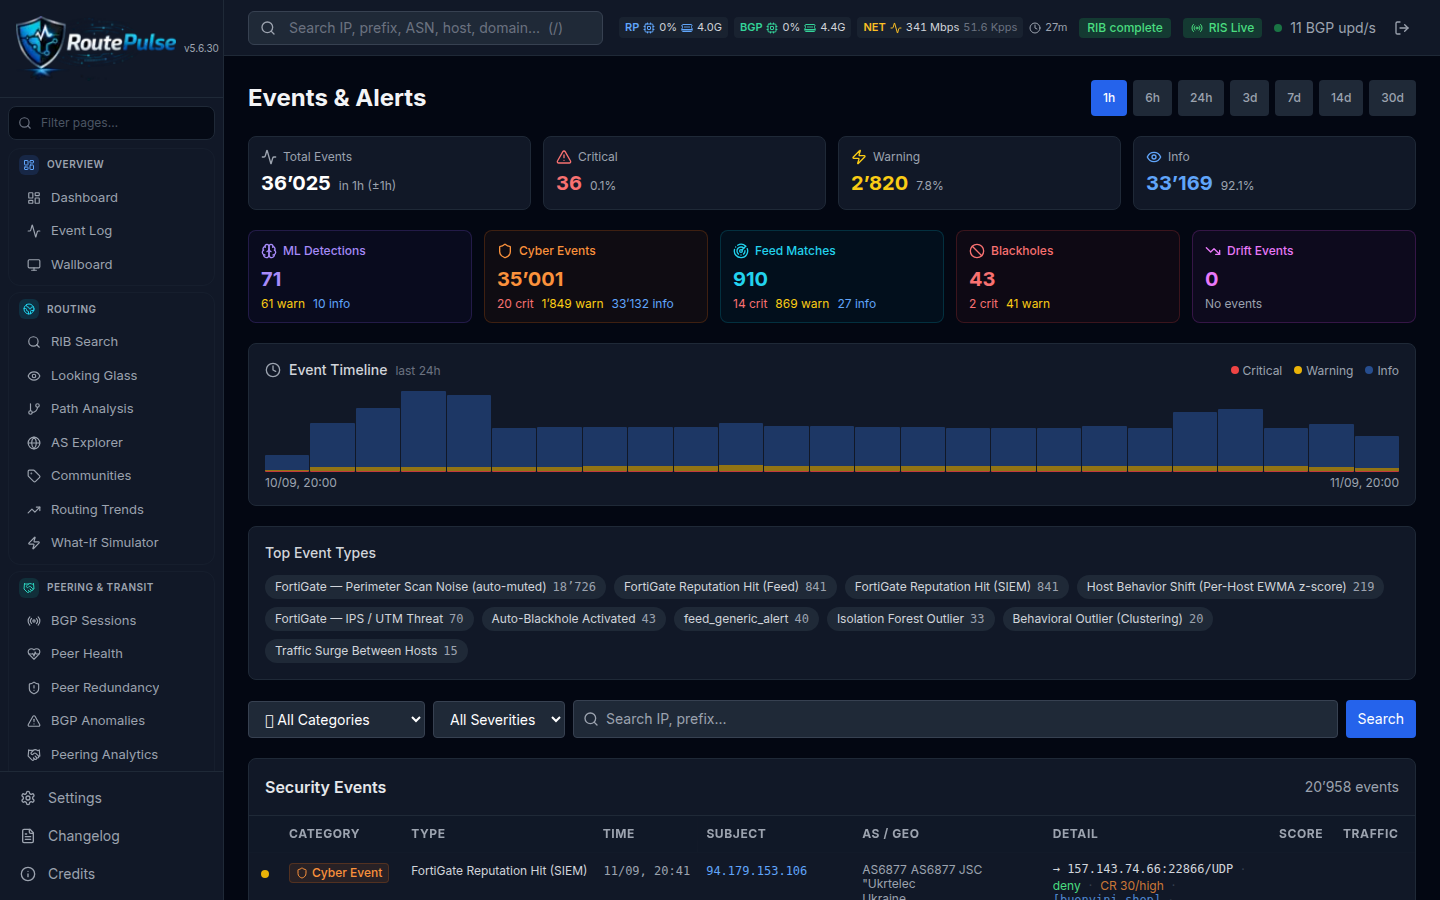
🧩 34-vendor SIEM convergence
Wazuh, Suricata, FortiGate IPS/UTM/AV/web/DoS, cPanel/Imunify360, Cisco FMC and more — auto-discovered, normalised, scored.
🧱 Firewalls as sensors and actuators →
FortiGate rich attack context and FortiAnalyzer, Cisco FTD threat detection and shuns managed by RoutePulse, Kemp LoadMaster WAF.
🌍 PeeringDB, CAIDA, RIPE, MaxMind
AS relationships, IXP presence, RIS Live, GeoIP2 and whois enrichment behind every AS and every host.
📣 AbuseIPDB, Shodan, Telegram, Webhooks
Reputation checks and auto-reporting, exposure data, and notifications to Telegram, Slack, Discord and PagerDuty.
Pricing & Value
🟢 Starter — €6,480 one-off
1 ASN · small fleet · core BGP + traffic + cyber + NIS2.
🔵 Professional — €19,480 year 1, then €4,490/yr
Full platform · NOC + SOC + AI + mitigation + compliance. Replaces roughly €85K/yr of tooling on a mid-size ISP (Crosswork, IDS operations, monitoring).
🟣 Enterprise — €38,980 year 1
Large fleet · priority support · custom integrations.
⚖️ Where it lands (mid-tier, year 1)
Kentik $120,000+ · Cisco Crosswork $72,000 · ThousandEyes $150,000+ · FastNetMon ~$3,588 (DDoS only) · DIY stack ~€40,000 of engineer time — every year. RoutePulse: €19,480 once, €4,490 from year 2, on hardware you own.
One platform vs. four vendors
| Capability | RoutePulse | Kentik | Cisco Crosswork | FastNetMon | Wazuh/Splunk |
|---|---|---|---|---|---|
| BGP + flow + RPKI/ASPA | ✓ | ✓ | partial | ✗ | ✗ |
| Capacity + transit-cost modelling | ✓ | ✓ | ✗ | ✗ | ✗ |
| Peering intelligence + IXP / LoA | ✓ | partial | ✗ | ✗ | ✗ |
| Cyber scoring + SIEM + AI | ✓ | ✗ | ✗ | DDoS | SIEM only |
| Auto-mitigation (RTBH / FlowSpec) | ✓ | ✗ | ✗ | ✓ | ✗ |
| Credential & campaign defense (mail · VPN · FTP · origin AS) | ✓ | ✗ | ✗ | ✗ | detect only |
| Router config-integrity | ✓ | ✗ | ✗ | ✗ | logs only |
| Government CTI at the source (CISA AIS) | ✓ | ✗ | ✗ | ✗ | ✗ |
| Published detection accuracy (AUC) | 0.994 | ✗ | ✗ | ✗ | ✗ |
| NIS2 / DORA / AI-Act built-in | ✓ | ✗ | ✗ | ✗ | ✗ |
| On-prem · data sovereignty | ✓ | ✗ | ✗ | ✓ | varies |
| Scope of the licence | NOC + SOC + compliance | observability | BGP monitoring | DDoS only | log SIEM |
| Price (mid-tier / year) | €19,480 Y1 · €4,490/yr after | $120K+ | $72K | ~$3.6K | $$$ |
Only RoutePulse covers the NOC and the SOC in one line item — and it is the only one of the five that ships the conviction engine, self-defending routers, credential-attack defense and built-in EU compliance. Published list prices, mid-tier, year 1.
Built for Enterprise
Bloom filter, 52K+ indicators
Automated mitigation response
Four-tier resolution chain
Materialized views, optimized storage
From $282/day to $1-3/day
Zero packet loss ingestion
500 features, 136 pages, 67 tRPC routers, 1,156 endpoints. Designed and built entirely in-house. High-performance binary protocol parsers, columnar analytics engine (44 ClickHouse tables — 35 base + 9 materialised views, 1.6B+ rows), real-time streaming architecture, 18-model ML ensemble with adaptive learning and CAD compositional anomaly detector (90% noise reduction on multi-modal hosts), 8-Gate Conviction Engine (SPRT + Thompson Sampling + Conformal Prediction with provable FDR bounds), 47 MITRE ATT&CK playbooks with agentic AI response (ANIE 6-layer Claude pipeline, €1–3/day spend), and native SIEM integration (Wazuh + Suricata IDS + FortiGate IPS with rich attack-context panels). AES-256-GCM encryption at rest, RBAC access control, WORM cryptographically-chained audit trail (append-only hash chain), NIS2 / DORA / AI-Act compliance dossier generator with Ed25519 signed manifests + SHA-256 hash-chained audit entries, public QR-scannable Letter of Authorization verifier.
Built for AS202032
RoutePulse is engineered and operated by the GOLINE SOC team — providing 24/7 BGP analytics, threat intelligence, and automated defense for our network infrastructure.
Visit RoutePulse Try the Public Looking Glass