
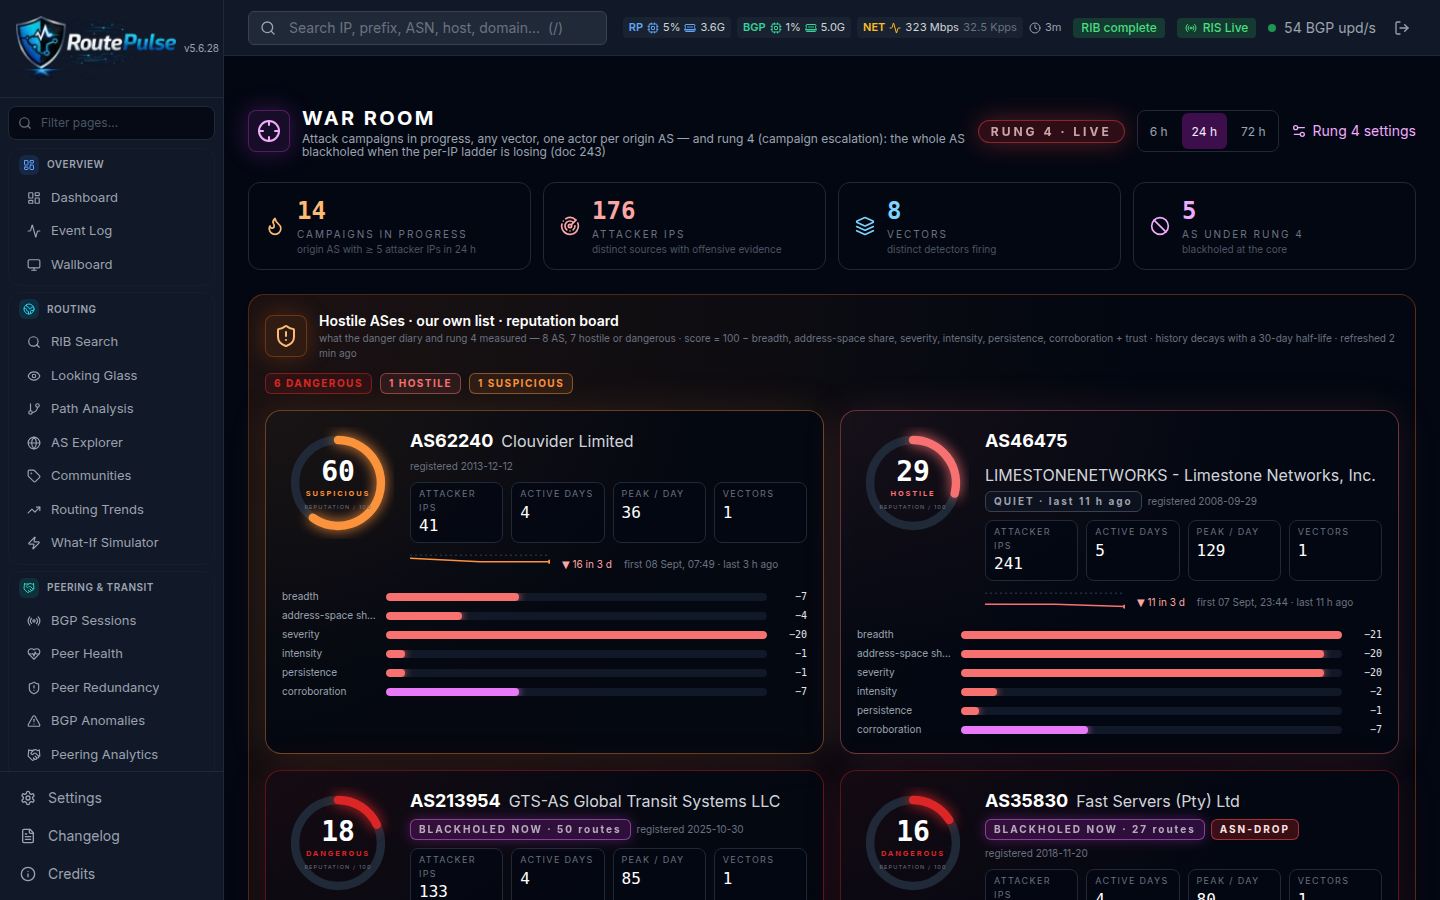
War Room — Every Attack Campaign as One Actor, and the Fourth Rung: the Whole AS Blackholed
A rented proxy network does not attack from an IP: it burns hundreds of single-use addresses across every prefix it announces, three to five attempts each, so that any per-IP response arrives after the address has already been discarded. The War Room shows every attack campaign in progress on any vector — VPN, Exchange, FTP, malware push, WAF — grouped by origin AS from the live BGP RIB, with its vectors, its /24 spread, its burn rate and how much of it the per-IP ladder has already mitigated.
When a campaign is massive — spread across the AS, fresh IPs arriving every minute, the per-IP ladder demonstrably losing — and six independent safety gates are green (no recurring traffic relationship with the AS in 30 days, no successful login from it on any service, not a protected network, not too large, corroborated by Spamhaus ASN-DROP, no history with us), RoutePulse treats the AS as the attacker: every prefix it announces is blackholed as announced, discard-only on the core routers, never propagated upstream, renewed while the campaign lasts and released after it ends. The hive of announced /24s, the strength gauges, the gate ring and the blocked-AS ledger show the operator exactly why, and a single click releases it.